Security and Compliance Basics
Stop Assuming Your Systems Are Secure. Start Knowing They Are.


Client Results and Success
Production-Ready Kubernetes Architecture
The platform was designed to support scalable production deployments with minimal resource consumption, enabling faster environment provisioning and operational stability.
3
environments K8s setup
95%
environments K8s setup
35%
savings over managed Kubernetes alternatives
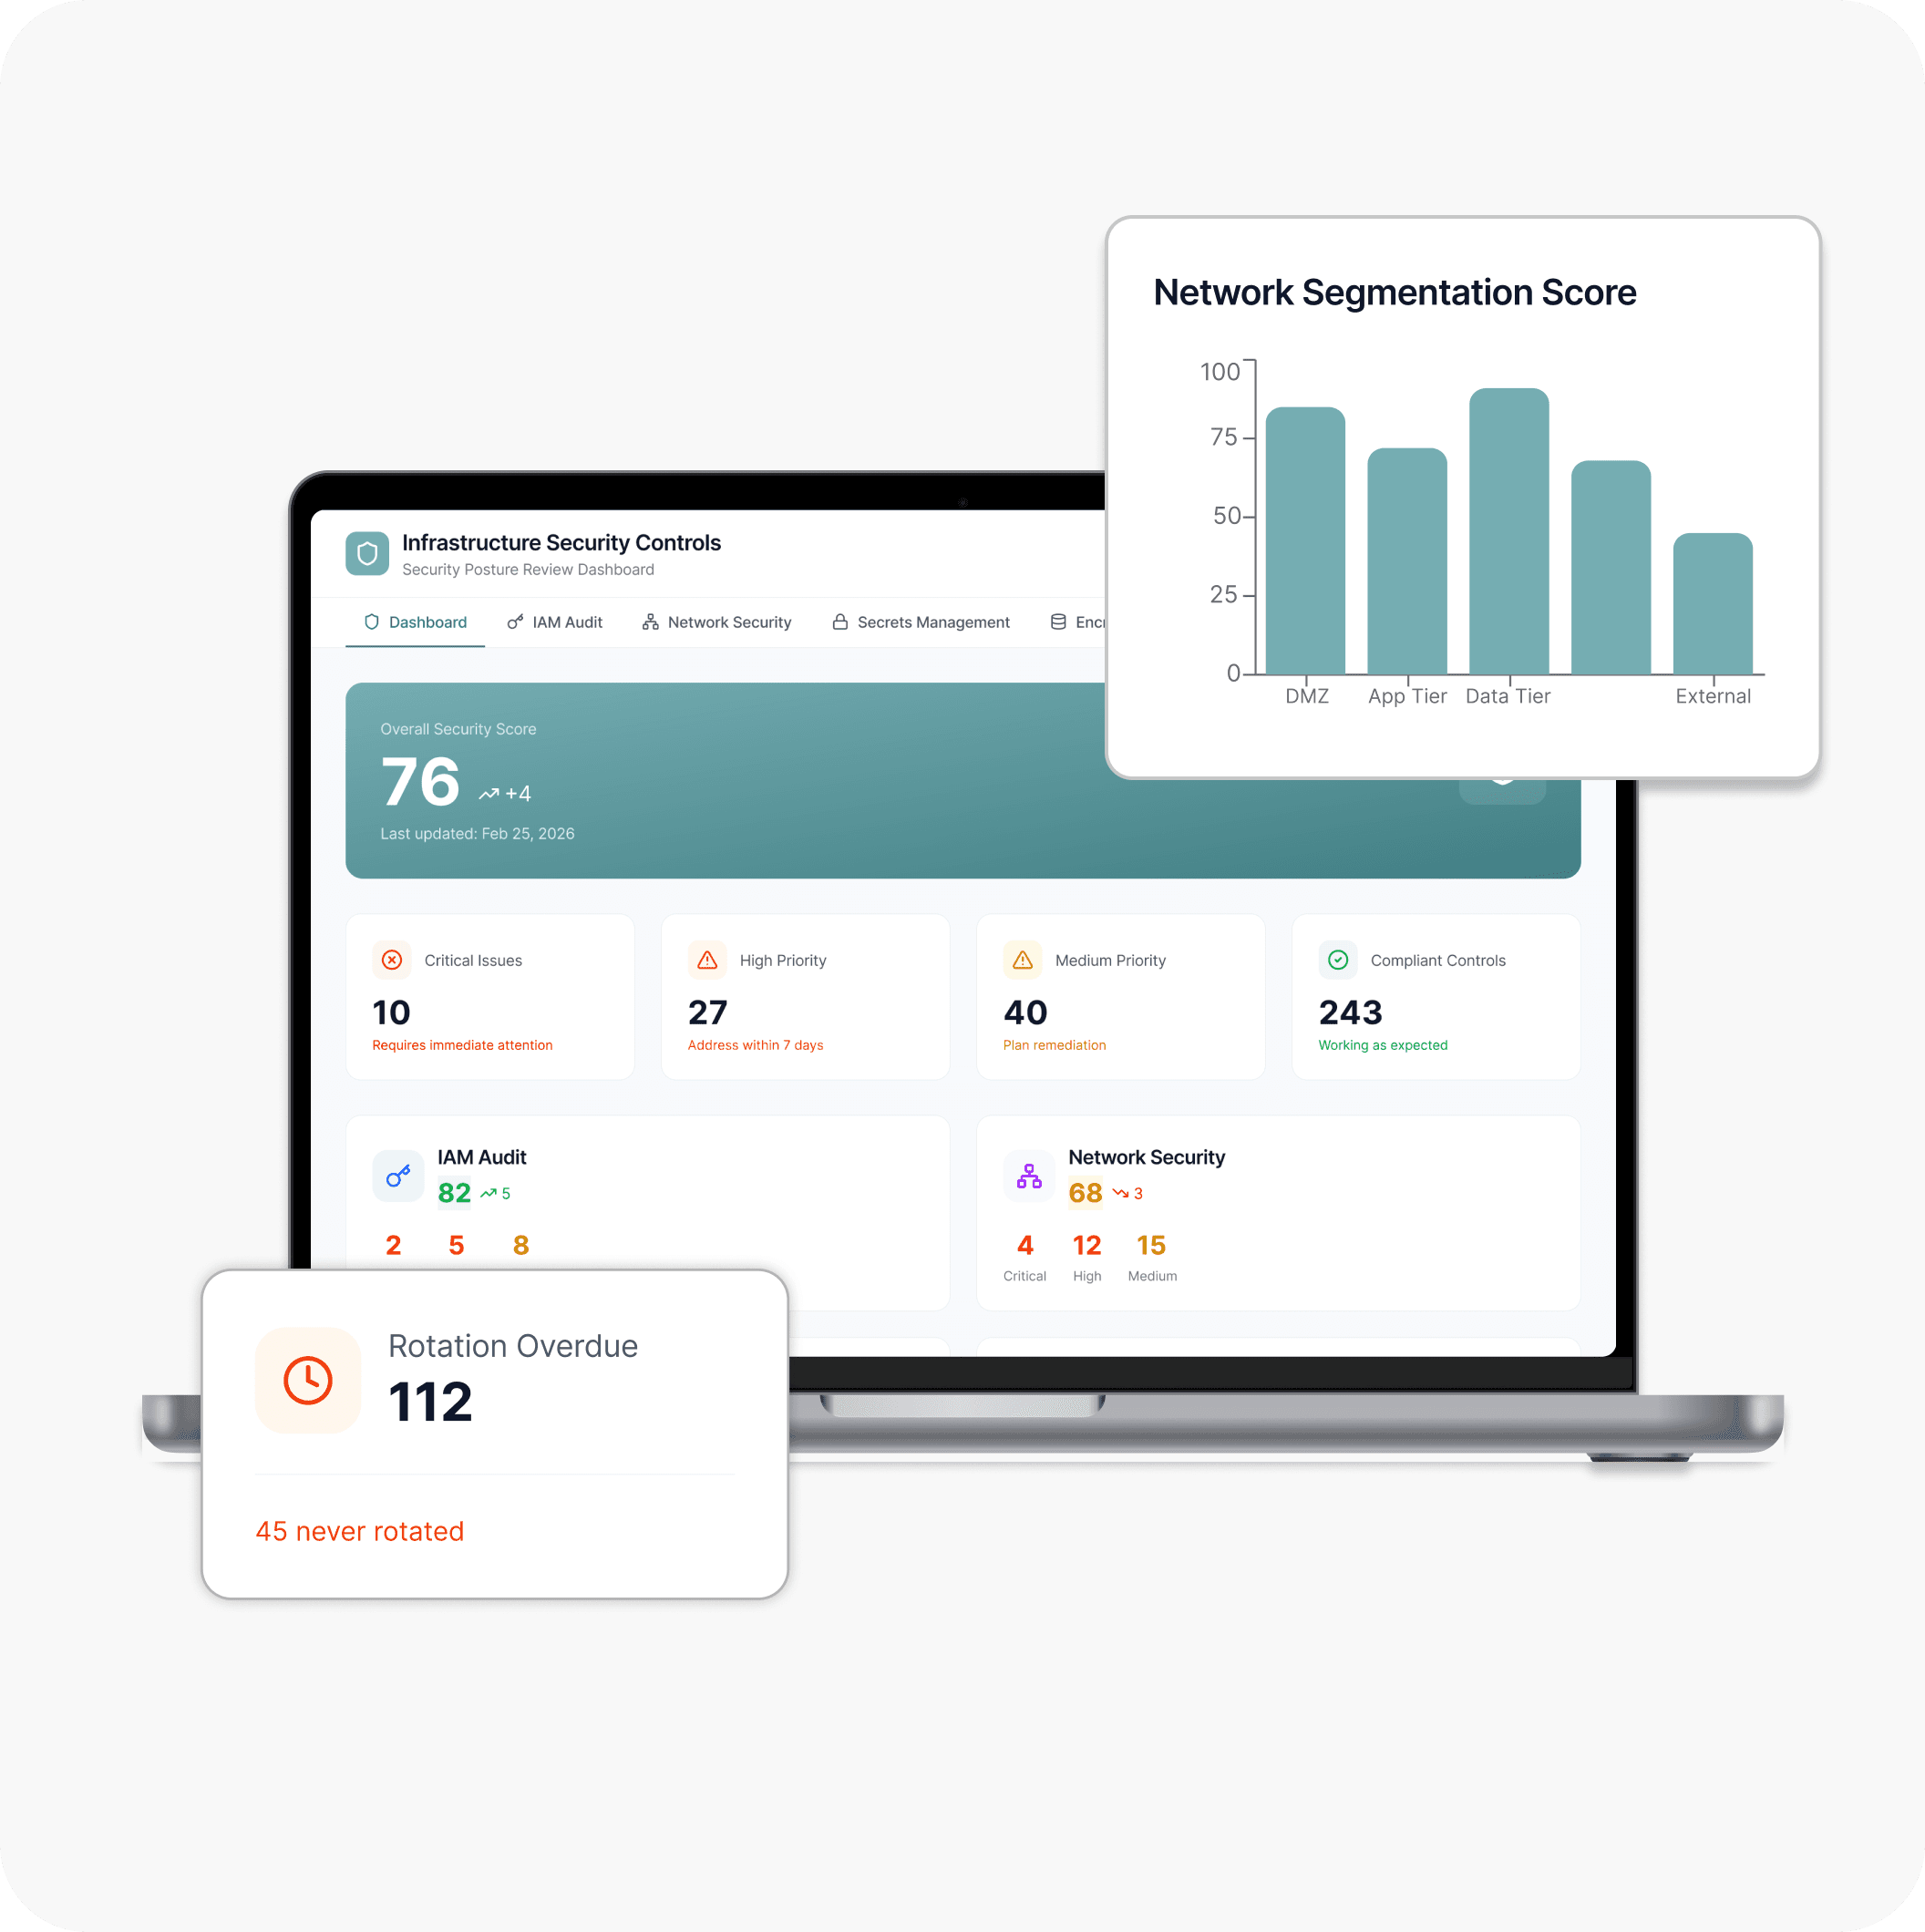
Our Security Assessment Examines Three Foundational Dimensions
- Identity and access management audit: IAM role assignments, privilege escalation paths, service account permissions, and cross-account access configurations
- Network security assessment: Security group rules, firewall policies, publicly exposed endpoints, and internal network segmentation adequacy
- Secrets and credential management: Hardcoded credentials identification, secrets rotation policies, vault configuration, and environment variable exposure risks
- Encryption coverage review: Data at rest encryption configuration, transport layer security implementation, and key management practices
- Authentication and authorization review: Session management, token handling, API authentication mechanisms, and broken access control identification
- Dependency and supply chain security: Third-party library vulnerability exposure, container image scanning coverage, and software bill of materials visibility
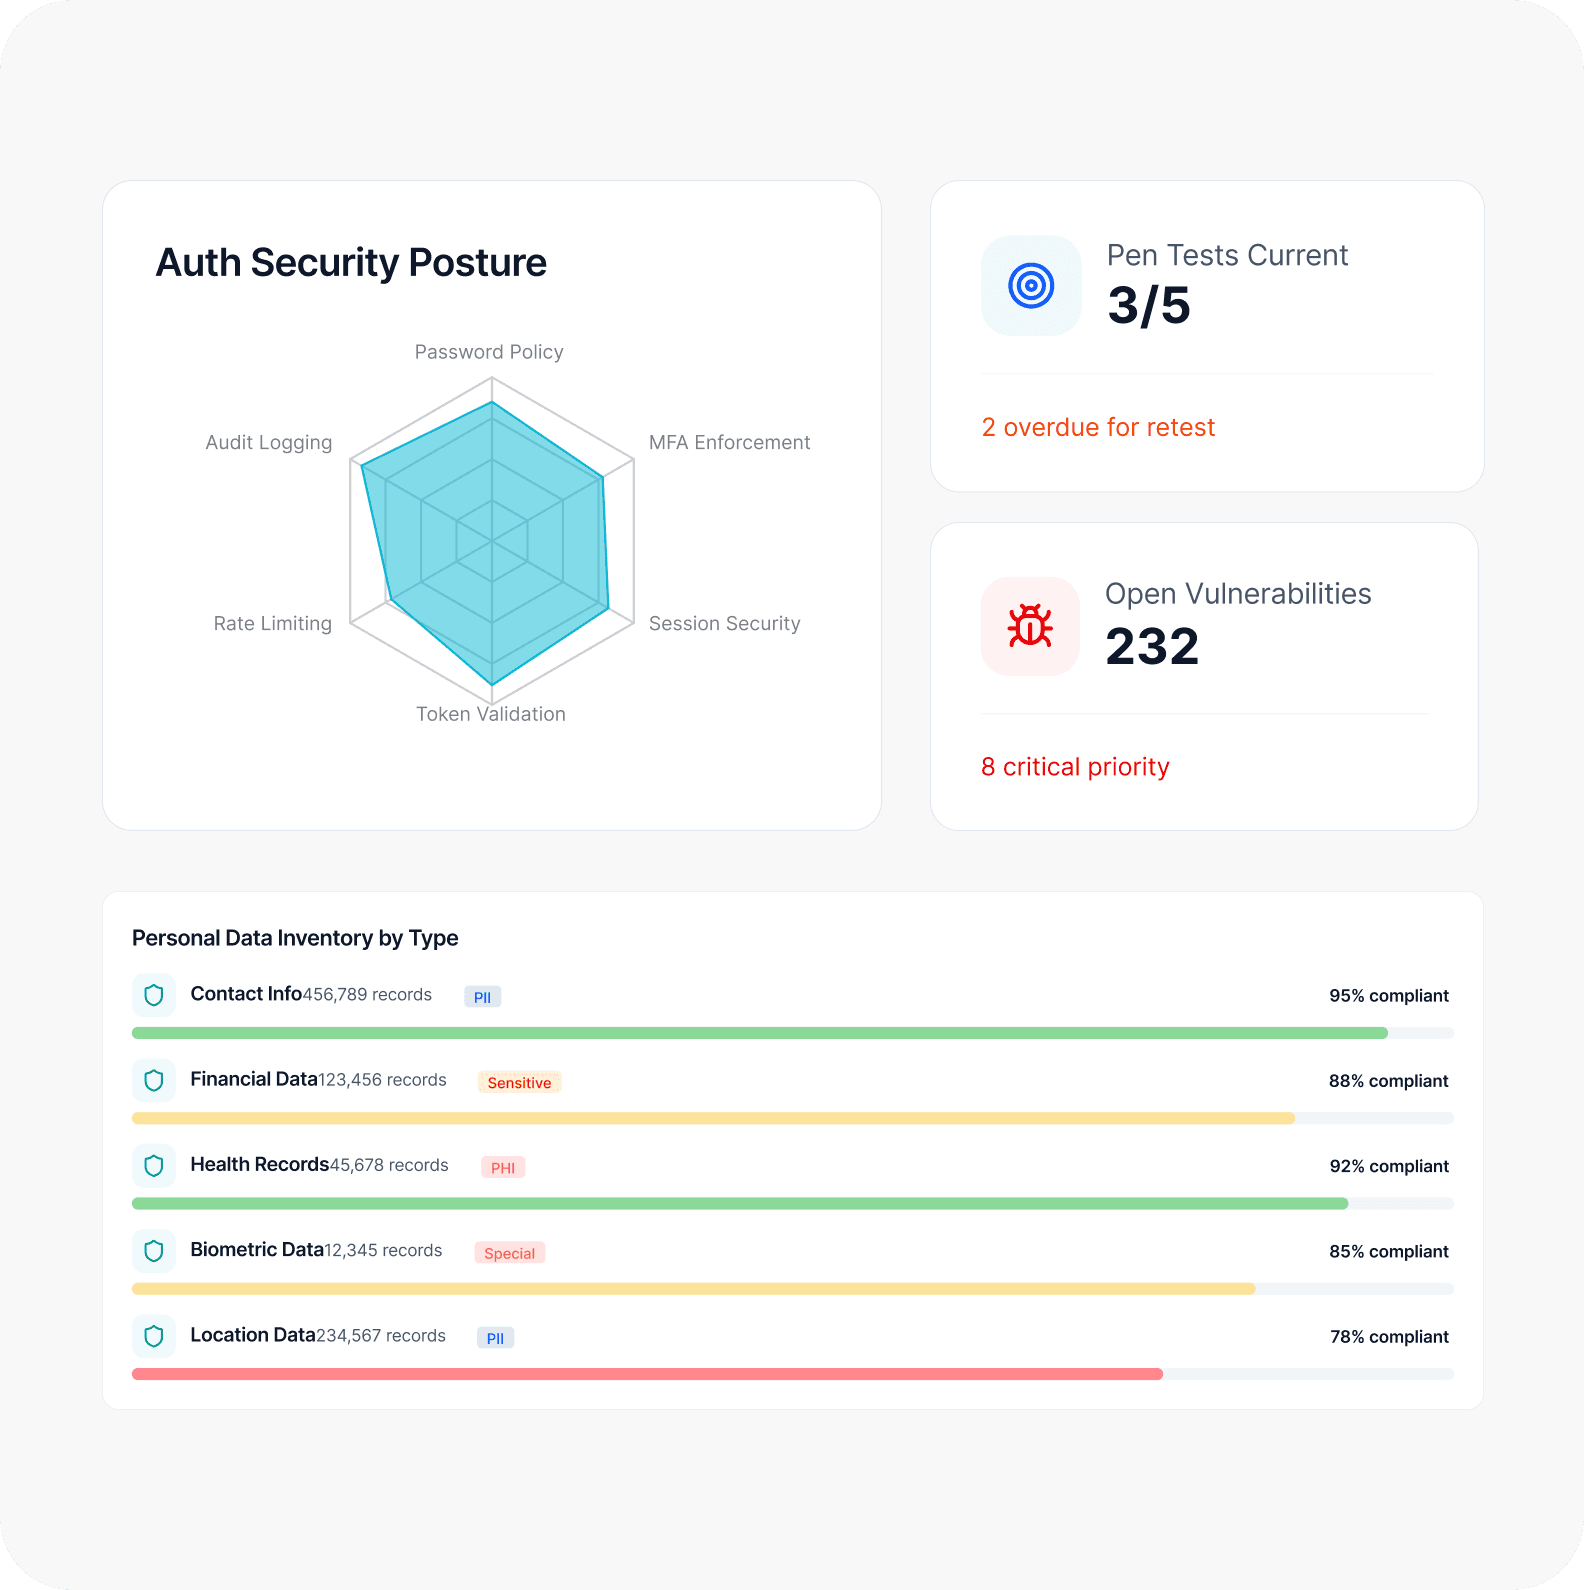
- Data classification and handling audit: Personal data inventory, retention policy enforcement, cross-border transfer controls, and data minimization practices
- Security testing integration: SAST and DAST tooling coverage, penetration testing currency, and vulnerability remediation tracking effectiveness
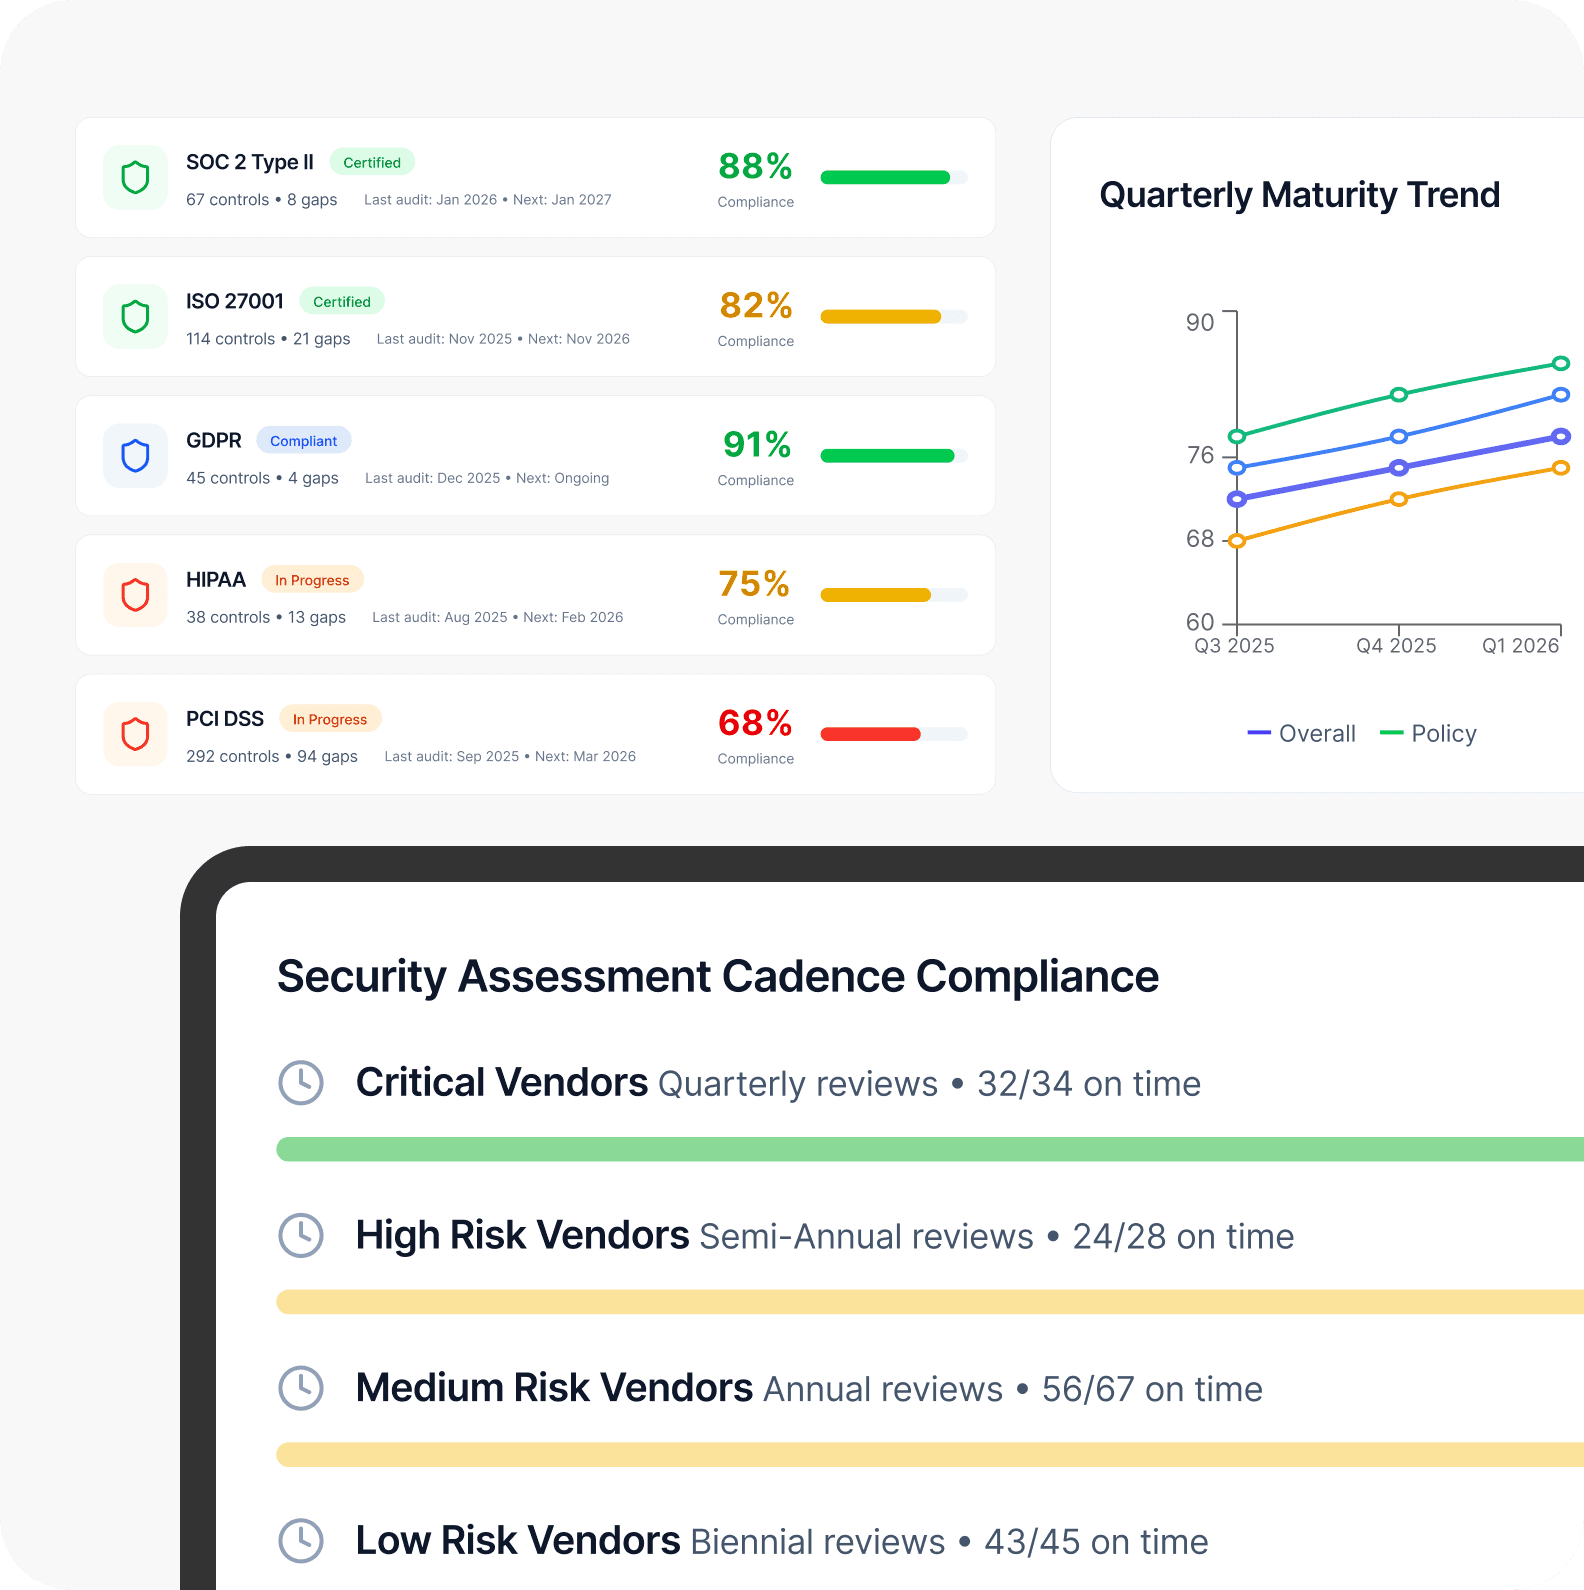
- Regulatory framework mapping: Gap analysis against applicable standards, including SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS based on your business context
- Control documentation assessment: Policy completeness, evidence collection maturity, and audit readiness against your target compliance frameworks
- Vendor and third-party risk: Supplier security assessment practices, data processing agreement coverage, and fourth-party risk visibility
- Security governance maturity: Ownership accountability, security review processes embedded in delivery workflows, and board-level risk reporting adequacy
Security Outcomes We Are Accountable For Delivering
Know Your Actual Security Posture, Not Your Assumed One
Win Enterprise Customers Without Security Reviews Derailing Deals
Protect Customer Data With Controls That Were Designed, Not Accumulated
Meet Regulatory Requirements Before They Become Enforcement Actions
Industries Across Which We Deliver Security and Compliance Impact


Security Assessments Delivered by Engineers Who Have Hardened 1000+ Production Environments
Our Offerings in DevOps Consulting and Services
Our Latest Thinking
AI Compliance in the United States: A Practical Guide to Governance, Risk, Documentation, and Audit Readiness
A practical guide to AI compliance in the United States, covering governance, risk management, lifecycle controls, documentation, audit readiness, and implementation.
AI Governance Framework for Enterprises: Policies, Roles, Controls, Metrics, and a 90-Day Roadmap
Learn how to build an enterprise AI governance framework covering policies, risk classification, roles, technical controls, metrics, compliance, and a practical 90-day implementation roadmap.
How Should a US Company Work with an Offshore Engineering Partner Across Time Zones
A practical guide to choosing, managing, and scaling an offshore engineering partner across time zones.
AI Reference Architectures for Fintech and Banking: 5 Production-Ready Patterns, Costs, and Risks
Explore five production-ready AI reference architectures for fintech and banking, covering AI controls, costs, failure modes, and deployment considerations.
AI Project Manager: How AI Can Track Tasks, Risks, Blockers, Dependencies, and Deadlines
A practical guide to AI project managers: what they track, how to implement one safely, and how to evaluate the options.
From Rolling Deployments to Zero-Downtime Releases
This blog explains how Blue-Green deployment helps reduce downtime in online banking releases through traffic switching, pod readiness, static-resource versioning, and rapid rollback.
