

Key Takeaways
- Build an AI governance framework that connects the policies, risk, ownership, technical controls, and monitoring.
- Classify AI systems by risk so that the high-impact use cases receive stronger testing and review processes.
- Implement corporate AI governance in 90 days by moving from visibility and policies to controls, monitoring, and reporting.
- Track governance coverage, unresolved risks, AI system performance, and remediation times to give executives a view of how the governance program is performing.
Picture a product team preparing to launch an AI assistant for customer support, the model has been tested, the product team is happy with the responses, and the launch date is on the calendar.
And then someone in the legal team asks questions about customer data privacy and accessibility.
Questions like these can likely pause product launches much faster than a failed evaluation of the model.
This is where the enterprise AI governance framework brings a difference, as enterprises today have to account for traditional ML models, GenAI applications, third-party AI features, and agents that can access systems and take the right action.
The market reflects how quickly this problem is increasing, as the Grand View Research estimates that the global AI governance market will reach $3,497.3 billion by 2033, up from $539.5 billion in 2026, which represents a 30.6% CAGR from 2026 to 2033.
From a business perspective, an artificial intelligence governance framework becomes important when AI begins to influence decisions, customer experiences, or day-to-day operations. Teams need to understand what an AI system can access, what it is allowed to do, and who is responsible for its outcomes. That clarity helps organizations adopt AI with confidence while keeping business and regulatory risks in view.
 Varun Kumar SahuChief Digital & Privacy Officer
This guide lays out that operating model, from the foundations of enterprise AI governance to the controls needed for AI agents that can take actions on their own. The goal is to give enterprises a way to scale AI while keeping responsibility visible at every step.
How Does an Enterprise AI Governance Framework Work?
An enterprise AI governance framework provides organizations a structured way to decide if an AI system can be deployed, prepare standards for the required level of review, assign ownership of risk, establish the evidence before launch, and set the process for handling issues after deployment. It is useful for answering questions that come up once an AI prototype is taken from experimentation to production. Some of the important questions are, like, can this be deployed? What level of review does it need? Who owns the decision? What evidence is required before launch? What happens if the system starts producing results that are not very safe or reliable?
The framework connects different policies, decision rights, risk controls, technical safeguards, and visibility, which therefore gives the teams a shared set of rules without asking every AI project to repeat the same rule again and again.
A hiring model, for example, may need fairness testing and documented approval before deployment takes place. A GenAI assistant connected to customer records may need stricter data controls and access limits. An AI agent that can place orders or update records may need human approval before it performs certain actions.
It is also useful for separating responsibilities that often risk getting mixed up together.
- AI Security: AI security focuses on protecting AI systems, models, interfaces, and data from threats such as unauthorized access, prompt injection, or model theft. Governance determines which systems are permitted, who is accountable for them, and what control standards need to be met.
- AI Ethics: AI Ethics establishes principles around issues such as fairness, transparency, and human impact. Governance turns those principles into decisions, policies, reviews, and controls that teams can apply.
- IT Governance vs. AI Governance: IT governance covers technology decisions across the organization while AI governance deals with risks that require AI-specific oversight, including model behavior, training data, explainability, bias, generative AI outputs, and changing model performance.
- Responsible AI: Responsible AI describes the outcome an organization wants, an AI system that people can use with confidence and accountability. Governance provides the structure for achieving and demonstrating that outcome.
What are The 6 Core Components of an Enterprise AI Governance Framework?
A useful enterprise AI governance framework should include six components that align governance decisions with risk management, ownership, controls, evidence, and monitoring across the AI lifecycle process.
AI governance has to work at the same pace as the system it governs. A policy alone does not tell an engineering team when a model needs review or give leadership visibility into a system after it goes live. The governance model needs clear ownership, practical controls, and a way to act when the risk or behavior changes.
Varun Kumar SahuChief Digital & Privacy Officer1. AI Governance Policies and Standards
AI governance best practice includes policies that set the boundaries before individual teams start making their own rules. These should cover:
- Acceptable AI Use: AI applications that are allowed, restricted, or prohibited.
- Data and Privacy: Data that will be used for training, prompting, retrieval, or fine-tuning, and under certain conditions.
- Model Development and Deployment: Testing, validation, documentation, and approval process required before releases.
- Third-Party APIs: Vendors need to disclose about models’ data handling, security updates, and subcontractors.
- Generative AI: Tools to be used by employees, systems to be accessed by agents, and actions requiring approvals.
- Human Review: A person reviewing or overriding an AI-generated recommendation or action.
- Managing Incidents: The team that needs to be notified when an AI system causes security, privacy, compliance, or performance issues.
- Documentation and Audit: Evidence that must be retained to show how a system was assessed and approved.
2. AI Risk Classification
An AI governance risk model prevents two common problems, which include sending every AI experiment through the same approval process and giving a high-impact system the same review as a low-impact tool. A practical starting point includes a four-tier model:
Risk Tier | Typical Use | Approval and Control Expectations |
Low | Internal search, summarization, basic productivity tools | Standard policy checks, owner assignment, basic monitoring |
Medium | Customer support, business workflow automation, internal decision support | Business and technical review, data checks, evaluation, and documented approval |
High | Credit, hiring, healthcare, legal, or other consequential decisions | Formal risk review, stronger testing, security assessment, human oversight, continuous monitoring |
Prohibited | Uses that violate law or the organization’s defined restrictions | Do not deploy; escalate exceptions through the appropriate governance authority |
3. Roles, Responsibilities, and Decision Rights
A governance committee as well as the team has to own the decision when a model is either approved, changed, paused, or retired. An enterprise structure can include:
- Executive Sponsor: Sets the organizational risk appetite and provides senior-level authority.
- AI Governance Committee: Reviews higher-risk use cases and resolves cross-functional decisions.
- AI Governance Lead: Runs the governance process, maintains standards, and tracks exceptions.
- Model/System Owner: Owns the AI system and its performance, risk, and lifecycle.
- Engineering/Platform Owner: Maintains the technical environment, deployment controls, and operational safeguards.
- Security: Assesses threats, access, vulnerabilities, and AI-specific attack paths.
- Legal/Compliance: Interprets regulatory and contractual obligations.
- Data Governance: Oversees data quality, lineage, privacy, and permitted use.
- Business Owner: Owns the business purpose, expected outcome, and acceptance of business risk.
Activity Executive | Executive | Governance | System Owner | Engineering | Security | Legacy/Compliance | Business |
Approve high-risk AI | A | R | C | C | C | C | C |
Risk classification | I | A/R | R | C | C | C | C |
Technical testing | I | C | A | R | R | I | I |
Production release | I | C | A | R | C | C | C |
Incident response | I | A | R | R | R | C | C |
Periodic review | I | A/R | R | C | C | C | C |
R = Responsible, A = Accountable, C = Consulted, I = Informed
4. Technical Controls
A policy becomes useful when technology can enforce it. Technical controls should follow the AI system through development, deployment, and runtime.
- Before Deployment: Teams should validate data, evaluate model performance, test for bias where relevant, assess security, and red-team higher-risk systems. The required depth should depend on the system’s risk tier.
- During Deployment: AI governance models should include approval gates, identity and access management, model or AI asset registries, version control, and audit logging. A deployment should have enough recorded evidence to reconstruct the process that was approved, the version that was released, and the ones who approved it.
- Runtime: Output controls need to be aware of what operations are taking place in the system. Depending on the use case, this can include performance and data-drift monitoring, hallucination or output-quality checks, prompt-injection detection, sensitive-data and output controls, access monitoring, incident detection, rollback mechanisms, and kill switches for systems that can take consequential actions.
5. AI Inventory, Documentation, and Auditability
An organization must be able to cover internally developed systems, third-party AI, embedded vendor capabilities, and approved AI applications. The system should also provide a way to identify unmanaged or shadow AI wherever possible
For each AI system, businesses need to record about the system owner, business purpose, model and provider, data sources, risk tier, regulatory exposure, intended users and use cases, validation and approval status, required controls, monitoring metrics, last review date, changes made since the previous review, and incident history.
This becomes a reference point for risk reviews, audits, vendor assessments, and executive reporting.
6. Monitoring and Improving Governance
Approval will be the starting point as an AI system can change because its data changes, its model is updated, its prompts are modified, its users behave differently, or if there are shifts in its business context.
Monitoring should therefore cover performance, drift, bias, security, compliance, incidents, model changes, and policy changes. The exact metrics will depend on the use case and risk tier. The governance process should follow a simple loop:
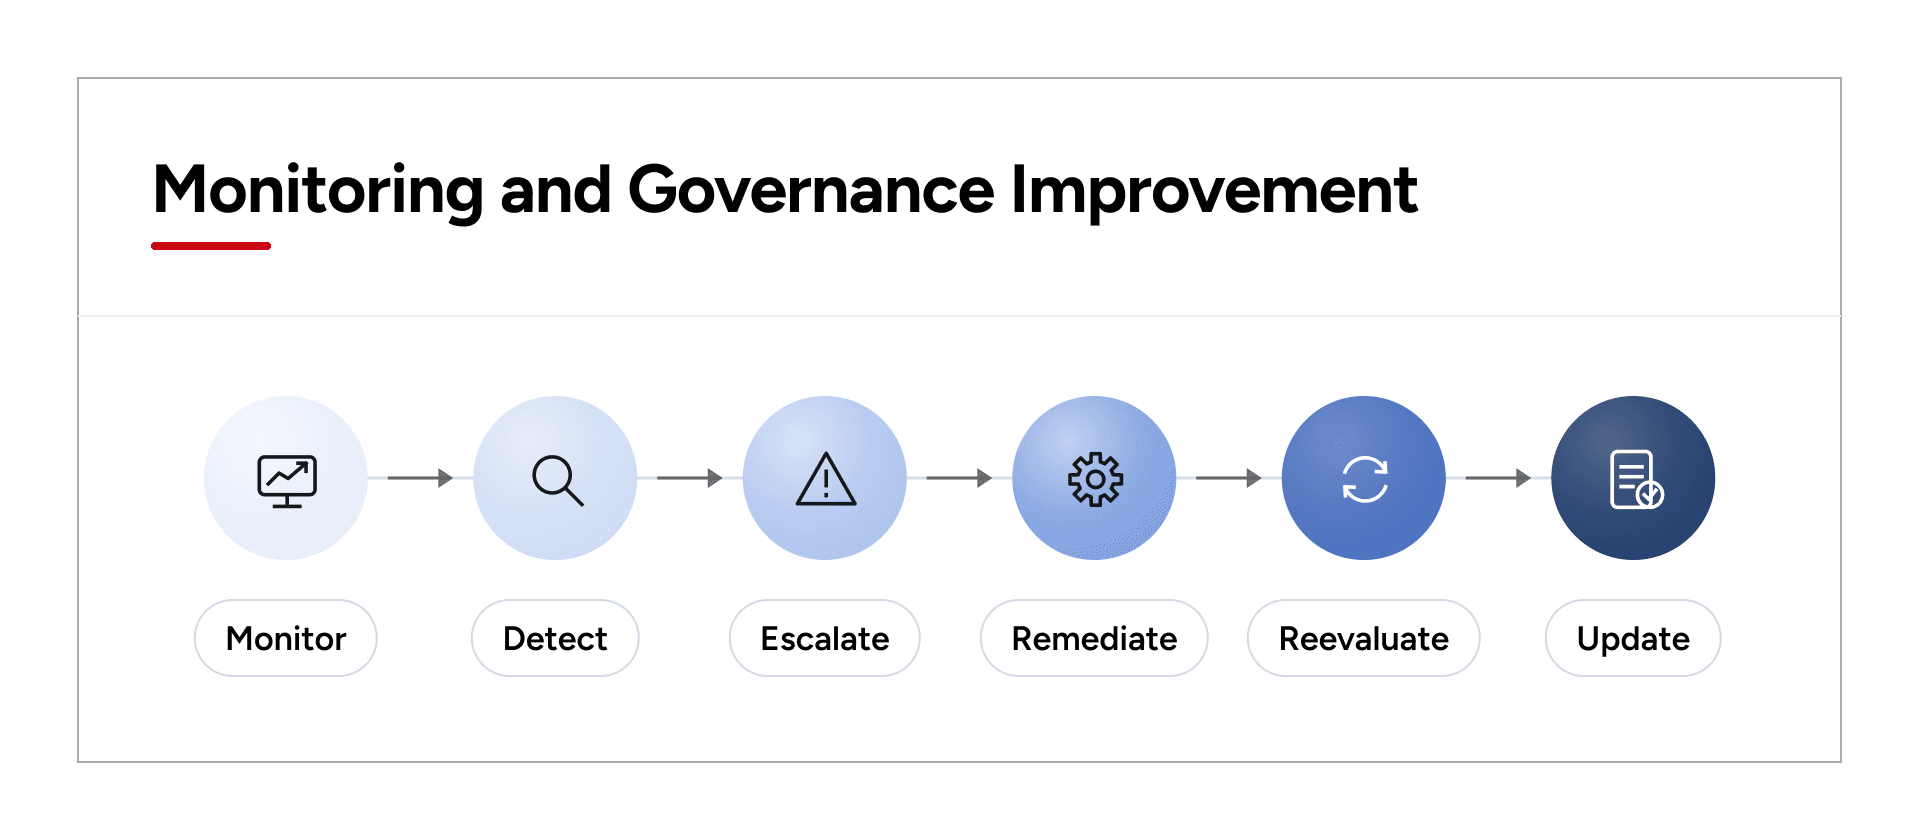
If a production model starts producing less accurate results, the monitoring system will detect a change, an issue will be escalated to the system owner, the team will investigate the cause, apply fix or rollback while reassessing the system against its approved thresholds, and update the documentation accordingly.
Which Enterprise AI Governance Metrics Should Be on the Executive Dashboard?
A useful enterprise artificial intelligence governance framework in an executive dashboard should connect governance activity with business risk. Executives should be able to see whether AI systems have owners, whether high-risk systems have the required controls, whether model behavior is changing, and how quickly teams respond when something goes wrong.
1. Which Governance Coverage Metrics Should Executives Track?
Executives can group AI Governance metrics into four areas:
Metric | What it Measures (Percentage) | Why Should Executives Track It? |
AI Inventory Coverage | Known AI systems recorded in the enterprise AI inventory | Shows whether leadership has visibility into the organization's AI estate. |
Owner Assignment | AI system with a named business and/or technical owner | Shows whether accountability exists for each system |
Risk Classification | Inventoried AI systems assigned a risk tier | Shows whether the organization knows which systems require greater scrutiny. |
Documentation Completeness | AI records containing required information such as purpose, data, sources, model/provider, controls, approvals, and review history. | Shows whether decisions can be understood and audited later |
All of the percentages measured here provide executives a proper picture in addition to ensuring that the governance program is “in place”.
2. Which Risk and Compliance Metrics Should Executives Monitor?
Risk and compliance metrics help teams in getting a proper understanding about the gaps that could lead to exposures in different operations. The core measures include:
- Open AI Risks: The number of identified AI risks that are not resolved, ideally split by severity and business impact.
- High-risk Systems: The percentage of high-risk AI systems missing mandatory testing, human oversight, security controls, etc.
- Compliance Exceptions: The number of approved deviations from policies or requirements, along with their age and risk level.
- Audit Findings: Open findings from internal, external, or other audits and identify the time period from which they have not been solved.
3. Which AI Model and System Performance Metrics Should Executives Consider?
AI behavior can change when data, users, prompts, business conditions, or connected systems change. An enterprise-ready AI governance framework software should therefore track:
- Drift: Whether input data or model behavior has changed from the expected baseline.
- Accuracy or Performance: Whether the system continues to meet its defined performance target for the intended use case.
- Bias: Whether performance differs across relevant groups where fairness is a material risk.
- Hallucination Rate: For GenAI systems, how often the system produces unsupported or incorrect information based on the organization’s defined evaluation method.
- Security Incidents: AI-related security events such as prompt-injection attempts that bypass controls, unauthorized access, sensitive-data exposure, or other confirmed incidents.
4. Which AI Governance Metrics Should Executives Measure for Maintaining Efficiency?
Operational metrics help leadership check whether the AI governance implementation is being carried out at the right speed and level.
- Approval Time: The average time from an AI governance review request to an approval or rejection decision.
- Remediation Time: The time needed for resolving an identified governance, security, compliance, or model-risk issue.
- Incident Management: The time between detecting an AI incident and taking the defined containment or corrective action.
- Governance Cost Per AI System: The people, tooling, assessment, monitoring, and compliance costs associated with governing an AI system.
How to Implement an Enterprise AI Governance Framework in 90 Days?
Within the first 30 days of AI governance implementation, teams should be able to identify which AI systems are in use, who is accountable for them, and what level of risk the organization is willing to accept. Start by naming an executive sponsor who can take up ownership and policy decisions when there is disagreement between the teams and create an AI Governance Committee with representation of the said business teams. Next, build an AI inventory covering production systems, pilots, internal AI applications, third-party tools, embedded vendor AI features, GenAI applications, and AI agents. Use this inventory to create an initial risk taxonomy. And then, teams should be able to produce an AI acceptable-use policy and document the governance charter and risk appetite.
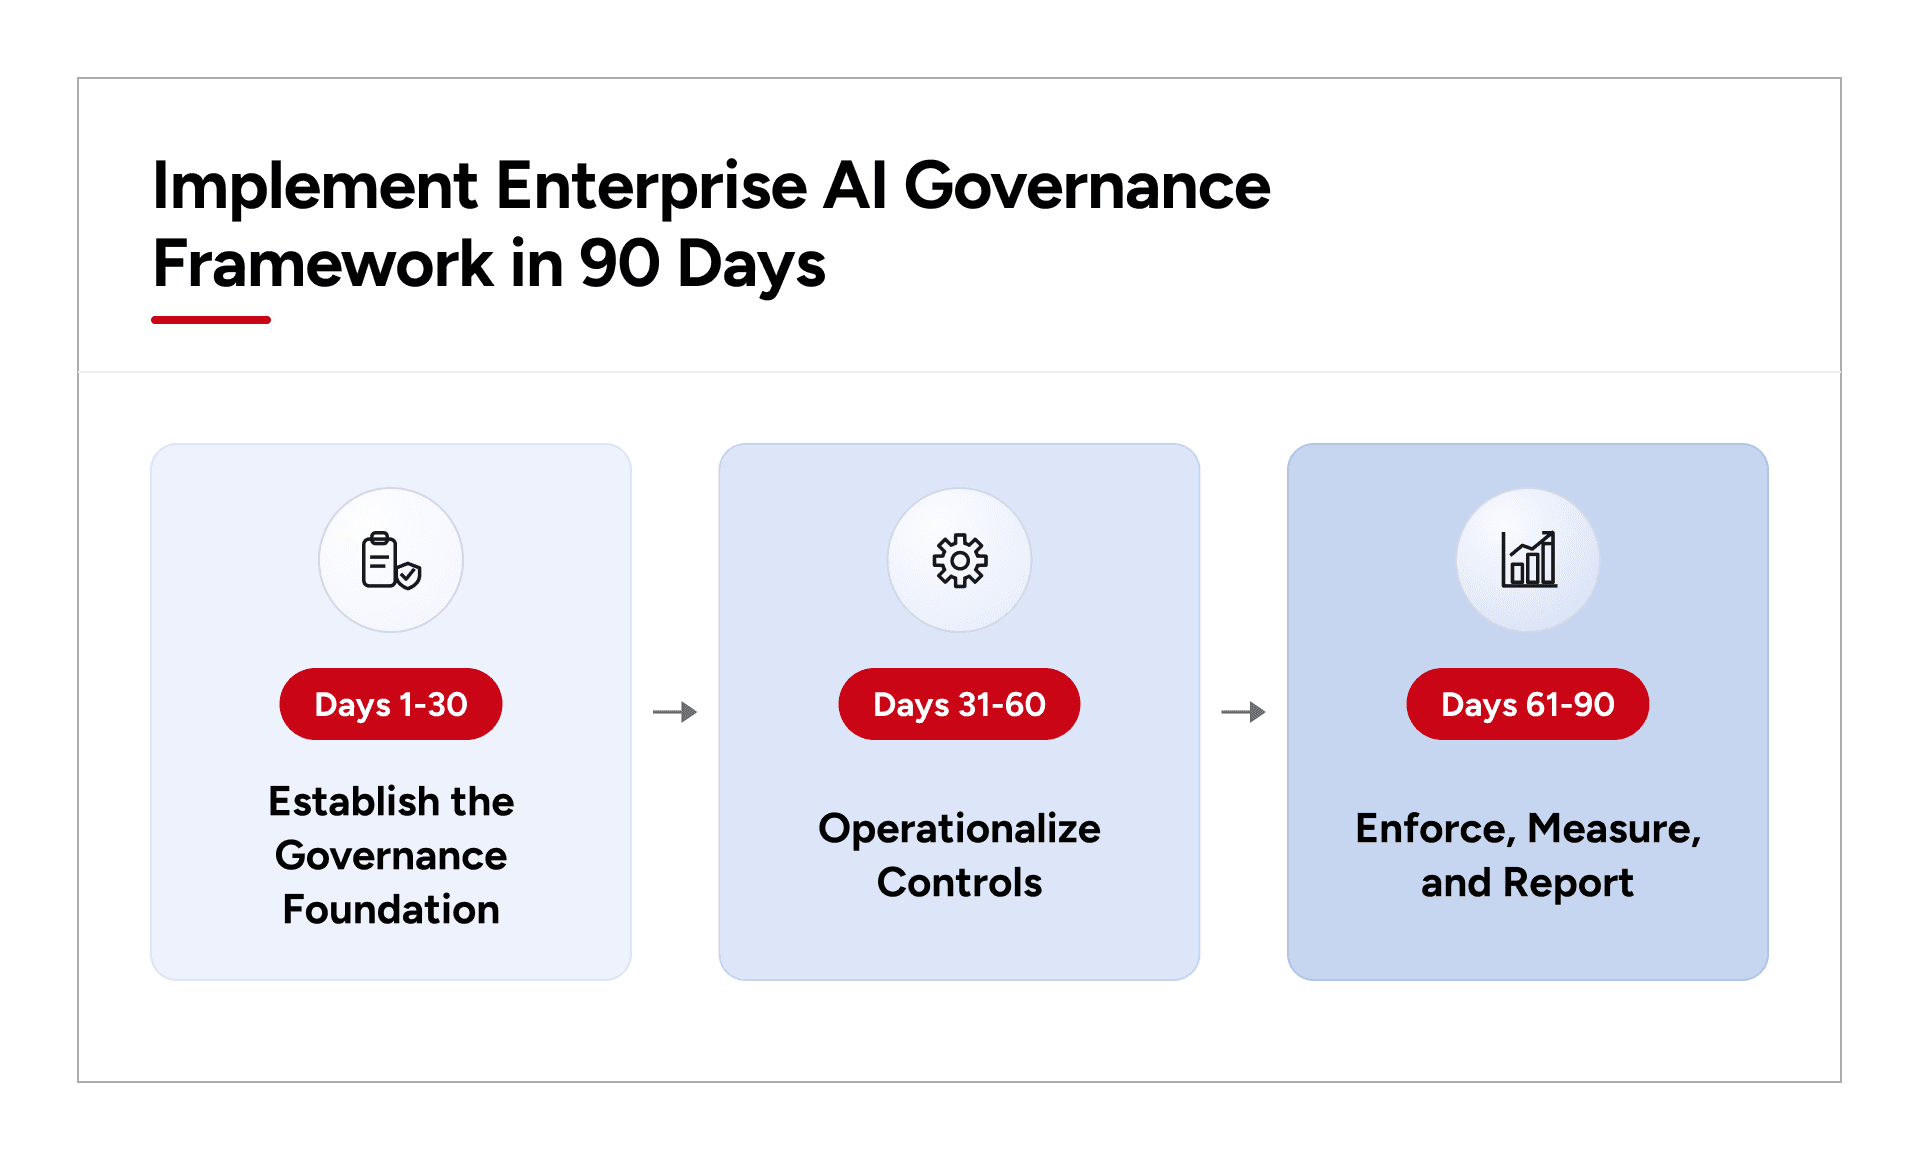
How Should Enterprises Operationalize AI Governance Controls in Days 31-60?
The second month turns governance rules into steps that teams must follow before an AI system reaches production. Apply the risk taxonomy to the systems identified during the first month and assign a business or system owner to each one and create a model and AI system model registry as the operational record.
Next, add engineering approval gates to existing development workflows that exist within the delivery process. Security and data controls need to follow the risk classification process and should include identity and access management, data minimization, encryption, input validation, output filtering, audit logging, privacy checks, and controls for sensitive information.
Establish a monitoring baseline for production systems to measure acceptable thresholds like who receives alerts and what happens when a threshold is breached. The AI governance committee should also agree on a small set of governance KPIs, such as inventory coverage, owner assignment, and high-risk systems.
What Should Enterprises Enforce, Measure, and Report in Days 61-90?
The final 30 days should test whether the governance process is operational when it is applied to live systems. Start with a high-risk model testing by reviewing the highest-risk systems against their required performance, the exact test should depend on the system and its intended use.
Run red-team exercises against selected high-risk GenAI applications and agents and look for failure modes related to prompt injection, inappropriate data disclosure, unsafe outputs, privilege escalation, or any other unauthorized action. After moving production systems for monitoring, the next step should be to track agreed upon measures like performance, drift, bias, hallucination rates, security events, and policy violations. In addition, teams should establish an AI incident-response process to specify how incidents are detected, assessed, and reviewed.
Once the organization’s first internal governance audit or mock audit is conducted before the end of the 90-day period, the results should be fed into the executive dashboard and board-level governance report. The final deliverable will include a year-one governance plan that covers the next round of policy updates, framework mapping, and expansion to new AI systems.
How does an Enterprise AI Governance Framework Control AI Agents?
AI agents require additional control systems as they use tools, access data, and take actions without a person approving every step. An agent that can update a customer record, issue a refund, or create a purchase order needs pre-defined limits before they can act.
- Permission Boundaries: Must specify the data, systems, and actions that an agent can access.
- Tool and API Access: Should be restricted to approved functions where each tool should have a defined purpose, required permissions, and input limits.
- Human Approval Thresholds: Should be able to initiate actions in case there are any financial, legal, employment, or customer impacts.
- Agent Memory: Should have rules regarding data storage, availability, and its accessibility. Customer information should not become a persistent agent memory simply because the agent encountered it during a conversation.
- Runtime Policy Enforcement and Prompt-injection Protection: Should check instructions and actions while the agent is live.
- Action Monitoring: Should record important agent activity, including toll calls, data access, approvals, rejected actions, and failures. This provides security and governance teams and an audit trail showing the attempts taken by an agent to initiate an action.
- Kill and Rollback Mechanisms: Should provide a way to stop an agent and recover from an incorrect action.
How Can Enterprises Comply with the NIST AI RMF, ISO/IEC 42001, and the EU AI Act?
NIST AI RMF, ISO/IEC 42001, and the EU AI Act are some of the crucial enterprise AI governance frameworks in 2026 that businesses today need to comply with. Since all three frameworks serve different purposes, the better approach here would be to an internal AI governance framework. After this, teams can map its policies, controls, evidence, and processes as per the requirements of each of the frameworks.
Framework | Primary Purpose | Best Fit |
AI risk management across the AI lifecycle | US enterprises and organizations seeking a practical risk-management structure | |
AI management system for establishing and improving AI governance | Global enterprises that need a structured management system | |
Legal requirements based on the risk and use of AI systems | Enterprises that develop, deploy, or provide AI systems within the EU market |
How Should Enterprises Map One AI Governance Framework Across These Standards?
Enterprises may maintain one AI inventory containing each system’s owner, purpose, data sources, risk classification, testing evidence, approvals, and monitoring records. The same evidence supports NIST risk management activities, ISO/IEC 42001 management-system requirements, and applicable EU AI Act obligations. The same approach can be applied across other governance areas:
Internal governance control | NIST AI RMF | ISO/IEC 42001 | EU AI Act |
AI policies and accountability | Govern | AI policies, roles, and responsibilities | Governance and organizational obligations |
AI risk classification | Map, Measure, Manage | AI risk assessment and treatment | Risk-based regulatory requirements |
Data and data-quality controls | Map, Manage | Data and resource controls | Data governance requirements for applicable systems |
Human oversight | Govern, Manage | Operational controls | Human oversight requirements for applicable high-risk systems |
Testing and evaluation | Measure | Performance and risk controls | Conformity and technical requirements where applicable |
Monitoring and incident management | Manage | Monitoring and continual improvement | Post-market monitoring and incident obligations where applicable |
Documentation and audit evidence | Govern, Measure | Documented information and management-system evidence | Technical documentation and record-keeping requirements where applicable |
The exact mapping depends on the organization’s role, industry, AI use cases, and regulatory exposure.
Why Choose GeekyAnts for Enterprise AI Governance and AI-Powered Product Engineering?
Enterprise AI governance works best when the people set up controls to understand how the AI system will actually be built, integrated, deployed, and maintained. Let’s say that even if a policy needs human review, such a requirement will still become an approval step, an access rule, a runtime check, or an escalation path within the product.
GeekyAnts brings 20 years of engineering experience since 2006 and 550+ engagements across products and enterprises. We focus on connecting enterprise AI governance solutions with the engineering work behind building AI-powered products by defining the use case and architecture through development, testing, deployment, and ongoing changes.
Enterprises need the right controls to show up where AI is designed, tested, deployed, and changed. When product, engineering, security, and governance teams work from the same requirements, it becomes easier to trace and address issues before they become business problems.
 Kunal KumarChief Revenue Officer
What Makes GeekyAnts Approach Different?
GeekyAnts brings AI-powered product engineering into the governance conversation. Product consultants and business analysts can help clarify the use case, while architects, designers, engineers, QA, DevOps, security, and AI specialists can translate those requirements into a working system.
Establishing AI Governance Across Compliance-Critical Systems
1. ShiftPilot - Workforce Governance
Our work with ShiftPilot showcases how governance requirements can become part of the product day-to-day workflow. The platform supports Belgian employment rules and DIMONA statutory reporting through automated declarations, employment-rule validation, filing-status tracking, and idempotent retry and recovery controls, pull-request reviews, CI gates, and staging validation, which adds further checks around payroll and compliance-sensitive changes.
2. RBI Domain Migration - Governance Under Regulatory Constraints
For India’s largest private bank, the domain migration had to meet an RBI mandate while protecting data sovereignty, security, and business continuity. The team audited 100+ partner integrations, updated SSL certificates, WAF rules, firewalls, and ingress controls, and used controlled deployment windows with monitoring and rollback readiness. Compliance validation was performed across connected ecosystems.
What is Next for Enterprise AI Governance?
The next phase of enterprise AI will bring more AI agents, even more use of third-party models, and AI systems that will have a great amount of access to business data. This phase will push the need for governance frameworks more closer in day-to-day product and engineering decisions.
Enterprises can expect the focus to move toward governing autonomous actions, AI supply chains, jurisdictions, and change in AI system’s operations along with the increase in their AI footprint.