

Security and Compliance Assessment Services
We examine your infrastructure security posture, access control architecture, and compliance alignment so you gain complete clarity on where vulnerabilities are hiding and what regulatory gaps are exposing your organization to risk. You get the most direct path to building security foundations that protect your systems, your data, and your customers.
Stop Assuming Your Systems Are Secure. Start Knowing They Are.








Our security and compliance assessment examines infrastructure configuration, identity and access management, application security, data protection, security tooling, and compliance controls. We review the actual environment to identify verified vulnerabilities, access risks, and gaps between current controls and applicable requirements.
Your security practices become deliberate and documented, audit cycles stop generating emergency remediation work, and the systems you operate genuinely reflect the data protection commitments your business has made to its customers. You leave holding a detailed, prioritized remediation roadmap your team can begin executing without delay.
Client Results and Success
Production-Ready Kubernetes Architecture
The platform was designed to support scalable production deployments with minimal resource consumption, enabling faster environment provisioning and operational stability.
- environments K8s setup
- 3
- environments K8s setup
- 95%
- savings over managed Kubernetes alternatives
- 35%
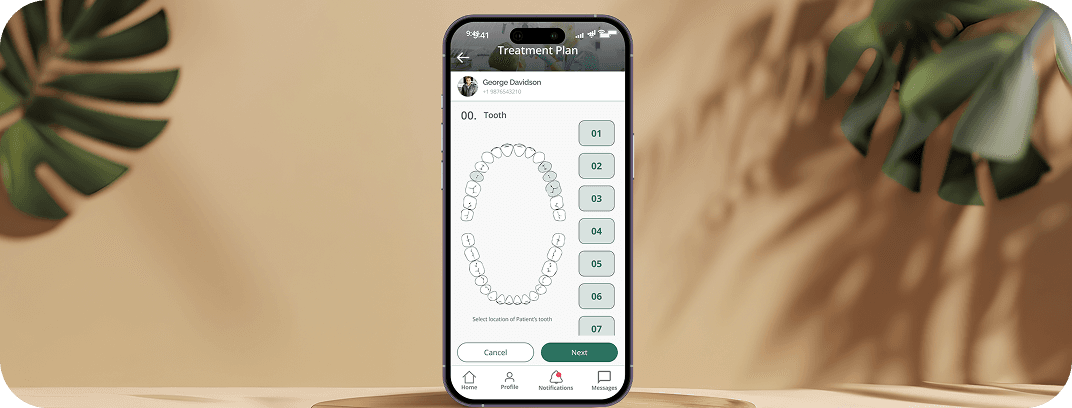
40% Faster Onboarding Completion
The redesigned system achieved a 40% reduction in onboarding completion time, directly improving platform adoption and reducing operational bottlenecks.
- Improvement in the doctor's efficiency for treatment planning
- 35%
- Reduction in onboarding completion time
- 40%
Production-Grade AI Infrastructure
The system supports scalable AI inference and automated inspection workflows, reducing manual intervention and enabling consistent performance under growing usage.
Read case study3× Faster Feature Iteration
The platform achieved 3x faster AI feature iteration cycles, significantly reducing time-to-release for new recommendation
- Reduction in meal decision time
- 40%
- Increase in daily active usage during pilot
- 2x
50% Fewer Manual Validation Cycles
The system achieved a 50% reduction in manual validation cycles, improving throughput and accelerating delivery timelines.
- Reduction in manual validation cycles
- 50%
- Faster internal testing workflows
- 30%
60% Cloud Cost Reduction
The platform achieved a 60% reduction in monthly cloud costs while maintaining uptime and transaction stability during and after optimization.
- Saved per month
- $4,800
- Annual savings
- $57,000+
What Our Cloud Security Compliance Audit Covers
Every engagement begins with a methodical, evidence-based evaluation spanning three essential pillars of your security and compliance posture: your infrastructure security controls, your application and data protection practices, and your organizational compliance alignment against the regulatory and contractual frameworks applicable to your business.
Our engineers work directly inside your environments, examining your actual IAM configurations, real network policies, genuine secrets management practices, and existing security tooling coverage, rather than relying on scanner outputs and questionnaire responses alone. The outcome is an honest characterization of where your security posture is genuinely robust, where it is relying on assumptions that have never been validated, and where a single misconfiguration or overlooked access path could result in a breach, a compliance failure, or both simultaneously.
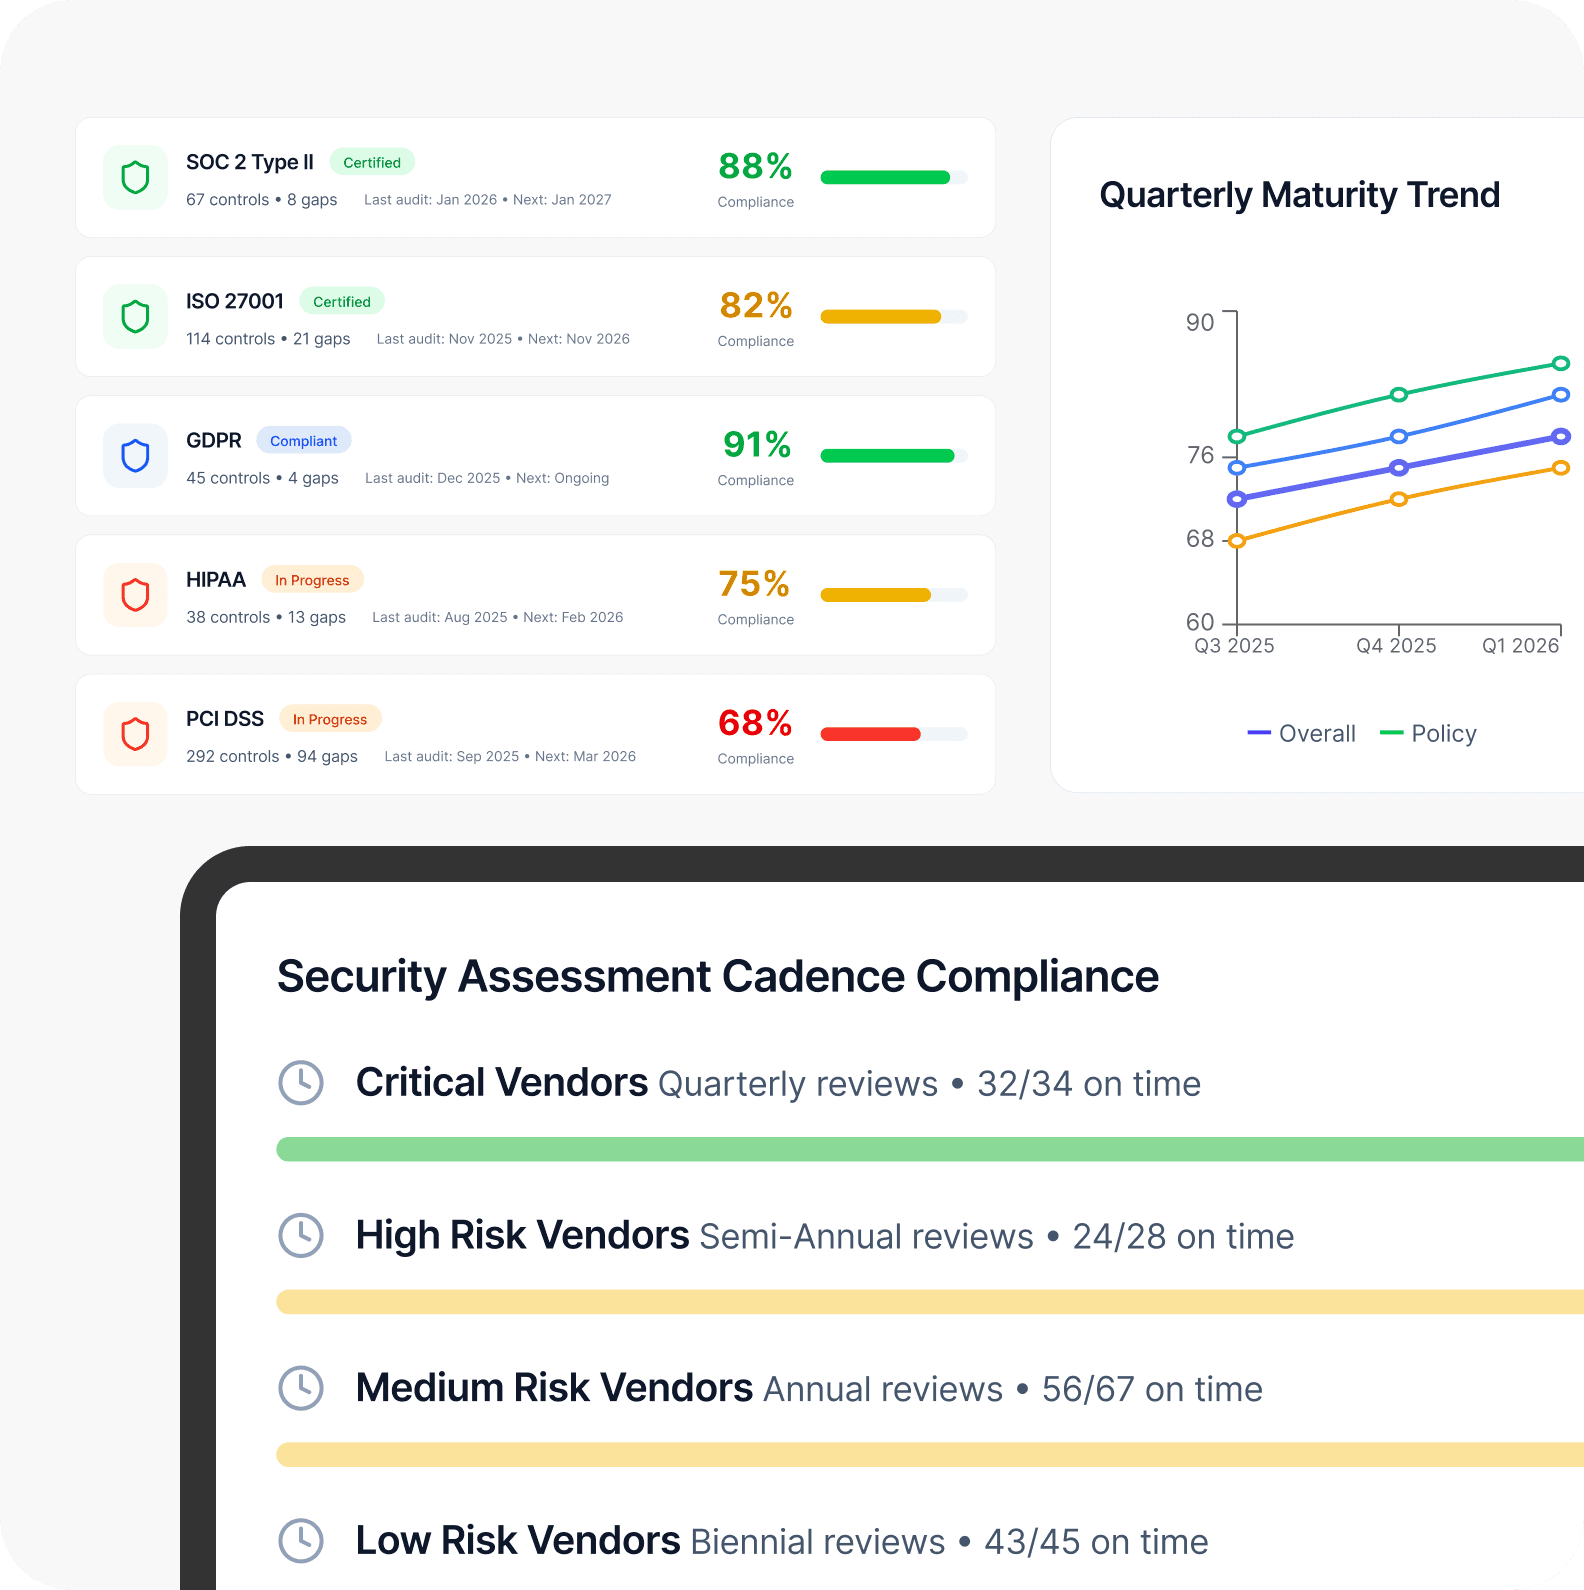
For enterprise SaaS environments, we evaluate these controls against the platform's architecture, customer data, cloud configuration, access model, third-party dependencies, and applicable frameworks such as SOC 2, ISO 27001, GDPR, HIPAA, or PCI DSS.
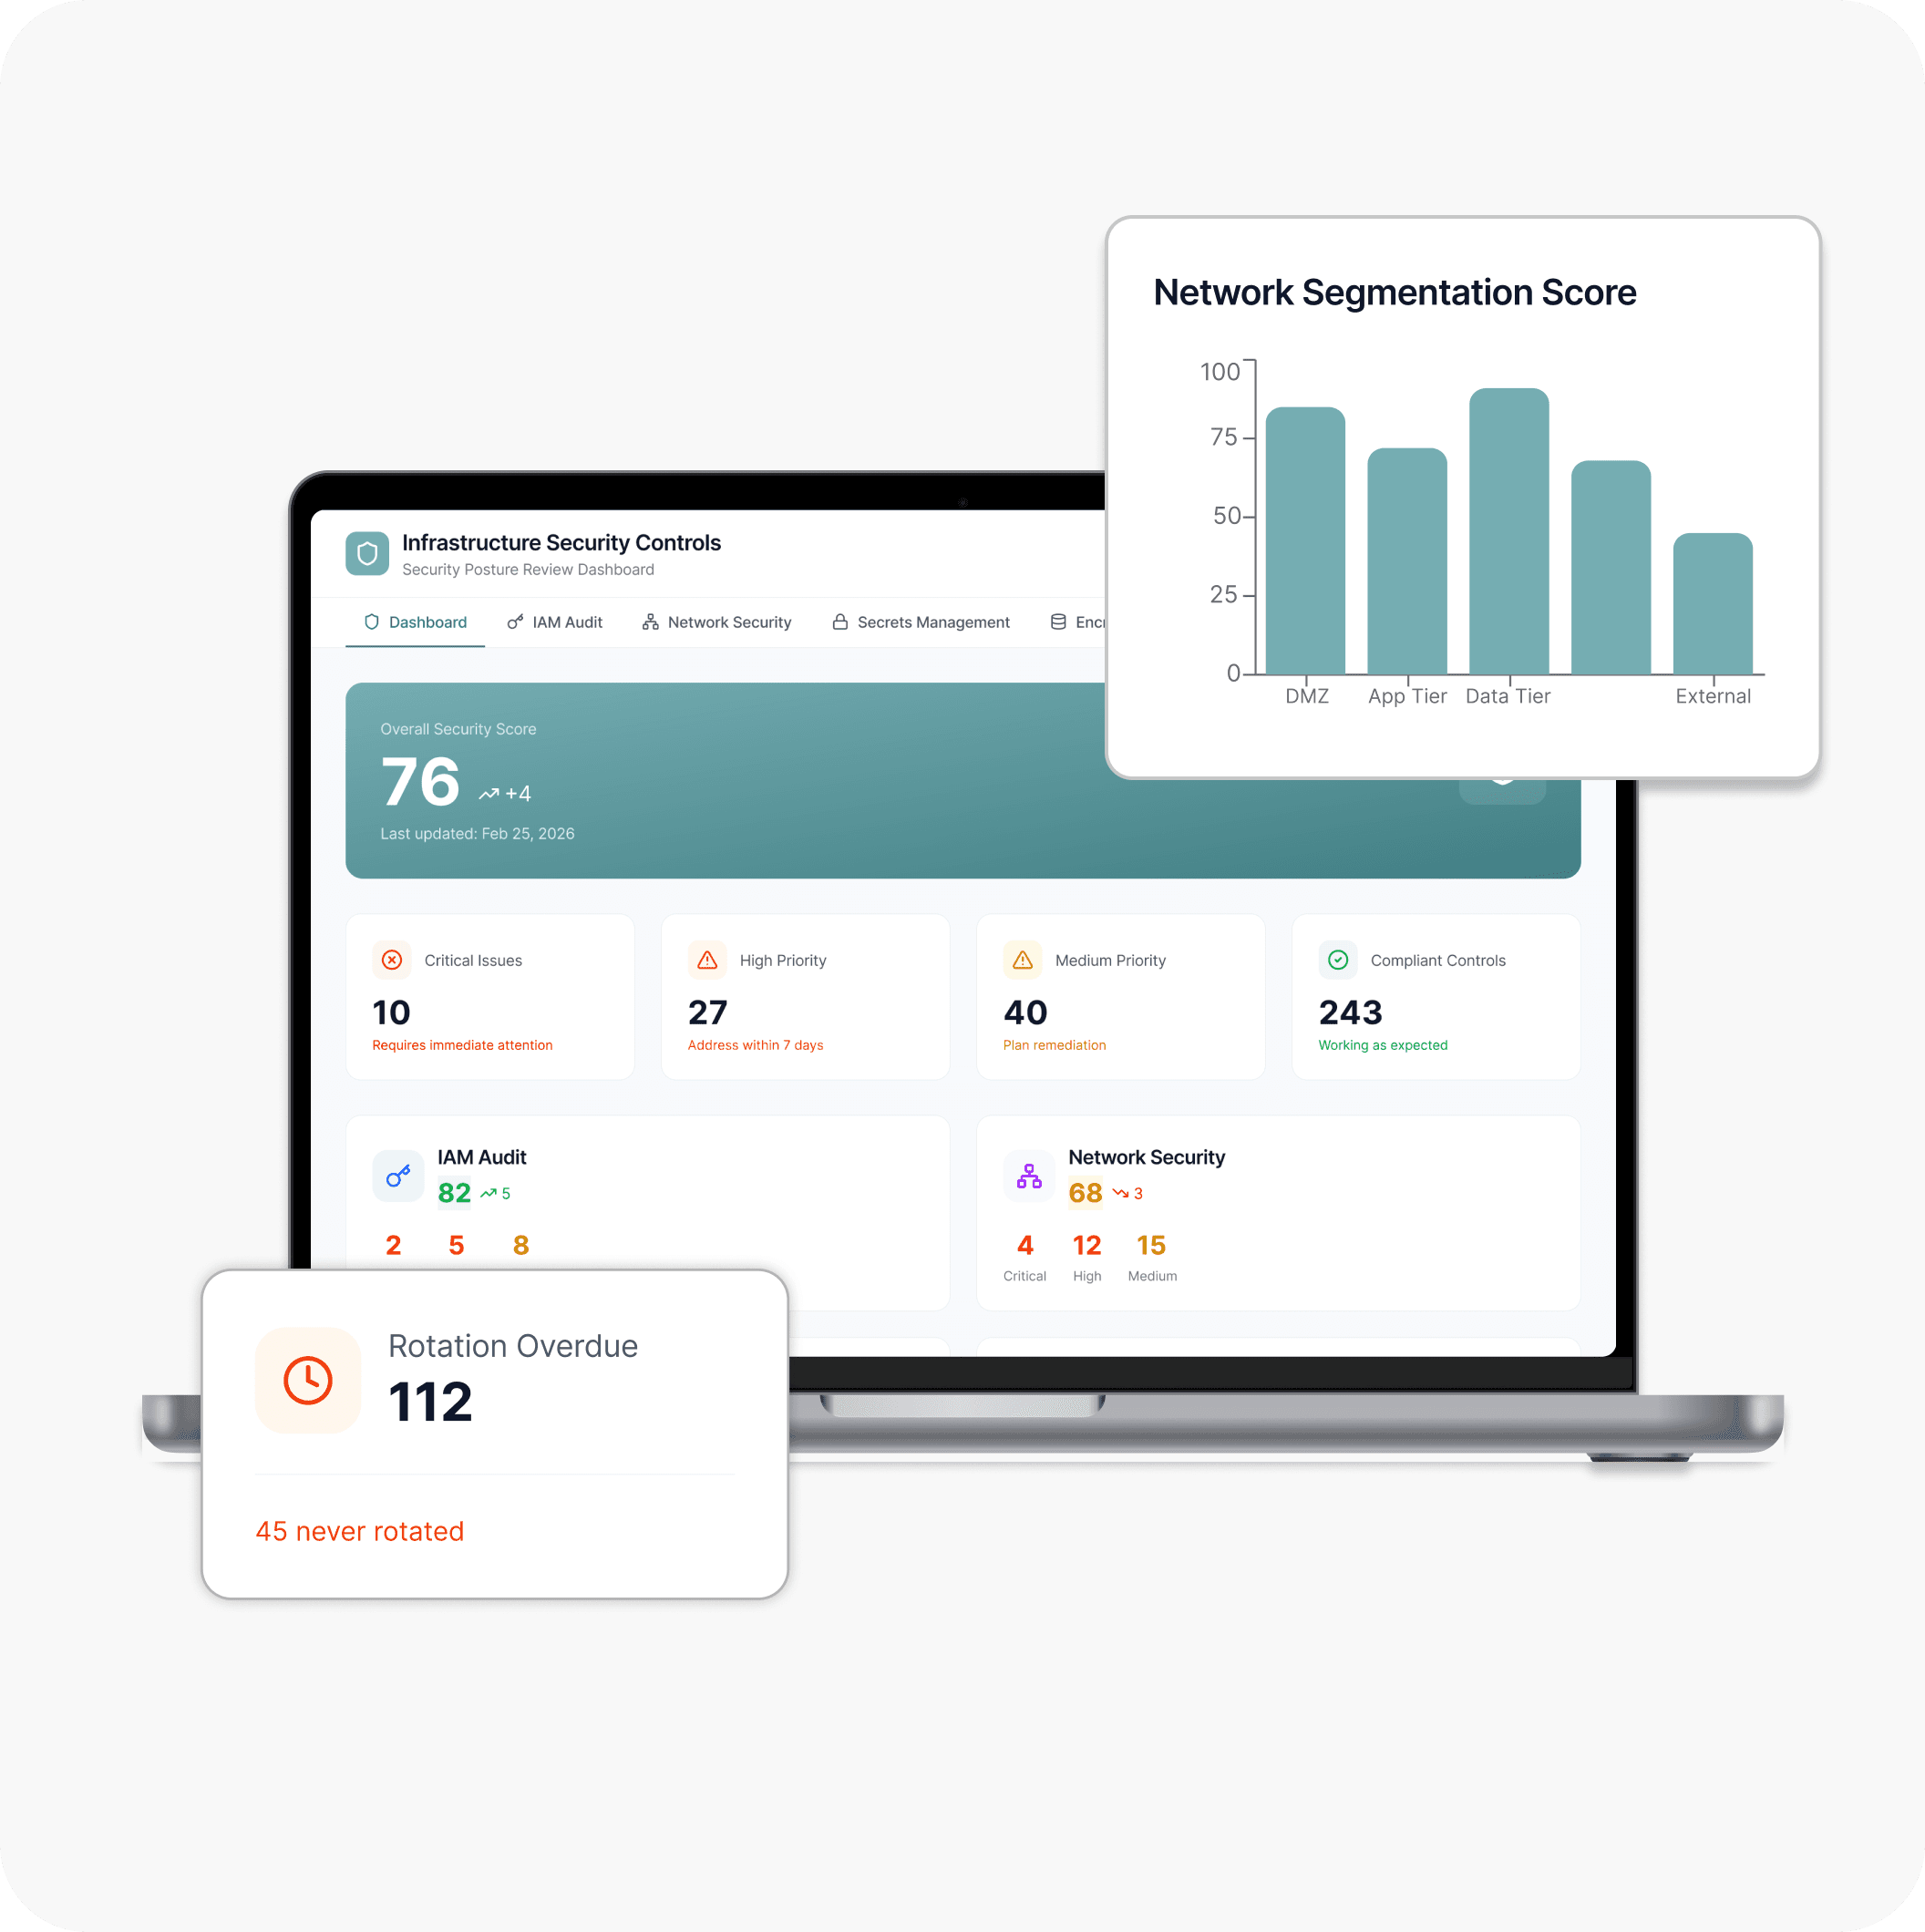
- Identity and access management audit: IAM role assignments, privilege escalation paths, service account permissions, and cross-account access configurations
- Network security assessment: Security group rules, firewall policies, publicly exposed endpoints, and internal network segmentation adequacy
- Secrets and credential management: Hardcoded credentials identification, secrets rotation policies, vault configuration, and environment variable exposure risks
- Encryption coverage review: Data at rest encryption configuration, transport layer security implementation, and key management practices
- Authentication and authorization review: Session management, token handling, API authentication mechanisms, and broken access control identification
- Dependency and supply chain security: Third-party library vulnerability exposure, container image scanning coverage, and software bill of materials visibility
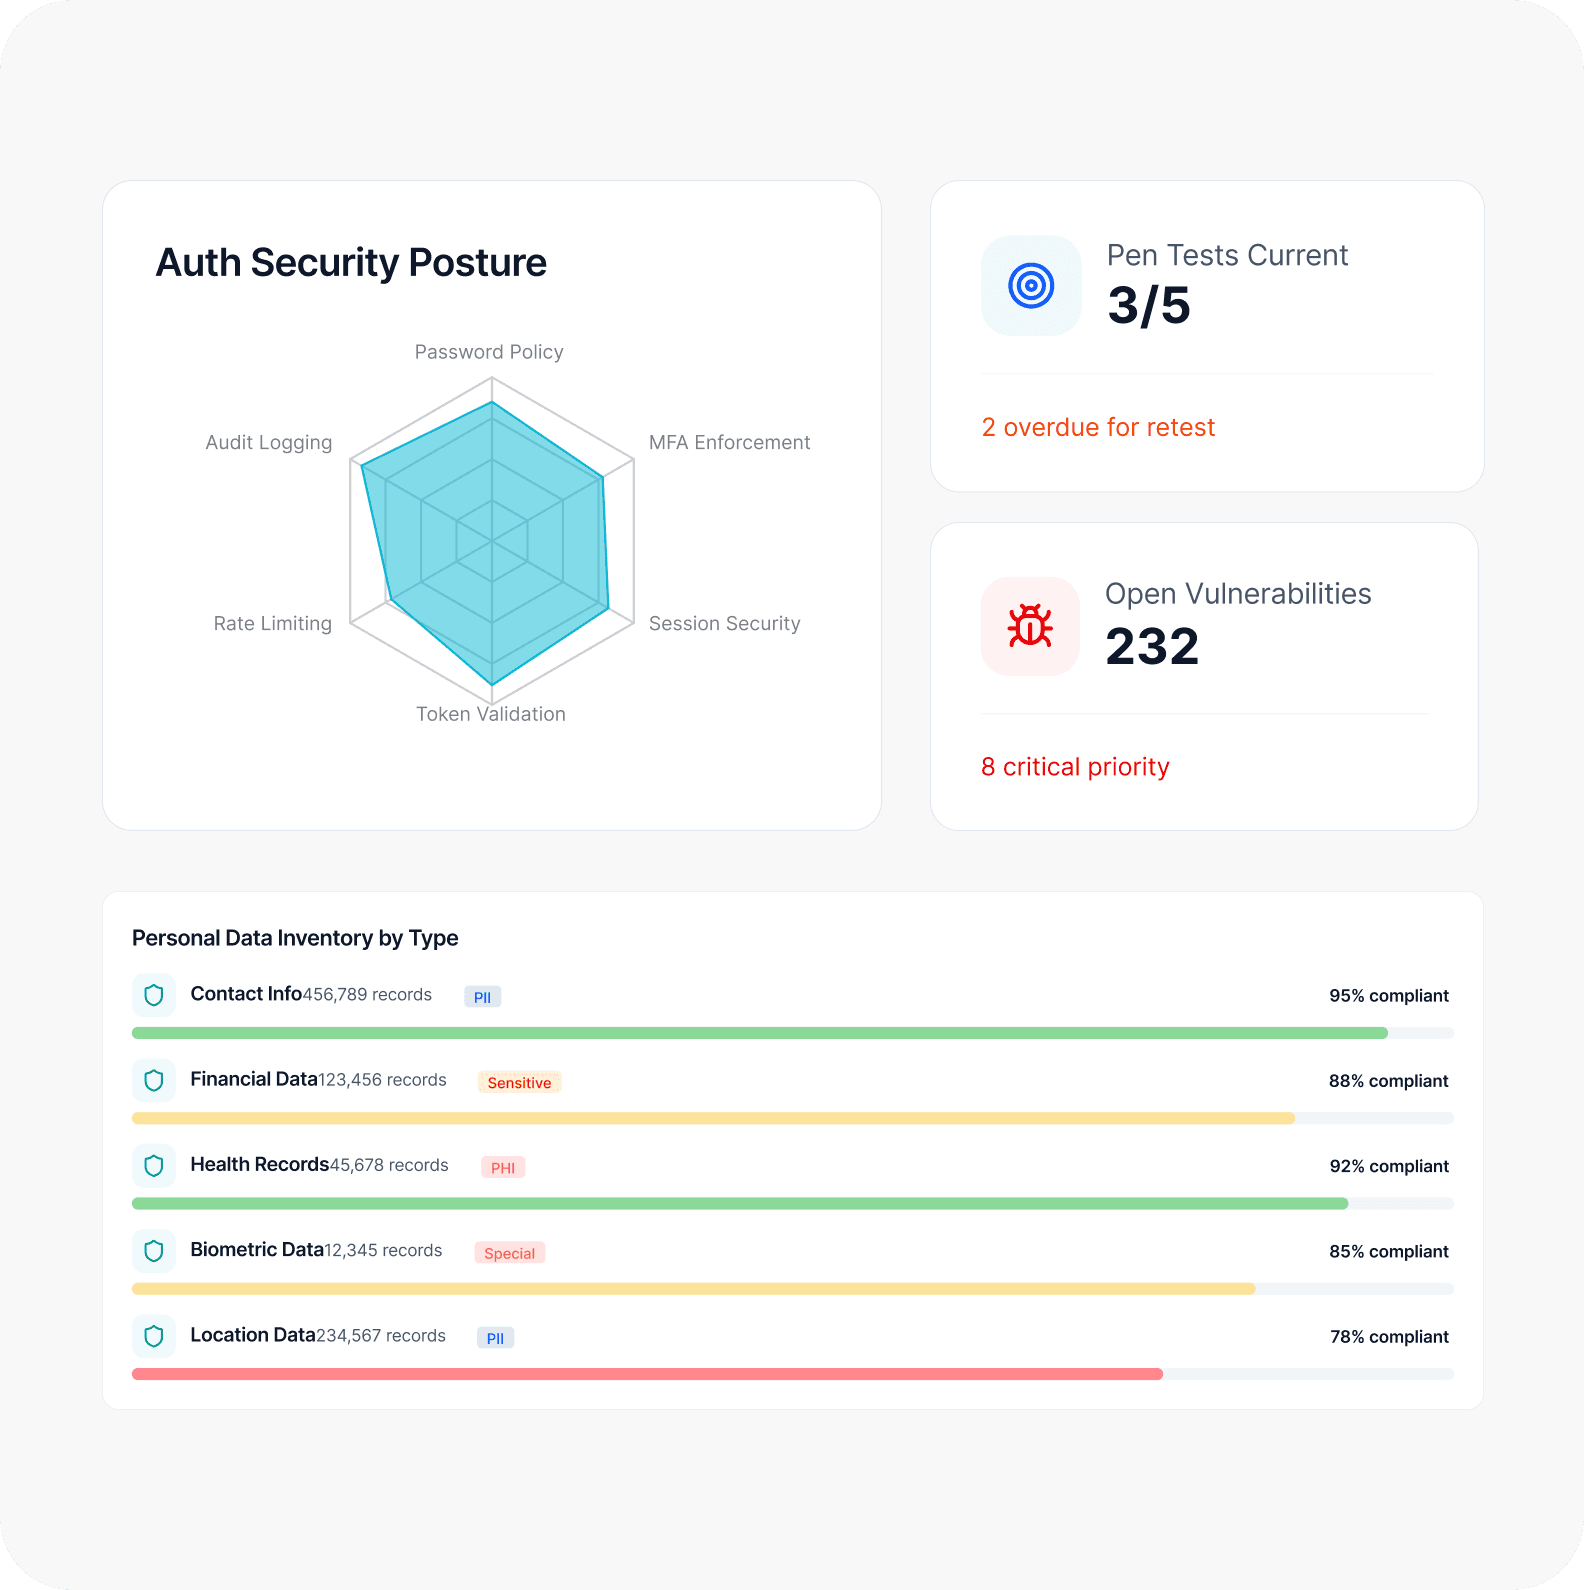
- Data classification and handling audit: Personal data inventory, retention policy enforcement, cross-border transfer controls, and data minimization practices
- Security testing integration: SAST and DAST tooling coverage, penetration testing currency, and vulnerability remediation tracking effectiveness
- Regulatory framework mapping: Gap analysis against applicable standards, including SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS based on your business context
- Control documentation assessment: Policy completeness, evidence collection maturity, and audit readiness against your target compliance frameworks
- Vendor and third-party risk: Supplier security assessment practices, data processing agreement coverage, and fourth-party risk visibility
- Security governance maturity: Ownership accountability, security review processes embedded in delivery workflows, and board-level risk reporting adequacy
Security Outcomes We Are Accountable For Delivering
Our assessment documents identified vulnerabilities, misconfigurations, access-control weaknesses, and compliance gaps across the agreed scope. Findings are organized by severity, exploitability, business impact, and remediation complexity so engineering and security teams can prioritize improvements and prepare for customer or regulatory security reviews.
Know Your Actual Security Posture, Not Your Assumed One
Understand every misconfiguration, every access control weakness, and every compliance gap in your current environment — so your security programme is built on verified evidence rather than inherited assumptions about what previous teams put in place.
Win Enterprise Customers Without Security Reviews Derailing Deals
Establish the security controls and compliance documentation your largest prospective customers require so security questionnaires and vendor assessments accelerate commercial conversations rather than stalling them.
Protect Customer Data With Controls That Were Designed, Not Accumulated
Replace the patchwork of security measures added reactively over time with a coherent, layered protection architecture deliberately designed around the sensitivity of the data your platform handles.
Meet Regulatory Requirements Before They Become Enforcement Actions
Align your security controls and compliance documentation to the regulatory frameworks governing your industry and geographies now — while remediation is a planned programme rather than a crisis response.
Industries Across Which We Deliver Security and Compliance Impact
We develop security strategies calibrated to the threat landscapes, regulatory obligations, and data sensitivity profiles that vary significantly across every industry we operate within. Our approach consistently prioritises building security controls that are sustainable under the pressure of ongoing delivery rather than point-in-time hardening that erodes as systems evolve.We understand the compliance frameworks governing healthcare data, financial transactions, consumer privacy, and critical infrastructure — and the commercial consequences of failing to meet them. Every industry in our portfolio reflects genuine, hands-on security engineering experience.
Why Choose GeekyAnts for Security and Compliance Assessment?
GeekyAnts evaluates security within the broader production environment. Our DevOps engineers review cloud infrastructure, application controls, identity and access, CI/CD practices, observability, reliability, data protection, and compliance requirements as connected parts of the same system.
The assessment can stand alone or inform broader DevOps improvements when findings require infrastructure, delivery, reliability, or operational changes.
Our AI-enabled engineers and security specialists have led security transformation programmes across platforms, handling sensitive financial, healthcare, and consumer data at a significant scale.
Every vulnerability and compliance gap is characterised by its exploitability, its potential business impact, and its remediation complexity — giving your leadership team the context needed to make informed prioritization decisions rather than treating every finding as equally urgent.
We recommend the security controls and compliance investments that your specific threat model, regulatory obligations, and business context demand — never a generic hardening checklist applied without regard for your operational reality.
Every recommendation we produce is specific, testable, and directly assignable — scoped to the actual configurations, policies, and tooling present in your environment rather than described in abstract architectural terms.
We document every finding, every control recommendation, and every compliance mapping rationale so your team owns the security programme fully and can sustain it independently long after the engagement concludes.
Our Offerings in DevOps Consulting and Services
Our Latest Thinking
FAQs About Security & Compliance Basics Assessment Services
An enterprise SaaS security assessment can cover cloud infrastructure, IAM, network controls, authentication and authorization, secrets management, encryption, application dependencies, data handling, security testing, logging, vendor risk, and compliance controls. GeekyAnts defines the final scope around the platform’s architecture, customer data, cloud environment, threat exposure, and applicable regulatory or contractual requirements.
Most assessments conclude within 2 to 4 weeks, depending on the breadth of your infrastructure estate, the number of applications and services in scope, and the complexity of your regulatory obligations. Organizations operating across multiple cloud accounts, handling sensitive regulated data categories, or pursuing multiple compliance certifications simultaneously may require additional time to ensure complete coverage across all relevant security domains.
We define the engagement scope and timeline during the initial discovery session so your team understands exactly what the process involves before work begins.
We operate within the access boundaries your security, legal, and compliance teams define. Read-only access to your cloud console configurations, IAM policies, network security rules, secrets management systems, and existing security tooling is generally sufficient to conduct a thorough assessment.
We never require access to actual customer data records — our evaluation focuses on the controls governing how data is protected rather than the data itself. For organizations in regulated sectors with strict access governance requirements, we are experienced in conducting comprehensive assessments within tightly controlled access frameworks without compromising the depth or quality of findings.
Security assessments are designed to operate alongside your normal delivery cadence without interrupting sprint commitments or release schedules. We typically conduct 3 to 4 structured working sessions with relevant engineers, platform leads, and compliance representatives across the engagement period. Outside of those sessions, your teams continue their normal work. Most organizations we assess report contributing fewer than 5 hours of active participation across the full engagement. Where your team is operating under a particularly demanding delivery period, we schedule working sessions around your existing commitments to avoid introducing additional pressure at already constrained moments.
A cloud security compliance audit is useful before an enterprise security review, compliance initiative, major infrastructure change, regulated-market launch, or when access controls and security configurations have grown without systematic review. GeekyAnts evaluates the current environment and maps identified gaps against the security and compliance requirements applicable to the agreed scope.
Our compliance coverage spans the frameworks most commonly applicable to technology organizations across global markets. These include SOC 2 Type I and Type II, ISO 27001, GDPR and other regional data privacy regulations, HIPAA for healthcare data handlers, PCI DSS for payment card processing environments, and SOX controls relevant to engineering organizations within publicly traded or pre-IPO companies.
For organizations operating across multiple jurisdictions or pursuing multiple certifications simultaneously, we map your existing controls against all applicable frameworks in a single engagement, identifying shared controls that satisfy multiple requirements and prioritizing the gaps specific to each framework. We are transparent about the boundaries of our assessment where specialist legal or regulatory expertise is required alongside technical security evaluation.
You receive a comprehensive security findings report documenting every identified vulnerability, misconfiguration, and compliance gap across the assessment scope. This is accompanied by a risk register classifying each finding by severity, exploitability, and potential business impact. The remediation roadmap sequences interventions across 30, 60, and 90-day execution windows based on the combination of risk severity and implementation effort.
For organizations pursuing compliance certification, we provide a control gap analysis mapping your current posture against each applicable framework requirement and identifying the specific controls requiring implementation or strengthening. Every engagement concludes with a live readout session where our engineers walk your technical and leadership teams through every finding, its business context, and the recommended remediation approach.
We treat the security of the engagement with the same rigour we apply to the environments we assess. Every access credential provided for assessment purposes is handled through dedicated, time-limited accounts wherever your environment supports them, is stored exclusively within our secure credential management infrastructure, and is revoked immediately upon engagement completion.
Assessment findings are transmitted exclusively through encrypted channels and stored within access-controlled environments for the duration of the engagement. We operate under a formal non-disclosure agreement covering all information accessed during the assessment, and we document and return or destroy all artefacts gathered during the engagement in accordance with your data handling requirements.
Automated vulnerability scanning and a security assessment serve meaningfully different purposes and should not be treated as equivalent activities. Vulnerability scanning identifies known weaknesses in software versions, patch levels, and configuration baselines against published vulnerability databases. It is fast, scalable, and valuable — but it operates without contextual understanding of your architecture, your access control design, your data flows, or your compliance obligations.
A security assessment combines automated tooling with hands-on engineering analysis to evaluate not just what vulnerabilities exist but whether your security architecture would contain a breach, whether your access controls would prevent lateral movement, whether your compliance controls would satisfy an auditor, and whether your incident response procedures would enable effective recovery. The findings from a genuine security assessment consistently include material risks that automated scanners are architecturally incapable of detecting.
The assessment is designed as a standalone deliverable that fully equips your engineering team to execute remediation independently. Every finding includes specific, actionable remediation guidance describing exactly what needs to change, in which system or configuration, and why — without requiring our continued involvement to interpret or expand upon.
For organizations that prefer external support during remediation, we offer targeted security engineering engagement covering specific control implementation, secrets management migration, IAM restructuring, compliance evidence collection programme development, and security tooling integration. For organizations pursuing formal compliance certification following the assessment, we can also support the certification process itself, including evidence preparation, auditor engagement, and control testing. Whether you execute independently or engage us to support specific workstreams, the assessment documentation serves as the authoritative remediation reference throughout.
Third-party and supply chain security receives dedicated attention within every assessment we conduct, because it represents one of the fastest-growing categories of security risk for engineering organizations of every size. We examine your software dependency inventory for known vulnerability exposure, assess your container image provenance and scanning coverage, evaluate your vendor security assessment practices and the contractual security obligations embedded in your supplier agreements, and identify where third-party access to your systems or data creates risk that your internal controls cannot fully govern.
Where significant supply chain exposure is identified, we provide specific recommendations for dependency management tooling, vendor assessment frameworks, and contractual security requirements appropriate for your supplier relationships and data sharing arrangements.
The most effective internal argument for proactive security investment is a precise, credible quantification of the cost of the alternative — and our assessment is specifically designed to provide exactly that. Beyond the direct financial costs of breach response, regulatory penalties, and customer notification obligations, security incidents carry commercial consequences including enterprise customer churn, deal pipeline disruption during the period of heightened scrutiny, and the reputational damage that follows public disclosure.
For organizations pursuing SOC 2, ISO 27001, or other compliance certifications, an assessment conducted before the certification programme begins consistently reduces the total programme cost by identifying and addressing control gaps before an external auditor discovers them — when remediation is a planned activity rather than an urgent certification prerequisite. Most organisations we work with recover the full cost of the assessment within a single avoided audit finding or a single enterprise deal that does not stall on security review.
