

AWS Cloud Foundations
Overly permissive IAM roles and uncontrolled account sprawl silently erode cloud security until an exposure event forces action. We take ownership of your AWS account structure and foundational controls from the ground up, so the infrastructure your business runs on is never the gap your security team is chasing.
Move Beyond Ad-Hoc AWS to Governed Enterprise Cloud








AWS debt rarely surfaces until the damage is already compounding. It builds through permissive roles, accounts provisioned outside any formal process, and a network topology that expanded until no single person understood it. The reckoning usually arrives as a failed audit or a breach that properly structured foundations would have stopped. Our AWS Cloud Foundations service exists to close that gap. We begin by mapping where your account hierarchy and access controls are exposing workloads to risk, then replace them with structured, auditable foundations your teams can operate confidently within.
Client Results and Success
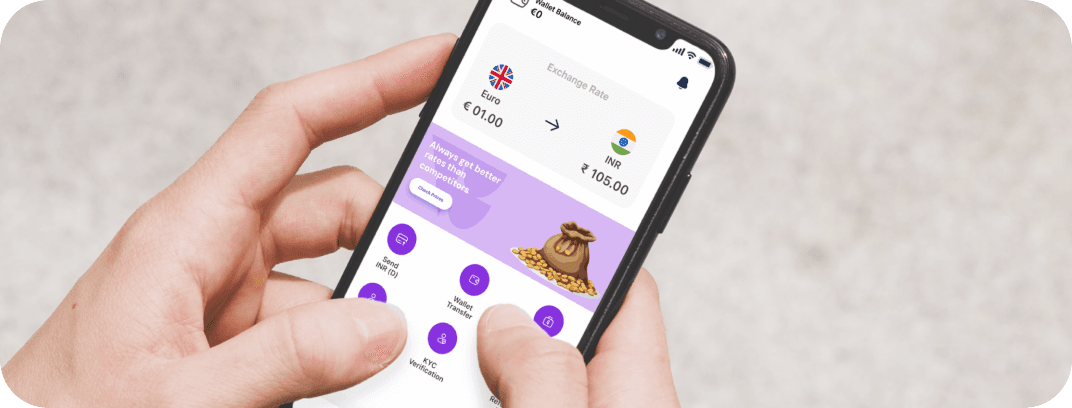
400M+ global payments processed annually
The system provides the scalability required to handle millions of transactions while maintaining data integrity and administrative control.
- Active Users in the UK, Canada, Europe, and Australia
- 120k+
- Global Payments Processed Annually
- 400M+
- Downloads Across iOS and Android
- 350k+
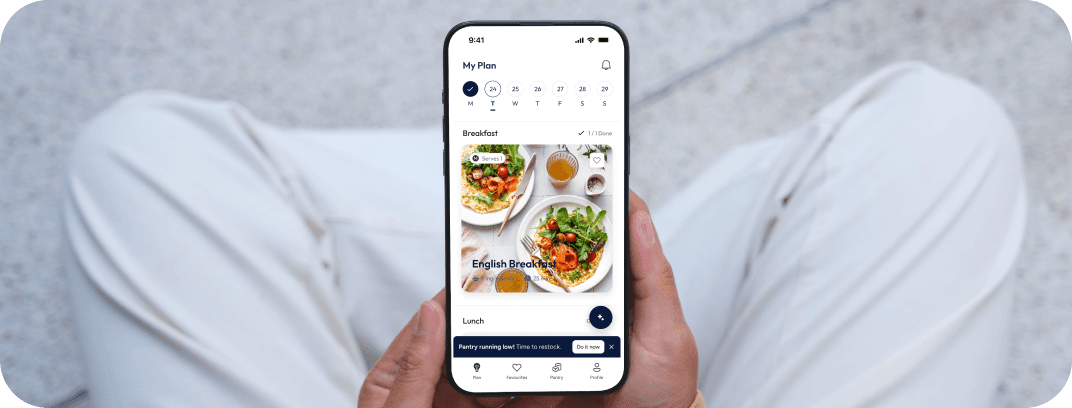
3x faster AI feature iteration
The modular backend architecture allowed the team to deploy new AI capabilities and personalized features significantly faster than industry benchmarks.
- Reduction in meal decision time
- 40%
- Increase in daily active usage during pilot
- 2x
- Faster iteration on new AI-driven features
- 3x
$57,000+ Annual Savings
The project achieved a 60% reduction in monthly cloud costs (from $8,100 to $3,300) without any loss in transaction speed or system security.
- Reduction in monthly cloud costs
- 60%
- Saved per month
- $4800
- Annual savings
- $57,000+
50% reduction in manual validation cycles
The integration of automated benchmarking frameworks and AI-driven process automation also resulted in 30% faster internal testing workflows.
- faster internal testing
- 30%
- reduction in manual validation
- 50%
AI-Powered Candidate Screening at Scale
Automated technical interviews with real-time voice interactions, adaptive questioning, and intelligent candidate evaluation to accelerate hiring and improve screening consistency.
- Candidate Screening
- 24/7
- Voice Interviews
- AI-Led
Transforming Pantry Data into Personalized Meal Experiences
Built an AI-powered platform that analyzes pantry inventory and user preferences to deliver personalized meal recommendations, reduce food waste, and simplify meal planning.
- Reduction in meal decision time
- 40%
- Higher Daily Usage
- 2x
- Faster Feature Delivery
- 3x
Our AWS Cloud Foundations Services
Infrastructure risk should not be something your team quietly absorbs. Our services close the gaps that come from ad-hoc account creation, permission creep, and setups that look stable until something breaks.
Full account structure design covering organizational units, SCPs, and access boundaries across your AWS environment.
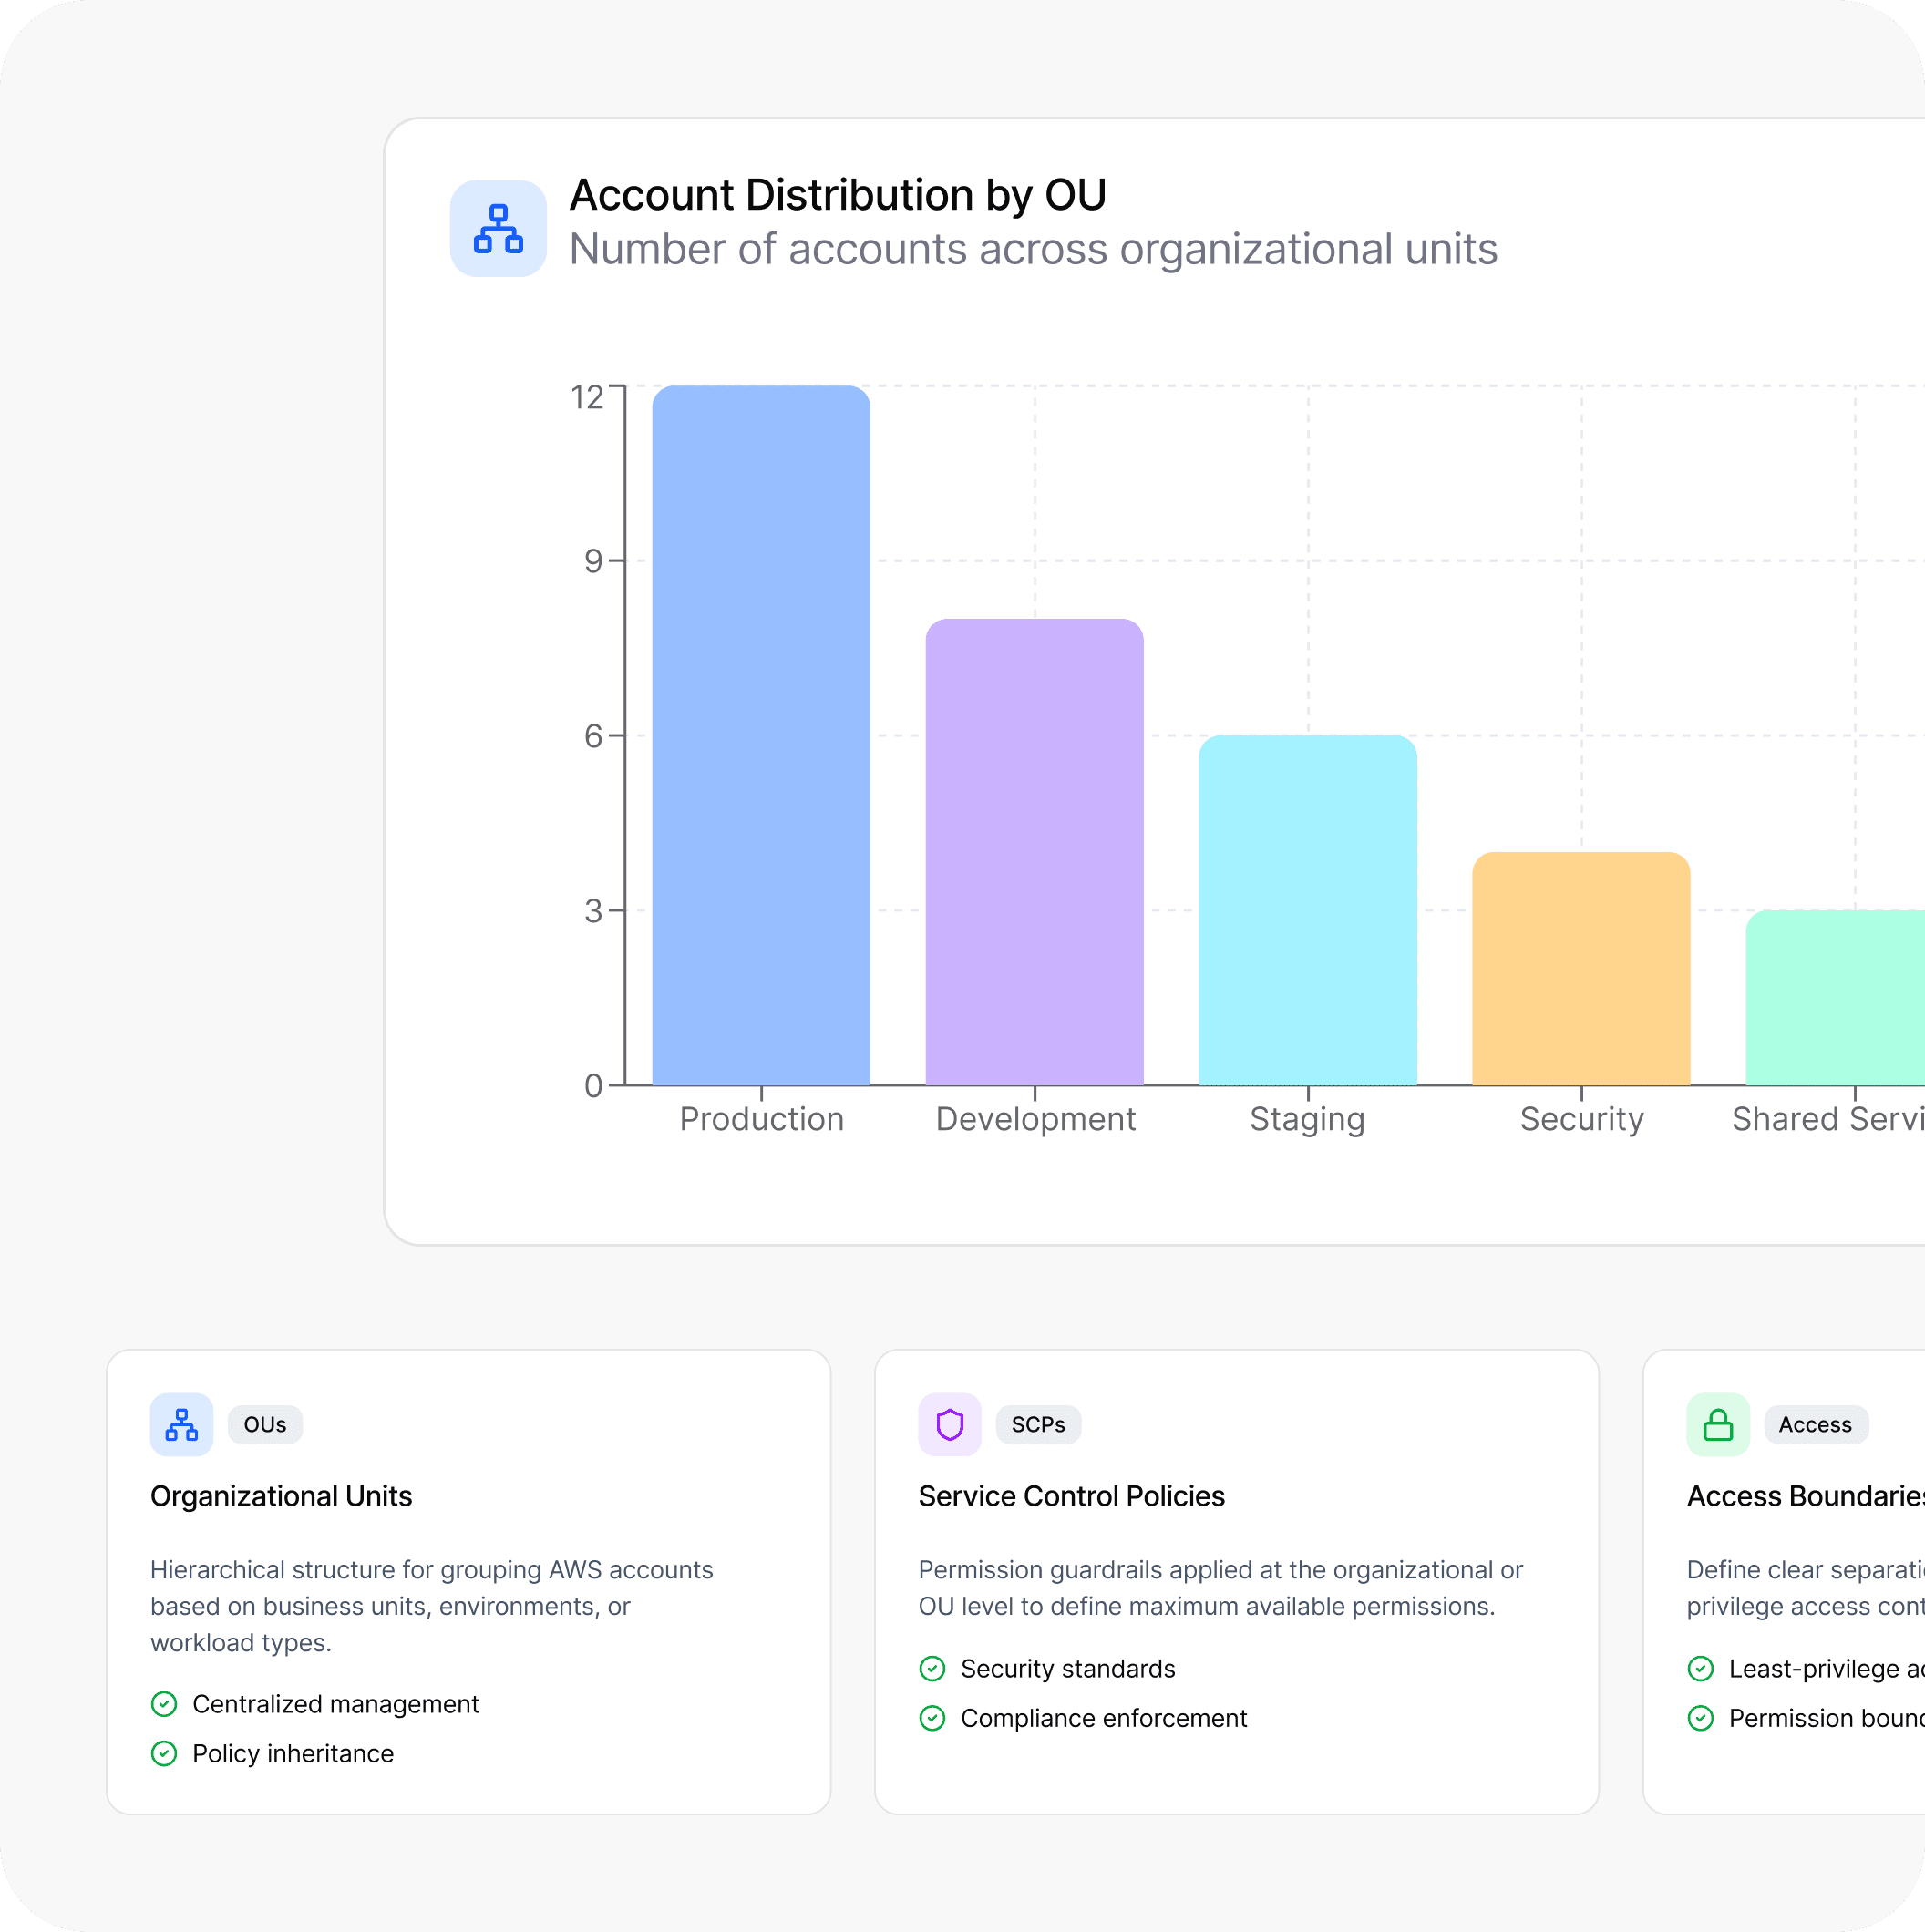
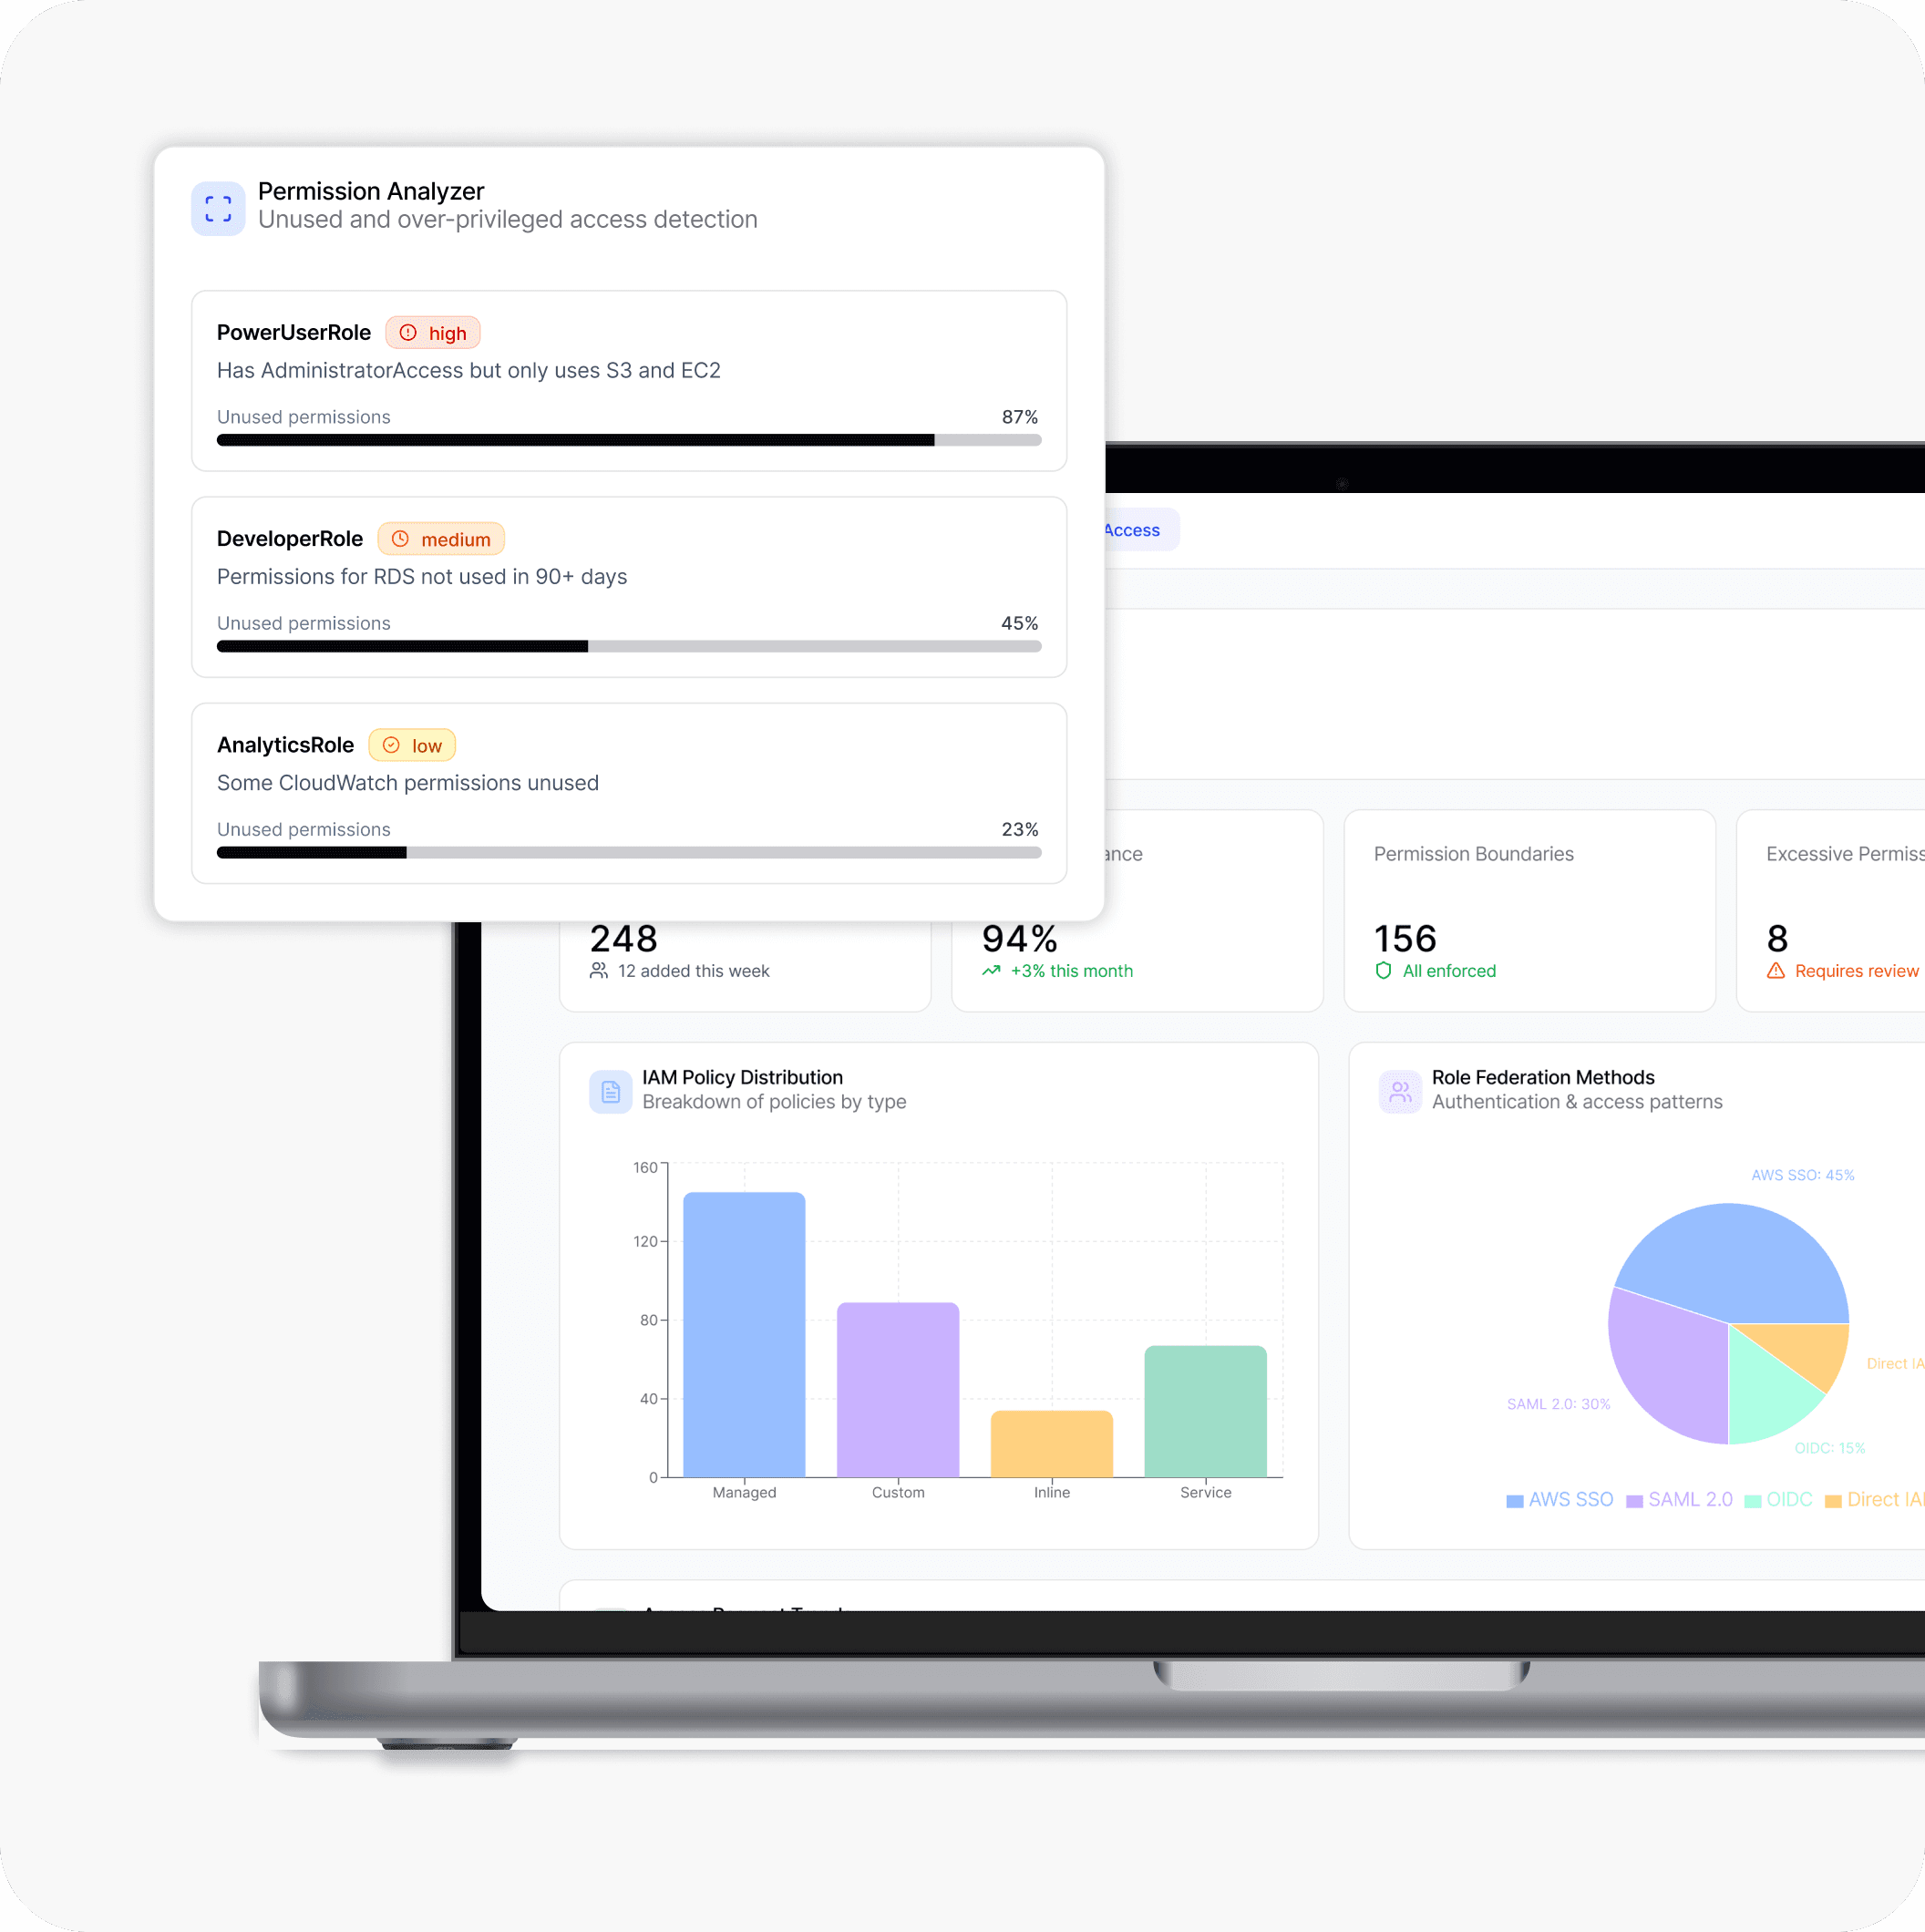
Framework built around least-privilege IAM policies, role federation, and permission boundaries suited to your actual workload.
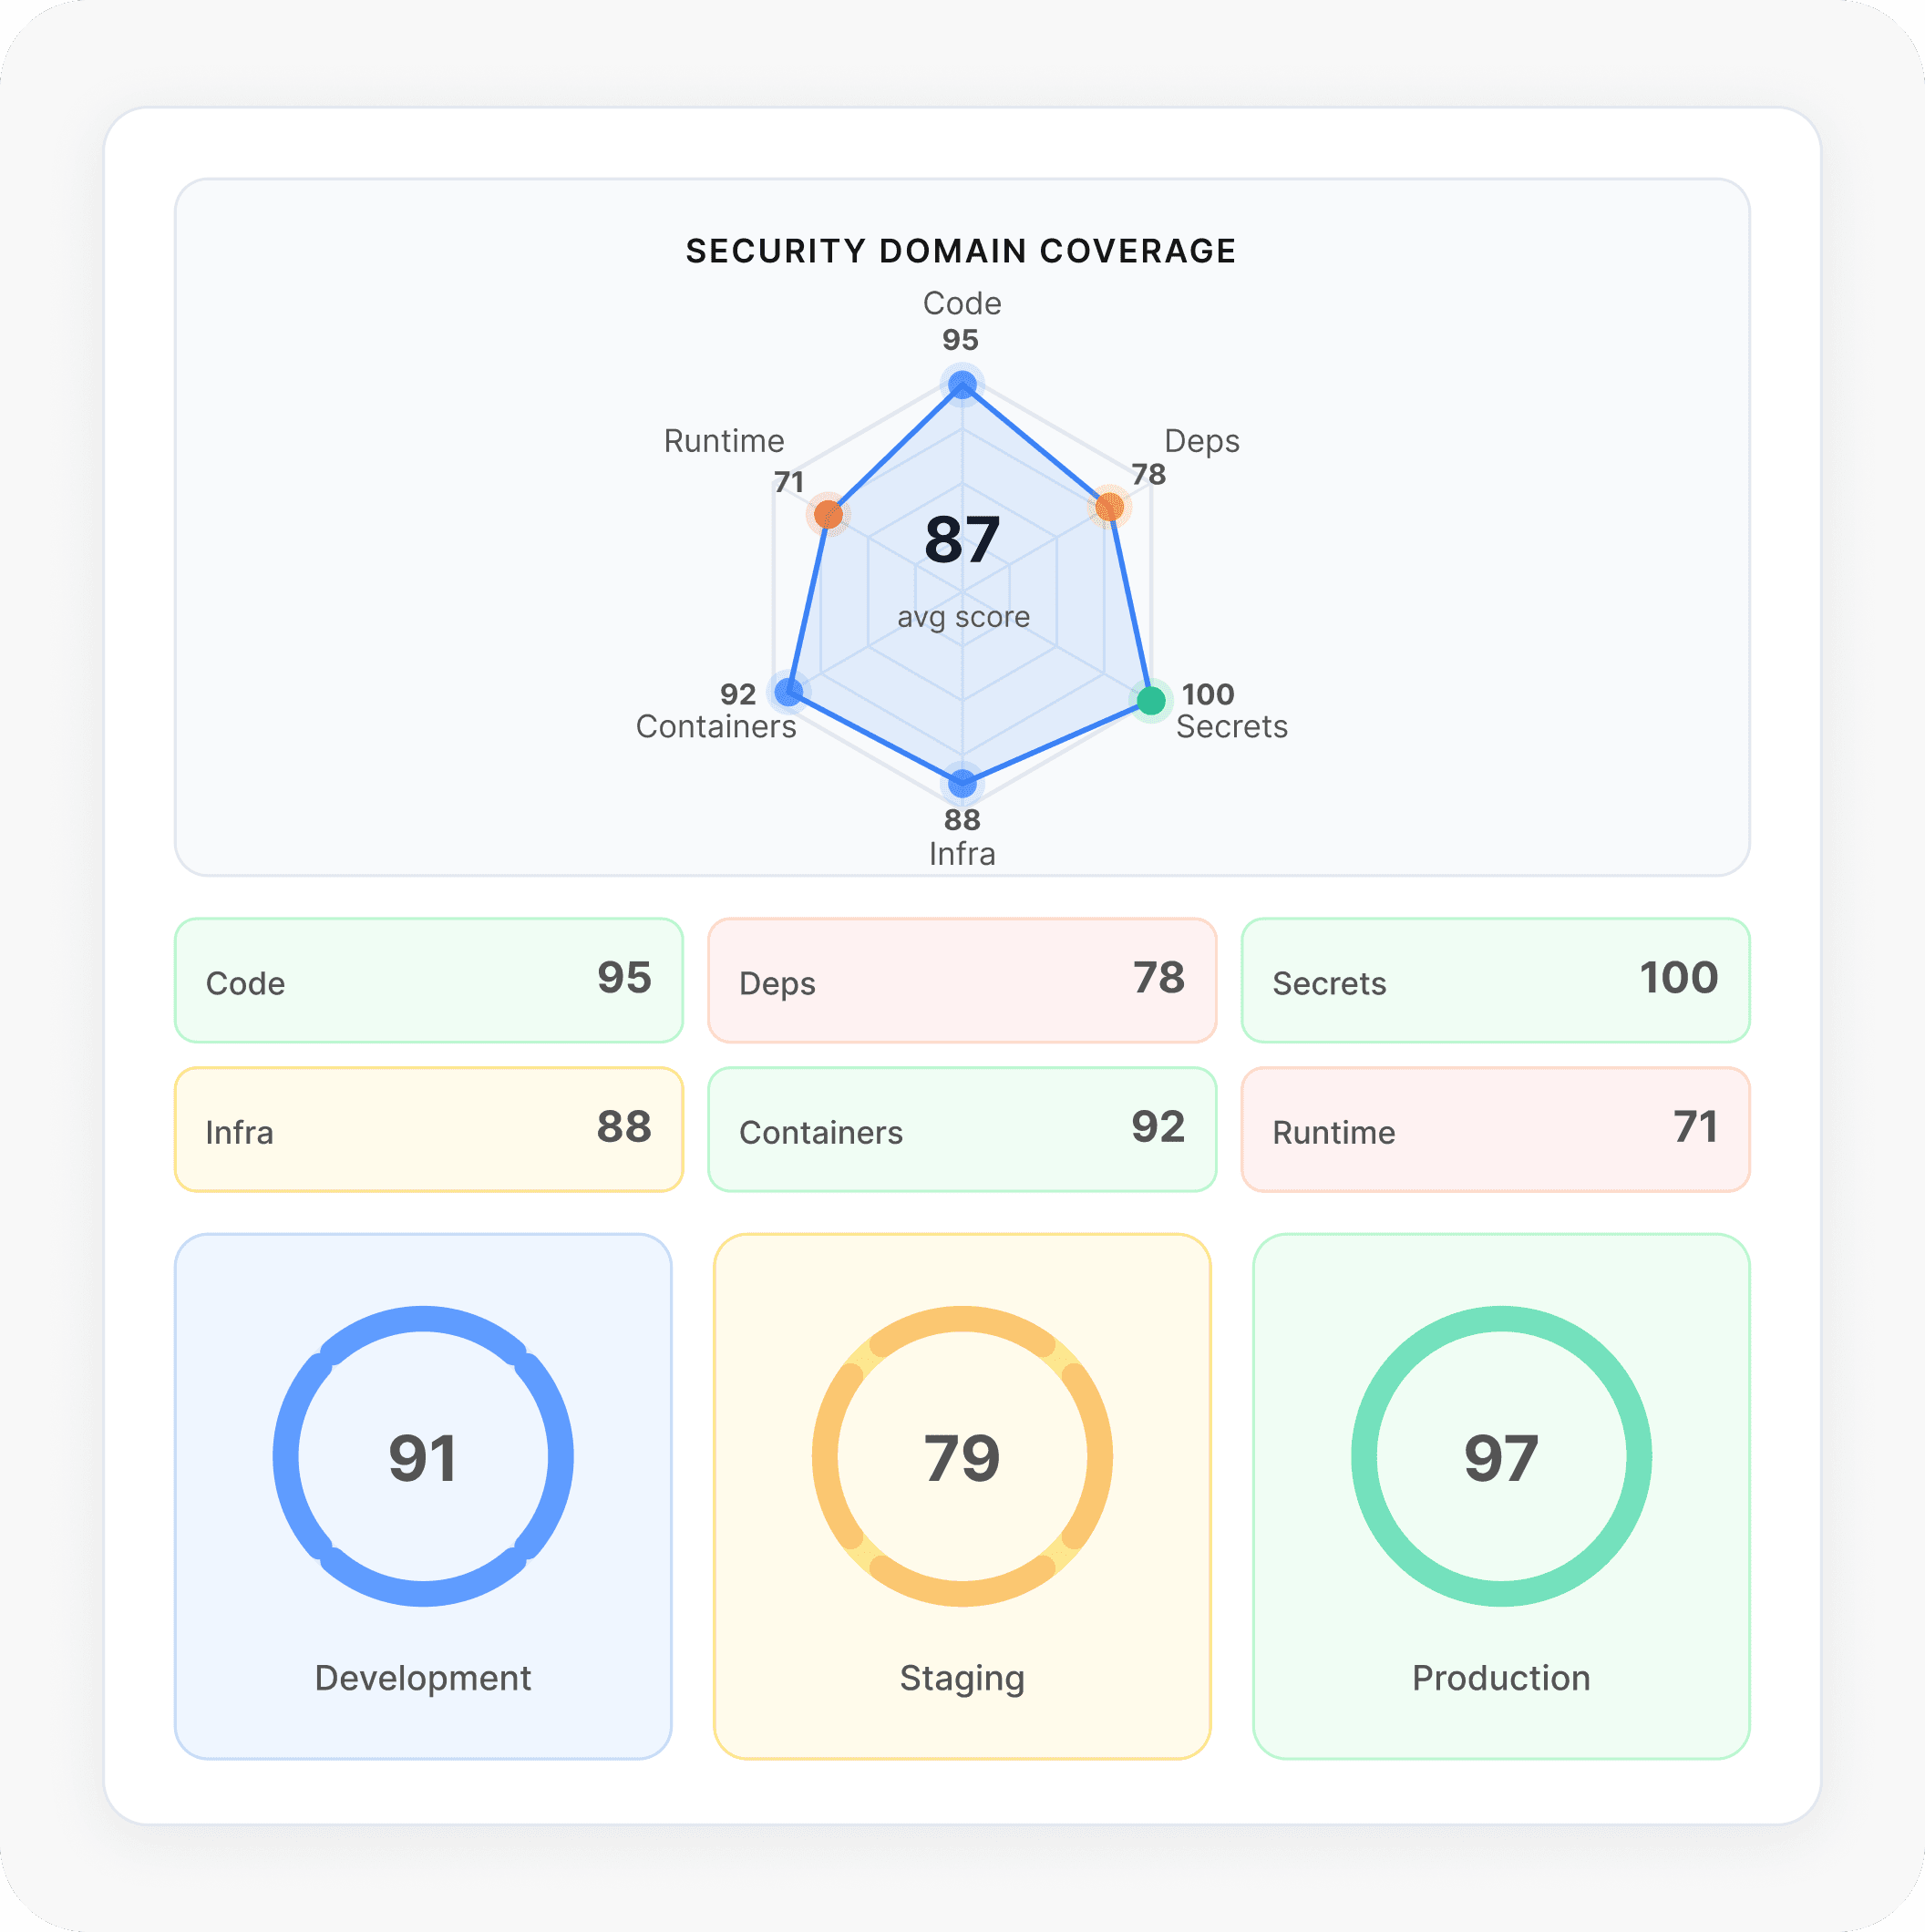
Automated security scanning with findings routed into your delivery pipeline from development environments to production.
Complete Backend Engineering Services for Enterprises and Companies
Industries-Based AWS Cloud Foundations
The controls for a production AWS environment vary by industry. VPC segmentation, encryption standards, logging requirements, and access governance in a regulated healthcare workload share very little with a high-volume e-commerce platform. We design AWS foundations around the specific compliance obligations and operational constraints your organization is accountable for, not a generic landing zone deployed without fully understanding your actual context.
AWS Cloud Foundations by Engineers Who Have Delivered 1000+ Projects
The same senior AWS architects who audit your environment are the ones refactoring your Service Control Policies (SCPs) and Landing Zone architecture. We don't hand off vision to a junior delivery team; the expert you talk to is the expert who codes.
We work across Azure Policy, Defender for Cloud, Bicep, and Entra ID with deep experience in Sentinel and Cost Management. The right tooling is what hits your compliance targets.
Everything delivered is production-ready, policy-enforced, and designed to be operated by your team independently long-term.
Our Latest Thinking
FAQs About AWS Cloud Foundations
We handle everything from initial account assessment to a fully structured AWS environment, including OU design, SCP enforcement, IAM baseline configuration, network segmentation, logging pipelines, and security tooling. The result is a cloud foundation your team can operate and scale without depending on undocumented access patterns or configurations that only one person understands.
Most engagements are completed within four to eight weeks. The timeline is shaped by how many accounts are in scope, the state of your access controls and org structure, and whether compliance certification requirements are part of the engagement brief.
We work from your existing environment. Remediating and restructuring what is already in place is almost always faster. When a more significant change to your account model or network layout is the right call, we make that case clearly and carry out the transition without affecting workloads in production.
That is the intended result. Every engagement is designed to leave your team with foundations they fully understand and can govern. Runbooks, architecture documentation, and policy records ship as standard, not as optional additions.
Having workloads in AWS and having a properly governed environment are entirely different things. Accounts without structure accumulate excessive permissions, shadow resources, and network rules nobody is willing to remove. These issues compound quietly until an audit surfaces them or an incident makes the gaps impossible to ignore.
A governed AWS Organizations structure, enforced SCPs, IAM baseline configuration, network architecture documentation, security runbooks, and a structured handover walkthrough delivered to your cloud engineering team.
We work across AWS Organizations, Control Tower, IAM Identity Center, Terraform, GuardDuty, Security Hub, CloudTrail, and Config. Every tool recommendation is based on your security requirements and operational model, not on what our team defaults to.
Yes. HIPAA-aligned logging pipelines, PCI-DSS-scoped network segmentation, FedRAMP-compatible control mappings, and encryption enforcement are part of how we build for teams operating under regulatory mandates or internally defined security standards and requirements.
Most teams see tangible improvement within the first two to three weeks, with access risk reduced, logging coverage expanded, and account boundaries enforced. Full foundation delivery is typically complete within six to eight weeks.
A new cloud hire needs months before they can safely remediate production security gaps. Our engineers bring that expertise from day one, deliver a documented and policy-enforced environment on a defined schedule, and do it without the recruiting delay, onboarding overhead, or ramp-up period a new hire requires.
