Security and Compliance Basics
Stop Assuming Your Systems Are Secure. Start Knowing They Are.


Client Results and Success
Production-Ready Kubernetes Architecture
The platform was designed to support scalable production deployments with minimal resource consumption, enabling faster environment provisioning and operational stability.
3
environments K8s setup
95%
environments K8s setup
35%
savings over managed Kubernetes alternatives
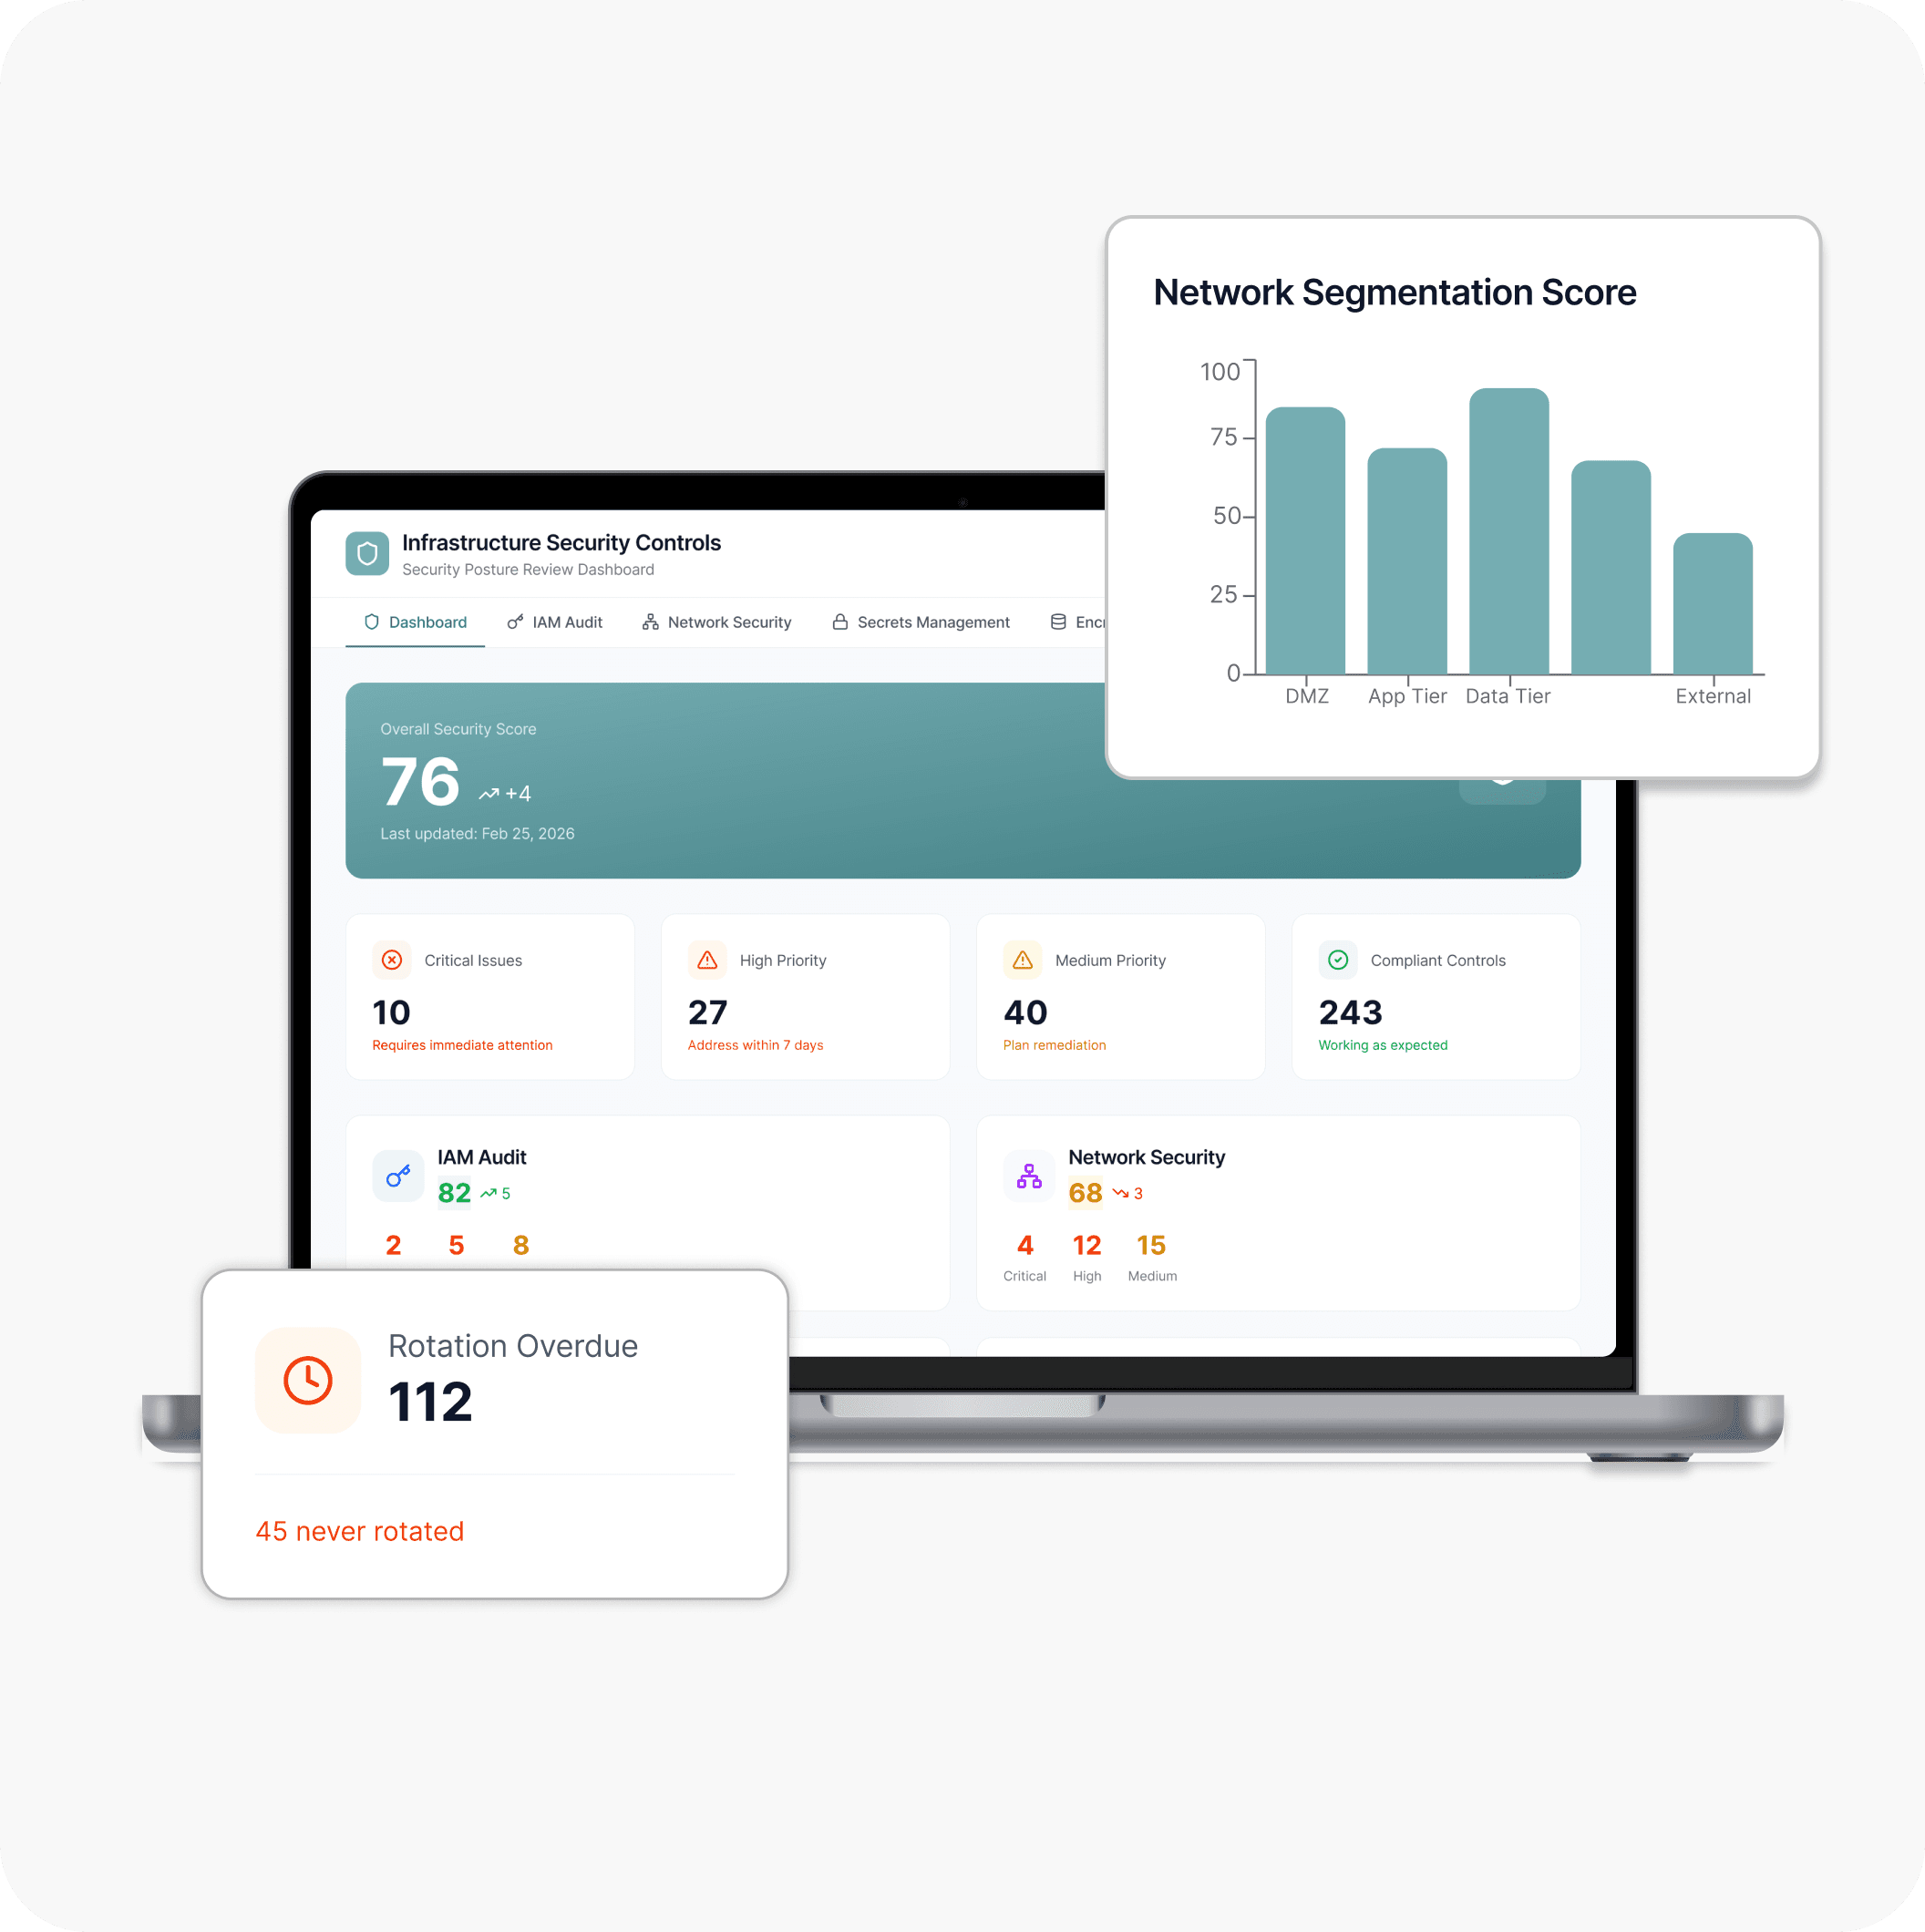
Our Security Assessment Examines Three Foundational Dimensions
- Identity and access management audit: IAM role assignments, privilege escalation paths, service account permissions, and cross-account access configurations
- Network security assessment: Security group rules, firewall policies, publicly exposed endpoints, and internal network segmentation adequacy
- Secrets and credential management: Hardcoded credentials identification, secrets rotation policies, vault configuration, and environment variable exposure risks
- Encryption coverage review: Data at rest encryption configuration, transport layer security implementation, and key management practices
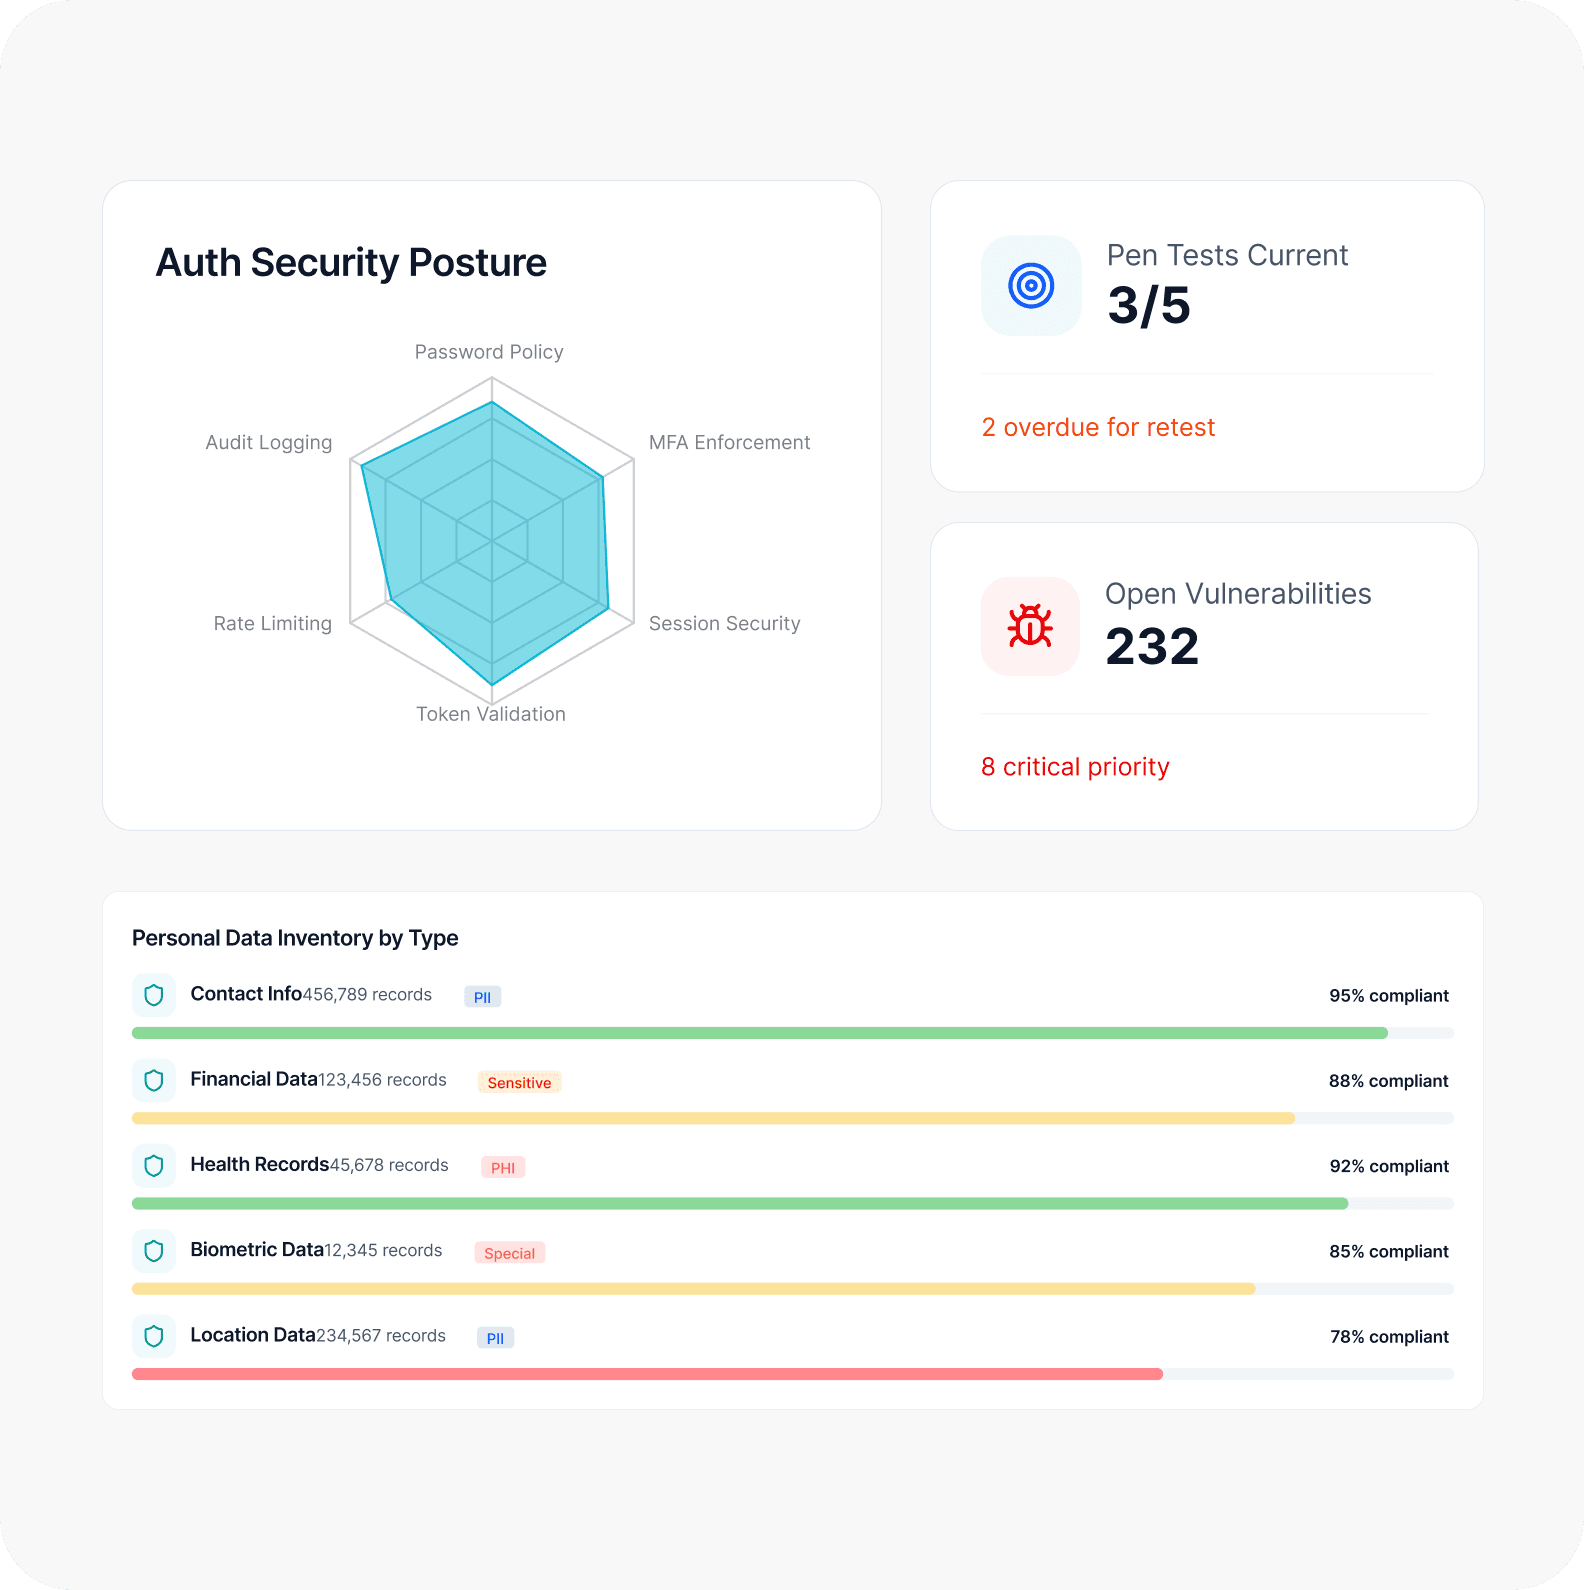
- Authentication and authorization review: Session management, token handling, API authentication mechanisms, and broken access control identification
- Dependency and supply chain security: Third-party library vulnerability exposure, container image scanning coverage, and software bill of materials visibility
- Data classification and handling audit: Personal data inventory, retention policy enforcement, cross-border transfer controls, and data minimization practices
- Security testing integration: SAST and DAST tooling coverage, penetration testing currency, and vulnerability remediation tracking effectiveness
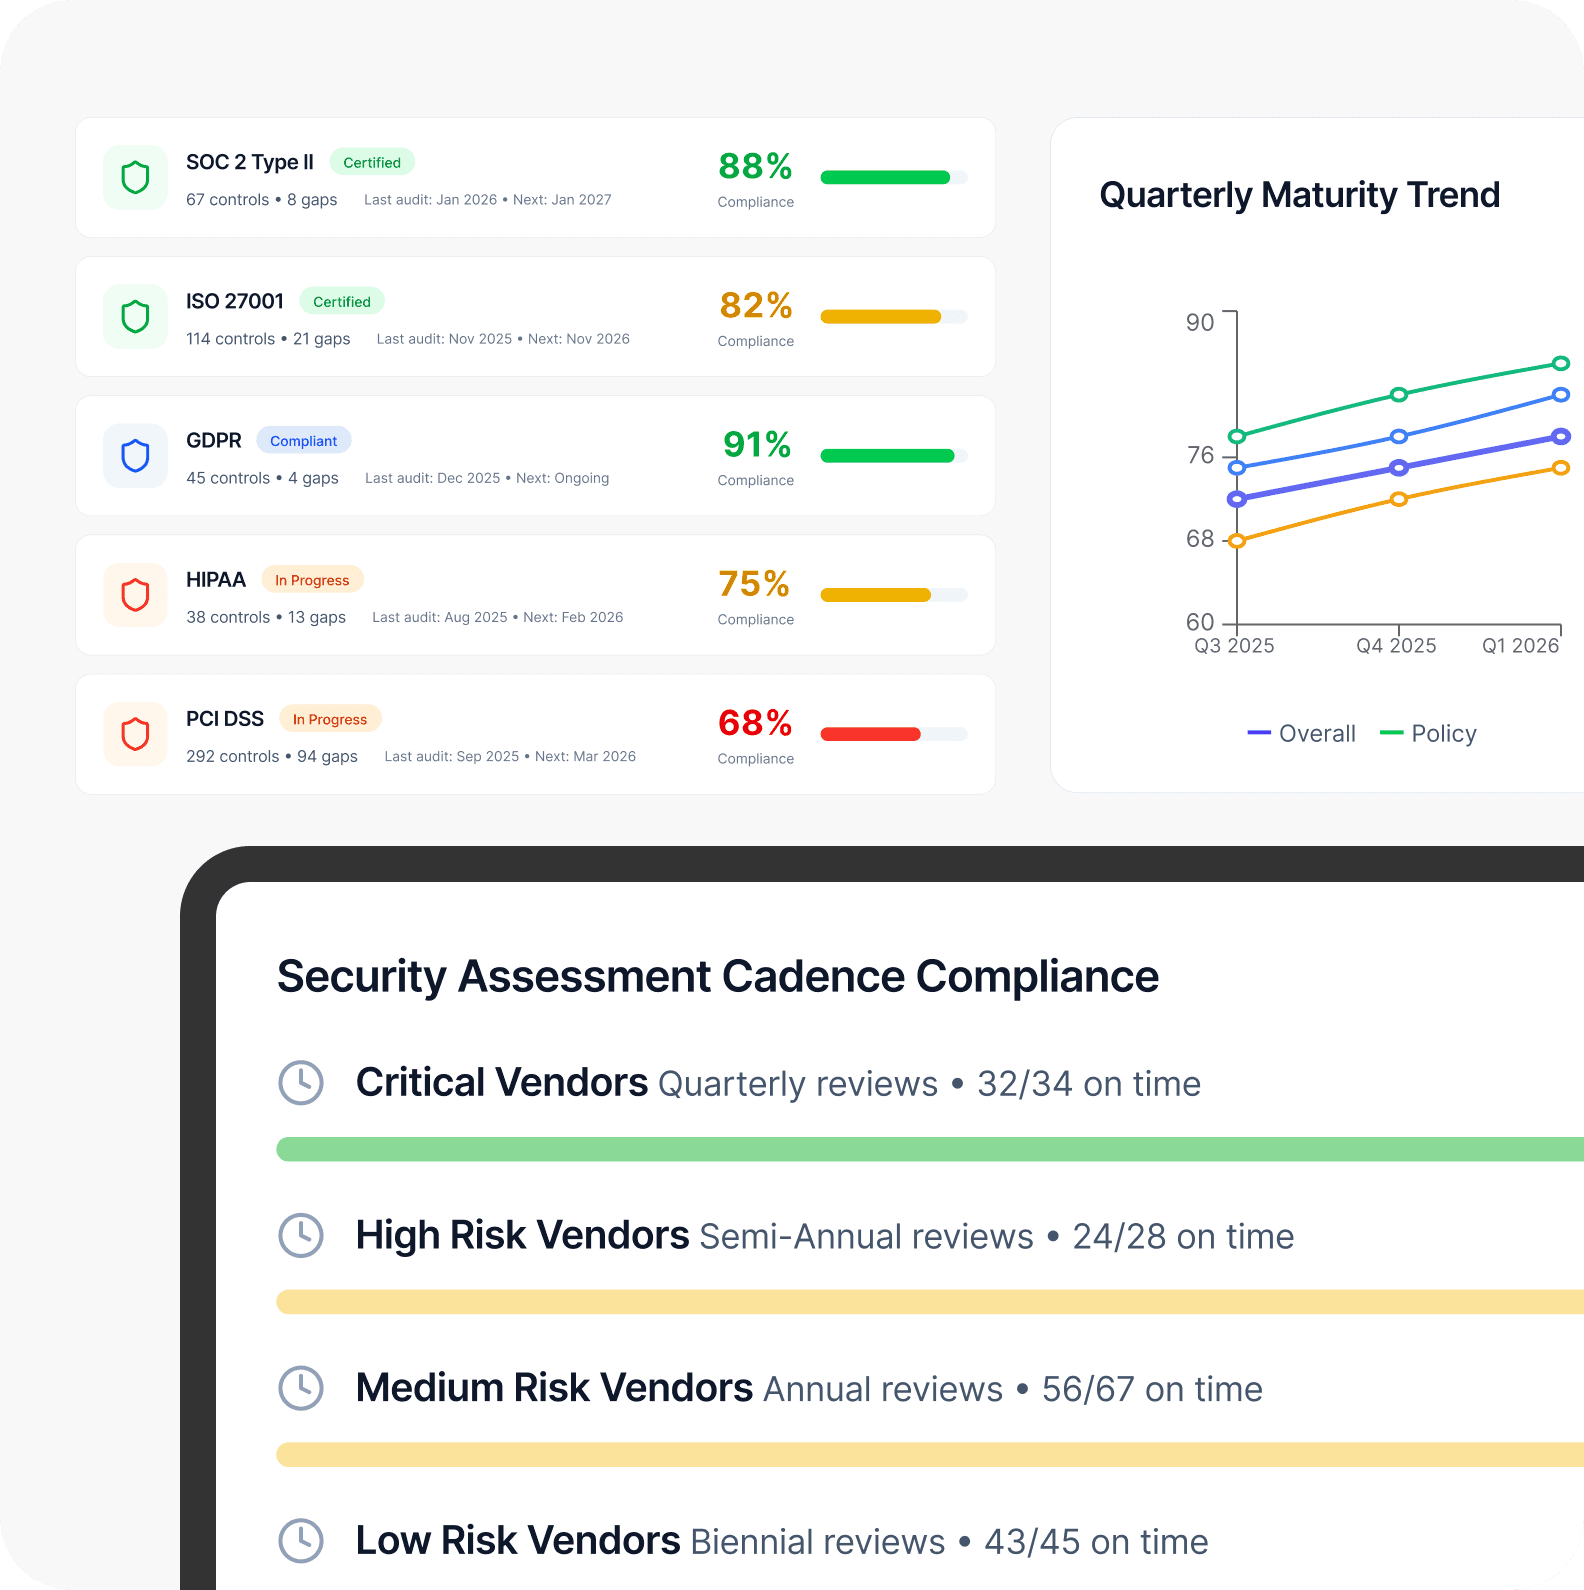
- Regulatory framework mapping: Gap analysis against applicable standards, including SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS based on your business context
- Control documentation assessment: Policy completeness, evidence collection maturity, and audit readiness against your target compliance frameworks
- Vendor and third-party risk: Supplier security assessment practices, data processing agreement coverage, and fourth-party risk visibility
- Security governance maturity: Ownership accountability, security review processes embedded in delivery workflows, and board-level risk reporting adequacy
Security Outcomes We Are Accountable For Delivering
Know Your Actual Security Posture, Not Your Assumed One
Win Enterprise Customers Without Security Reviews Derailing Deals
Protect Customer Data With Controls That Were Designed, Not Accumulated
Meet Regulatory Requirements Before They Become Enforcement Actions
Industries Across Which We Deliver Security and Compliance Impact


Security Assessments Delivered by Engineers Who Have Hardened 1000+ Production Environments
Our Offerings in DevOps Consulting and Services
Our Latest Thinking
What Does a GeekyAnts Discovery Sprint Deliver? Scope, Process, Team, Timeline, and Sample Outputs
When the business idea is clear but the scope, journeys, and technical approach are not, a discovery sprint validates them before you build. Here is what one involves, who takes part, how long it runs, and the outputs you leave with.
ISO 42001 Implementation Guide: How Enterprises Can Prepare for AI Management System Certification
A practical guide to ISO 42001 implementation, certification readiness, AI governance, evidence, audits, and enterprise compliance planning.
GeekyAnts Secures Top 10 Spot in Clutch’s August 2026 Financial App Developer Rankings
GeekyAnts ranks among Clutch’s top 10 financial app developers for August 2026, supported by a 4.9-star rating across 120 client reviews.
US Fintech Compliance Guide: Regulations Every Founder and Developer Should Know
A practical guide to US fintech regulations, compliance requirements, product controls, AI governance, partnerships, and launch readiness, helping fintech teams plan for compliant product development and growth.
Why Legacy Systems Make Business Growth More Expensive: Navigate A Smarter Path to Legacy Modernization
Learn how legacy systems make business growth more expensive and how edge-first modernization can remove constraints without replacing the existing system.
SSO, Audit Logs and RBAC: The Enterprise Features AI Prototyping Tools Do Not Cover | Sarika Gautam
Why AI-generated prototypes fail enterprise review: the context behind SSO, the cost of skipping audit logs, and how role explosion makes RBAC a product of its own.
