Security and Compliance Assessment Services

We examine your infrastructure security posture, access control architecture, and compliance alignment so you gain complete clarity on where vulnerabilities are hiding and what regulatory gaps are exposing your organization to risk. You get the most direct path to building security foundations that protect your systems, your data, and your customers.
4.9Clutch rating
100+Reviews
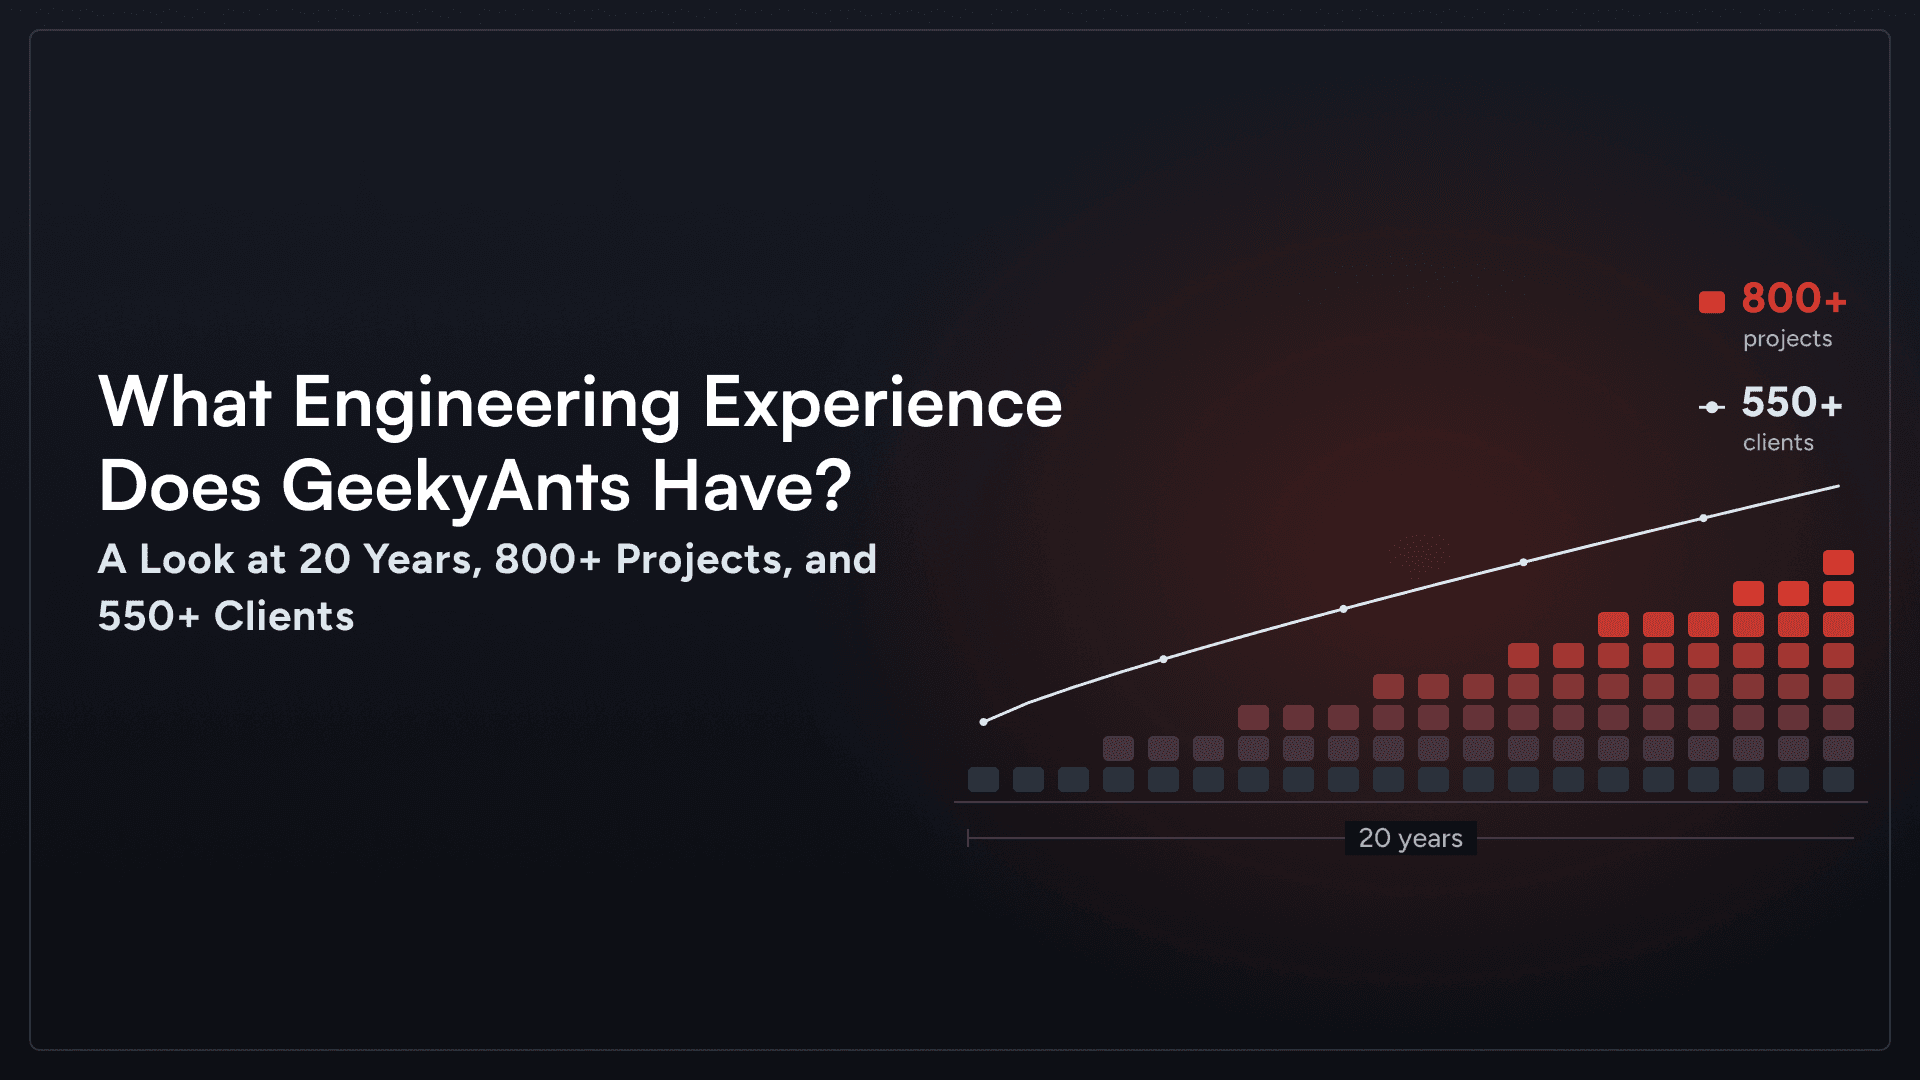
1000+Projects delivered

Free consultation

Stop Assuming Your Systems Are Secure. Start Knowing They Are.

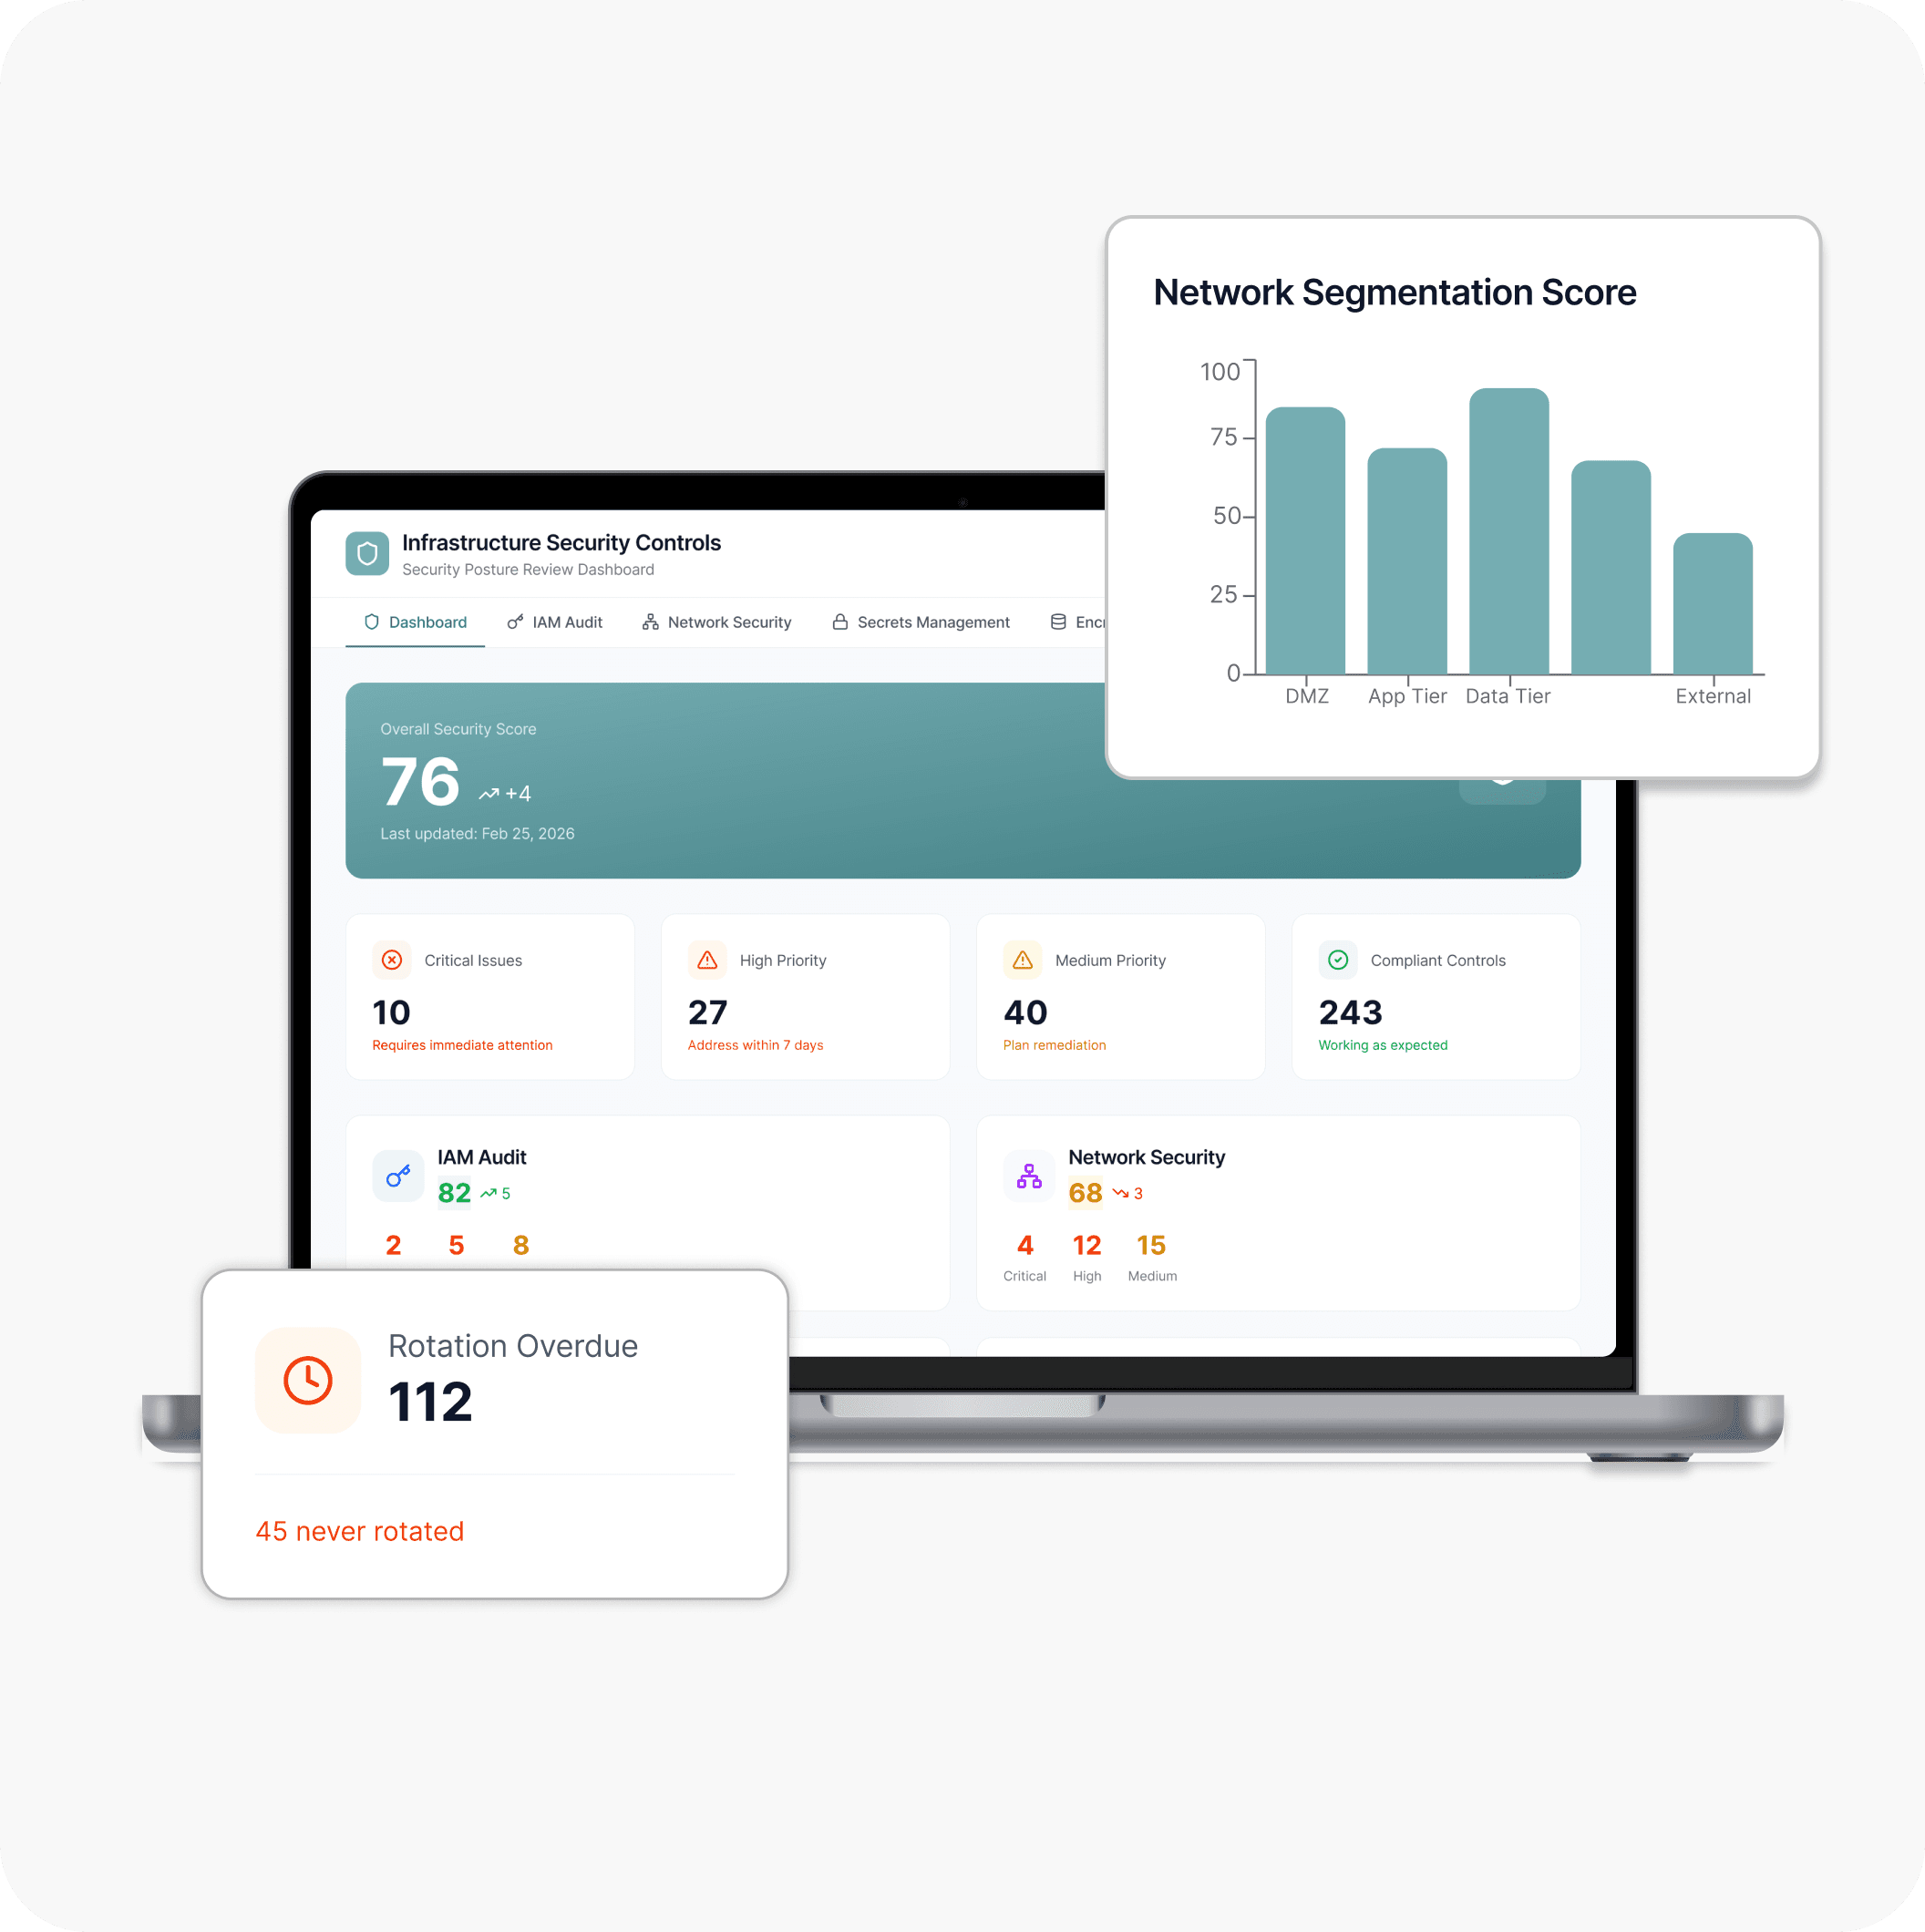
Our security and compliance assessment examines infrastructure configuration, identity and access management, application security, data protection, security tooling, and compliance controls. We review the actual environment to identify verified vulnerabilities, access risks, and gaps between current controls and applicable requirements.

Your security practices become deliberate and documented, audit cycles stop generating emergency remediation work, and the systems you operate genuinely reflect the data protection commitments your business has made to its customers. You leave holding a detailed, prioritized remediation roadmap your team can begin executing without delay.

Work

Client Results and Success

View all
Production-Ready Kubernetes Architecture
Retail Platform for the Nordic Market

Production-Ready Kubernetes Architecture

The platform was designed to support scalable production deployments with minimal resource consumption, enabling faster environment provisioning and operational stability.
environments K8s setup
3
environments K8s setup
95%
savings over managed Kubernetes alternatives
35%
Read case study

WHAT WE DO

What Our Cloud Security Compliance Audit Covers

Every engagement begins with a methodical, evidence-based evaluation spanning three essential pillars of your security and compliance posture: your infrastructure security controls, your application and data protection practices, and your organizational compliance alignment against the regulatory and contractual frameworks applicable to your business.

Our engineers work directly inside your environments, examining your actual IAM configurations, real network policies, genuine secrets management practices, and existing security tooling coverage, rather than relying on scanner outputs and questionnaire responses alone. The outcome is an honest characterization of where your security posture is genuinely robust, where it is relying on assumptions that have never been validated, and where a single misconfiguration or overlooked access path could result in a breach, a compliance failure, or both simultaneously.

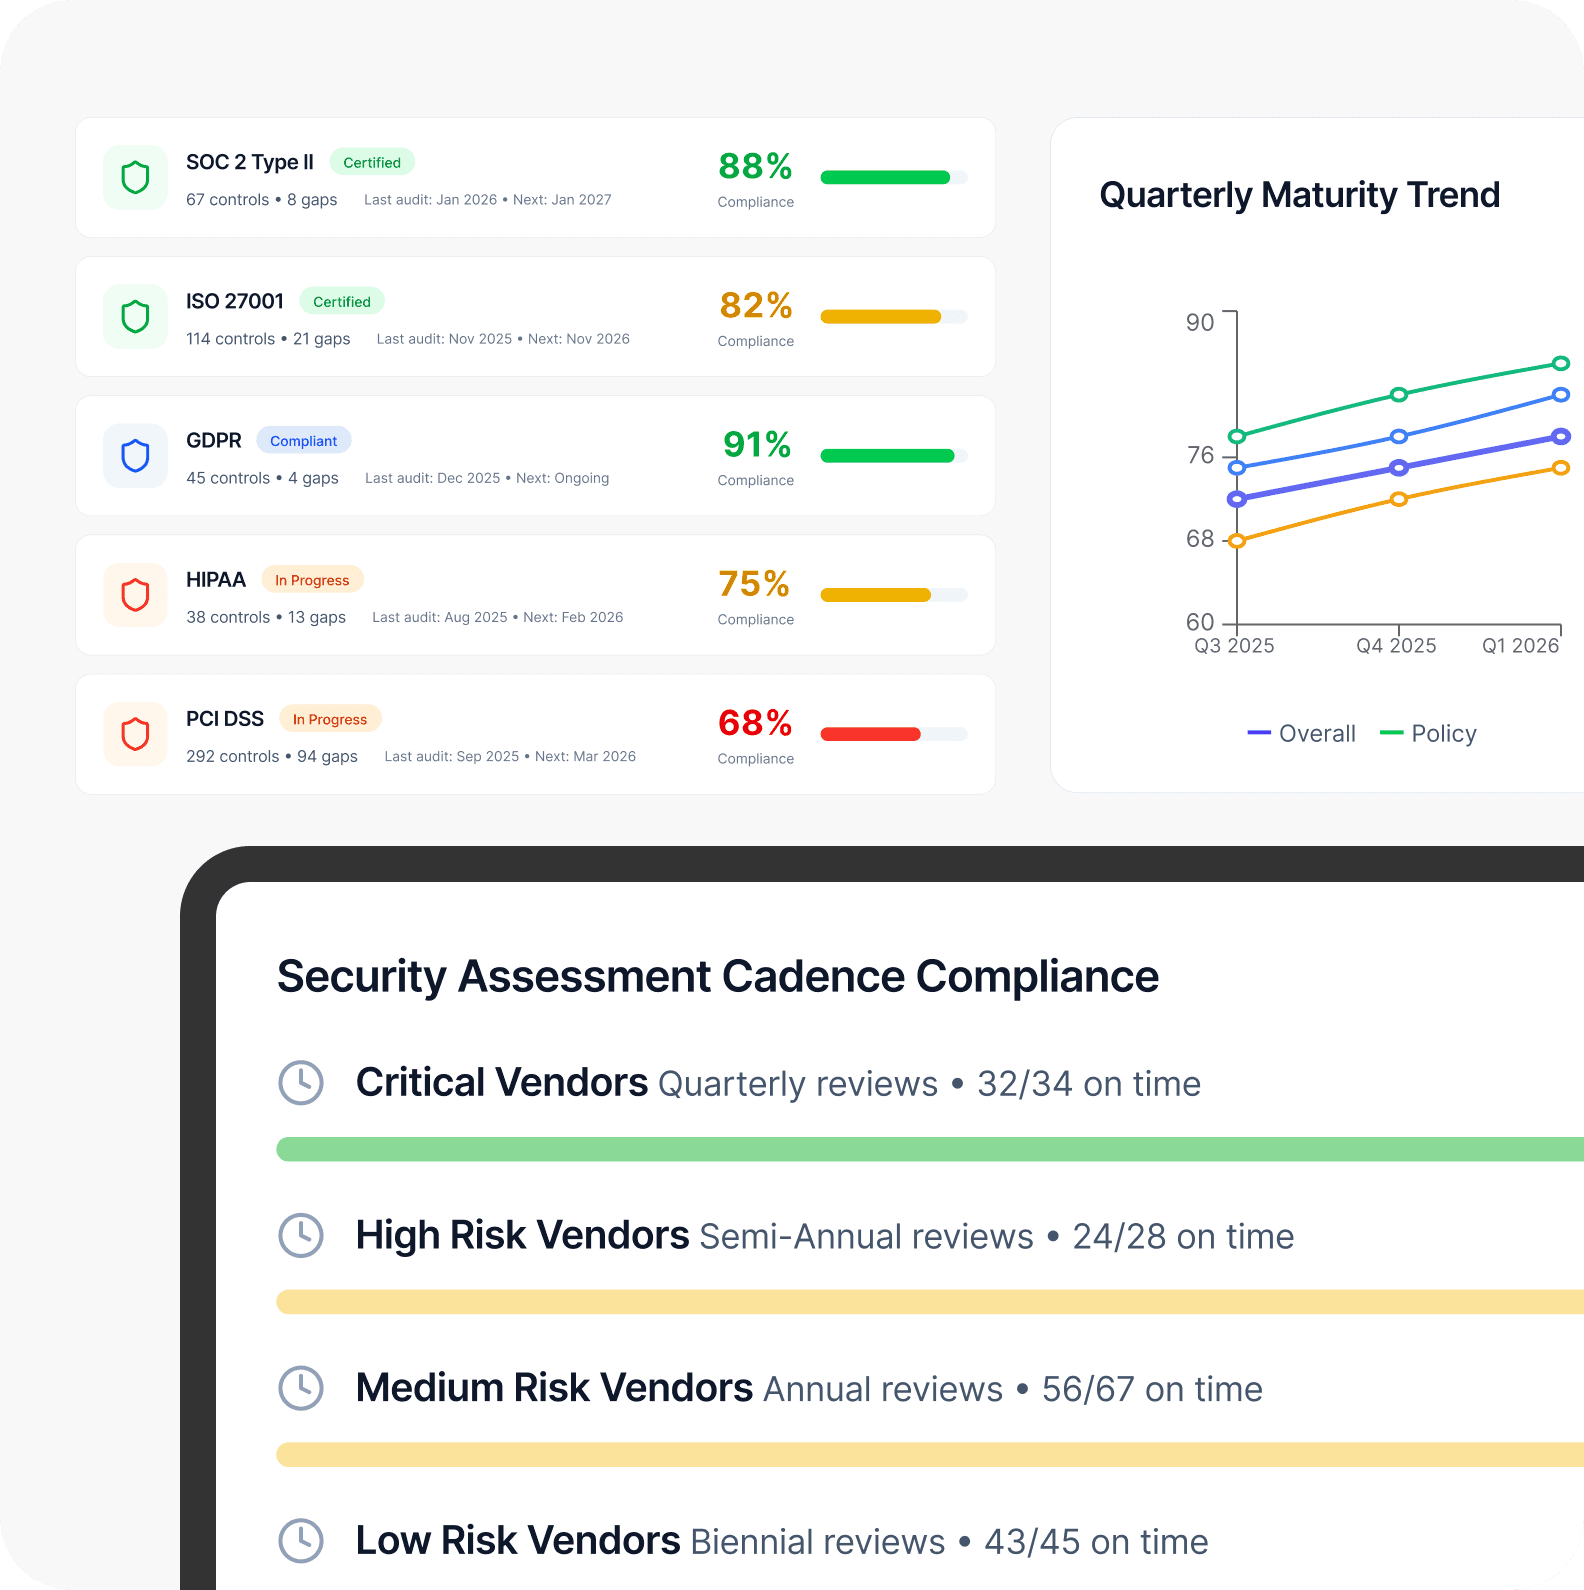
For enterprise SaaS environments, we evaluate these controls against the platform's architecture, customer data, cloud configuration, access model, third-party dependencies, and applicable frameworks such as SOC 2, ISO 27001, GDPR, HIPAA, or PCI DSS.
Our Promise

Security Outcomes We Are Accountable For Delivering

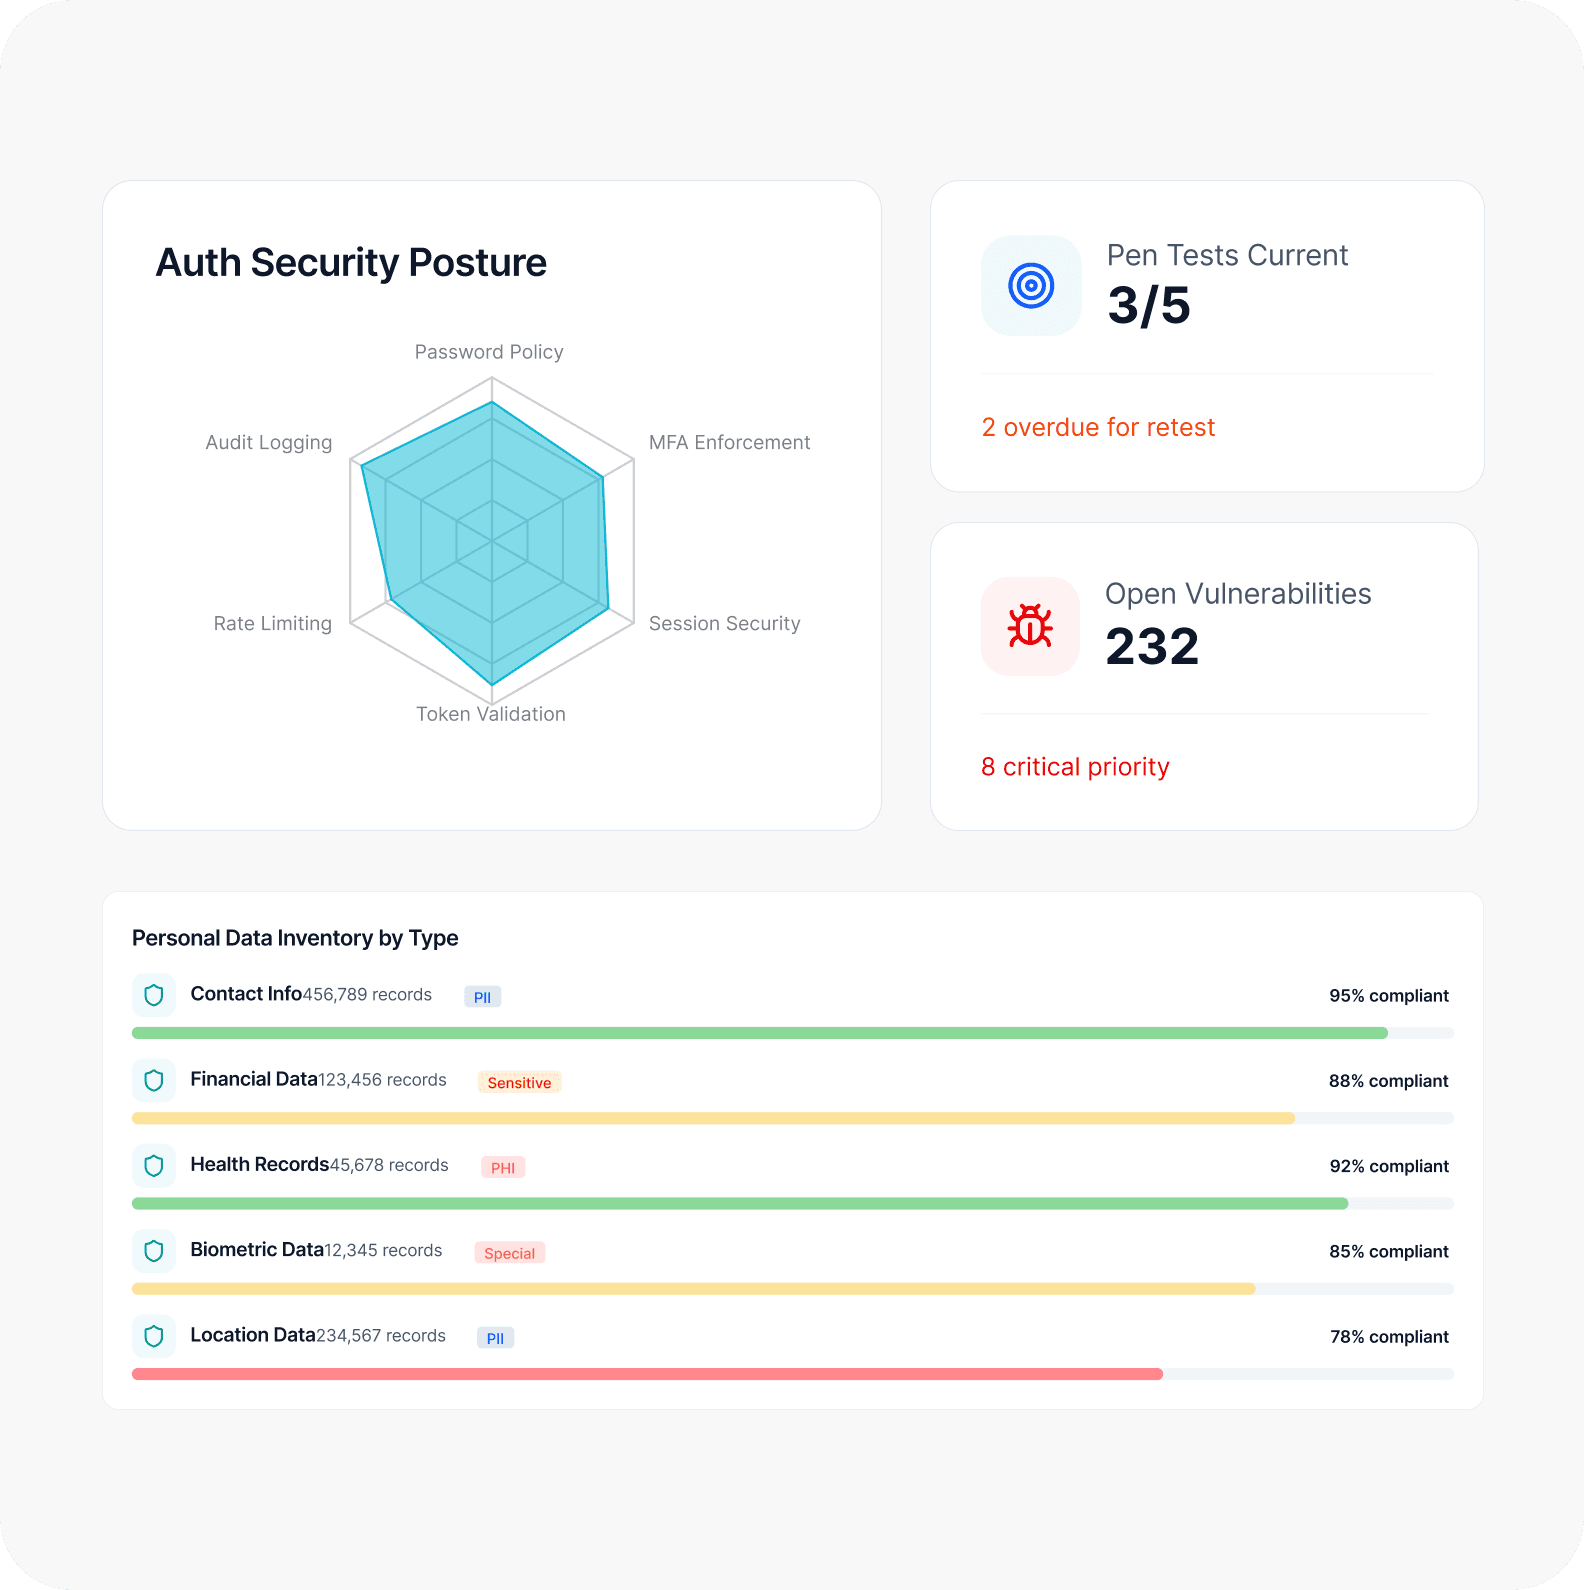
Our assessment documents identified vulnerabilities, misconfigurations, access-control weaknesses, and compliance gaps across the agreed scope. Findings are organized by severity, exploitability, business impact, and remediation complexity so engineering and security teams can prioritize improvements and prepare for customer or regulatory security reviews.
Know Your Actual Security Posture, Not Your Assumed One

Understand every misconfiguration, every access control weakness, and every compliance gap in your current environment — so your security programme is built on verified evidence rather than inherited assumptions about what previous teams put in place.

Win Enterprise Customers Without Security Reviews Derailing Deals

Establish the security controls and compliance documentation your largest prospective customers require so security questionnaires and vendor assessments accelerate commercial conversations rather than stalling them.

Protect Customer Data With Controls That Were Designed, Not Accumulated

Replace the patchwork of security measures added reactively over time with a coherent, layered protection architecture deliberately designed around the sensitivity of the data your platform handles.

Meet Regulatory Requirements Before They Become Enforcement Actions

Align your security controls and compliance documentation to the regulatory frameworks governing your industry and geographies now — while remediation is a planned programme rather than a crisis response.

Industries

Industries Across Which We Deliver Security and Compliance Impact

We develop security strategies calibrated to the threat landscapes, regulatory obligations, and data sensitivity profiles that vary significantly across every industry we operate within. Our approach consistently prioritises building security controls that are sustainable under the pressure of ongoing delivery rather than point-in-time hardening that erodes as systems evolve.We understand the compliance frameworks governing healthcare data, financial transactions, consumer privacy, and critical infrastructure — and the commercial consequences of failing to meet them. Every industry in our portfolio reflects genuine, hands-on security engineering experience.

Why Choose GeekyAnts for Security and Compliance Assessment?

GeekyAnts evaluates security within the broader production environment. Our DevOps engineers review cloud infrastructure, application controls, identity and access, CI/CD practices, observability, reliability, data protection, and compliance requirements as connected parts of the same system.
The assessment can stand alone or inform broader DevOps improvements when findings require infrastructure, delivery, reliability, or operational changes.
Our AI-enabled engineers and security specialists have led security transformation programmes across platforms, handling sensitive financial, healthcare, and consumer data at a significant scale.
Every vulnerability and compliance gap is characterised by its exploitability, its potential business impact, and its remediation complexity — giving your leadership team the context needed to make informed prioritization decisions rather than treating every finding as equally urgent.
We recommend the security controls and compliance investments that your specific threat model, regulatory obligations, and business context demand — never a generic hardening checklist applied without regard for your operational reality.
Every recommendation we produce is specific, testable, and directly assignable — scoped to the actual configurations, policies, and tooling present in your environment rather than described in abstract architectural terms.
We document every finding, every control recommendation, and every compliance mapping rationale so your team owns the security programme fully and can sustain it independently long after the engagement concludes.

Engagement

Our Offerings in DevOps Consulting and Services

DevOps Assessment

Infra, CI/CD & operations health checkRisk, cost & bottleneck identificationClear, prioritized improvement roadmap
Know More

CI/CD and Release Management

Fast, reliable deployment pipelinesSafer releases with easy rollbacksImproved developer delivery velocity
Know More

Cloud Infrastructure Management and Deployment

Day-to-day infrastructure operations & supportStable, secure cloud environmentsReduced operational overhead for teams
Know More

Deployment and Infrastructure Automation

Automated provisioning of infrastructure & deploymentsReduced manual errors and toilConsistent environments across stages
Know More

Infrastructure as Code

Version-controlled cloud infrastructureReproducible and auditable environmentsStandardized app and system configuration
Know More

Containerization and Kubernetes

Application containerizationPragmatic Kubernetes adoptionScalable and portable runtime platform
Know More

Observability- Monitoring, Logging & Alerts

Full system visibility and metricsFaster issue detection and debuggingReduced the production of firefighting
Know More

Cost Optimization and FinOps

Cloud cost visibility and trackingWaste elimination without slowing teamsPredictable and efficient cloud spend
Know More

Cloud Migration and Modernization

Low-risk cloud migrationsLegacy workload modernizationSimplified and future-ready infrastructure
Know More

Scalability and Performance Planning

Traffic and load readiness analysisBottleneck and capacity planningScale-ready architecture guidance
Know More

Reliability and Production Readiness

Production resilience and ownershipReduced outages and deployment failuresSustainable on-call operations
Know More

Security and Compliance Basics

Identity, access, and permission controlsNetwork isolation, traffic restrictions, and encryptionAudit logging and baseline compliance readiness

Insights

Our Latest Thinking

The Hidden Complexity Behind GitOps’ “Push to Deploy”
Nov 6, 2026

Insight

The Hidden Complexity Behind GitOps’ “Push to Deploy”

A GitOps platform that provisioned isolated customer environments straight from Git, and the four problems that surfaced once it was running: dependencies that weren’t ready when resources existed, configuration changes that broke existing tenants, successful deploys that hid broken integrations, and resource limits that blocked work the cluster could handle. The piece documents each fix, the ~110-second provisioning run, and is careful about which numbers are measured observations and which are calculations.

FAQ

FAQs About Security & Compliance Basics Assessment Services

Start a project

The Right Conversation Can Save You Six Months.