

Key Takeaways
- Growth-funded startups need a clear AI inventory to identify which third-party tools, internal systems, AI agents, and employee-led use require stronger controls.
- AI compliance in the United States should connect governance, risk classification, data access, human oversight, testing, monitoring, documentation, and audit evidence across the AI lifecycle.
- US AI compliance obligations can come from federal agencies, state laws, sector regulations, privacy rules, security requirements, contracts, and internal policies.
- AI systems need clear guardrails for data access, system permissions, human approval, incident response, and evidence retention before they scale into production.
Why Is AI Compliance in the United States Becoming an Operational Priority?
AI now sits inside business workflows, employee tools, customer products, and decision systems. McKinsey’s 2025 global survey found that 88% of respondents reported AI use in at least one business function, while 7% reported AI use at full organizational scale. For technology leaders, wider adoption raises questions about which AI systems employees and products use, what company information enters those systems, where that information is processed or retained, and what access each system receives.
For growth-funded startups, this expansion makes AI compliance an operational priority because each use case can introduce regulatory, privacy, security, and governance requirements that need defined controls and ownership.
These questions carry greater weight in the United States because AI oversight comes from several directions. Federal agencies, state laws, sector regulations, privacy laws, security requirements, and voluntary frameworks shape how enterprises manage AI risk. This fragmented environment creates an operational challenge for organizations that build or deploy AI across products and internal functions.
AI compliance therefore needs a connected operating structure. Governance defines ownership and guardrails. Risk assessment identifies exposure across data, systems, users, and business processes. Engineering controls access, testing, approvals, deployment, and monitoring. Documentation captures decisions and control evidence throughout the AI lifecycle. Audit readiness gives the organization records that demonstrate whether those controls operate as designed.
This structure gives technology leaders a defined boundary for AI use and a record of how each system is governed as adoption expands.
In growth-funded and mid-market companies, visibility is where AI governance starts. Leadership needs a clear record of the AI systems in use, the information each system can access, the people accountable for them, and the controls attached to that access. As AI use expands across teams and products, gaps in that record can create questions for security, privacy, engineering, and compliance. A reliable AI inventory gives these teams a common starting point for governance decisions.
 Varun Kumar SahuChief Digital & Privacy Officer
Growth-funded and mid-market companies are expanding AI use through copilots, SaaS features, APIs, agents, and product integrations. Each route can introduce new data flows, permissions, and ownership questions. Technology leaders need a clear view that connects AI use with information access, accountable owners, system boundaries, and production controls. This gives technology and compliance teams a shared basis for risk assessment and governance decisions.
What Is AI Compliance, and How Does It Work Across AI Product Delivery?
Artificial intelligence compliance keeps an AI system aligned with the laws, regulations, standards, contracts, and internal policies that apply to its use. For enterprise teams, compliance shapes how an AI system moves from use-case assessment through development, testing, deployment, monitoring, system changes, and retirement.
AI governance, risk management, compliance, and audit readiness support this process through distinct responsibilities:
Function | Role in AI product delivery |
AI governance | Defines who can approve an AI use case, who owns the system, what data and actions are permitted, and when human review is required. |
AI risk management | Identifies and assesses risks linked to data, model behavior, security, users, vendors, and the business process supported by the system. |
AI compliance | Connects applicable obligations and internal policies with the controls teams follow when they build, deploy, and operate the system. |
AI audit readiness | Maintains records that show which controls were required, who performed them, what evidence they produced, and how teams addressed exceptions. |
The four functions remain connected as an AI system changes. A new data source, model, vendor, user group, or system permission can alter its risk profile. Teams may need to review controls, testing requirements, approvals, documentation, or monitoring in response.
AI compliance should begin during use-case assessment, with AI regulatory compliance requirements identified before development moves forward. Product, engineering, security, data, and compliance teams need defined responsibilities and records of key decisions throughout delivery. This creates a clear connection between identified risks, required controls, assigned owners, completed tests, approvals, and evidence that supports the system’s use in production.
What Does AI Compliance in the United States Require from Growing Companies?
AI compliance in the United States operates across federal oversight, state legislation, sector regulations, privacy laws, security requirements, contracts, and internal policies. The obligations that affect an enterprise depend on the AI use case, the data involved, the people affected, and the locations where the system operates.
At the federal level, enterprises must account for laws and regulatory requirements that apply to the activities supported by an AI system. AI use within healthcare, financial services, employment, or other regulated functions can bring existing requirements for privacy, security, consumer protection, records, or decision processes into the AI control environment.
State activity adds complexity. State legislatures continue to introduce and enact AI measures covering areas such as private-sector use, healthcare, discrimination, and responsible AI use. For growing companies operating across states, AI risk management requires a team to identify which requirements apply to each AI system and connect them to a common set of controls.
Privacy and security requirements also shape AI deployment. Teams need to know what company, customer, or employee data an AI system can access, where that data is processed or retained, which users and systems have access, and what permissions the AI system receives. These questions become critical when enterprises connect AI models, agents, or third-party services to internal data and business systems.
Frameworks can help enterprises organize these responsibilities. The NIST AI Risk Management Framework provides a voluntary structure for managing AI risks across Govern, Map, Measure, and Manage. ISO/IEC 42001 provides requirements for establishing and maintaining an AI management system. Neither framework replaces the laws, regulations, contracts, or sector requirements that apply to an organization.
Growing companies can bring these requirements into one internal control layer. Common controls can cover AI inventory, risk classification, data access, security, human oversight, testing, approvals, monitoring, incident handling, and documentation. Teams can map each applicable requirement to the relevant control and retain evidence that shows how the control operates.
This structure gives technology leaders a consistent way to manage AI governance and compliance across products, teams, jurisdictions, and regulatory requirements.
How Should Companies Build an AI Inventory and Risk Classification for AI Compliance in the United States?
Growing companies need to know where AI is in use before they can assign ownership, assess risk, or apply controls. A central AI inventory captures approved systems and AI use that has not passed through established technology, security, procurement, or compliance processes.
The inventory should cover internal copilots, AI agents, customer-facing AI systems, third-party AI services, embedded AI features, and employee-selected tools. Shadow AI requires attention because teams may adopt tools without security, legal, procurement, or technology review. Third-party AI also requires records of the provider, business purpose, data access, system connections, and permissions.
Each AI system should have a named business owner and technical owner. The business owner remains accountable for the use case and its impact. The technical owner manages system changes, access, testing, and control requirements. Defined ownership gives security, compliance, and engineering teams clear contacts when risks or system changes require review.
How Can Companies Building AI Products Classify Risk?
A simple tier structure can determine the level of governance each system receives:
Risk tier | Suggested classification |
Tier 1: Limited Risk | Internal AI use with restricted data access, limited system permissions, and no role in decisions with material impact. |
Tier 2: Elevated Risk | AI with access to sensitive information, business systems, external users, or workflows that can affect business operations. |
Tier 3: High Risk | AI that supports consequential decisions, handles regulated data, performs sensitive actions, or receives broad system permissions. |
The organization should define the criteria behind each tier based on its business, regulatory obligations, risk tolerance, and AI use cases.
What Should an AI Inventory Capture?
Inventory field | Information to capture |
AI system and purpose | System name, business use case, users, and intended outcome |
AI type and source | Internal copilot, AI agent, customer-facing system, third-party service, or other AI use |
Data and access | Data used, sensitive information involved, connected systems, and permissions |
Ownership | Business owner, technical owner, and teams responsible for review |
Risk tier | Assigned tier based on data, access, decision impact, and affected users |
Control status | Required reviews, testing, human oversight, monitoring, and approvals |
Lifecycle status | Proposed, under review, approved, in production, suspended, or retired |
The inventory becomes part of the governance process. New AI use enters the inventory during intake. Changes to data access, permissions, vendors, models, or business use trigger a review of the assigned risk tier and controls. Technology leaders gain a current record of the enterprise AI footprint and can direct governance resources according to the risk each system presents.
How Should an AI Governance and Compliance Framework Fit Into the AI Lifecycle?
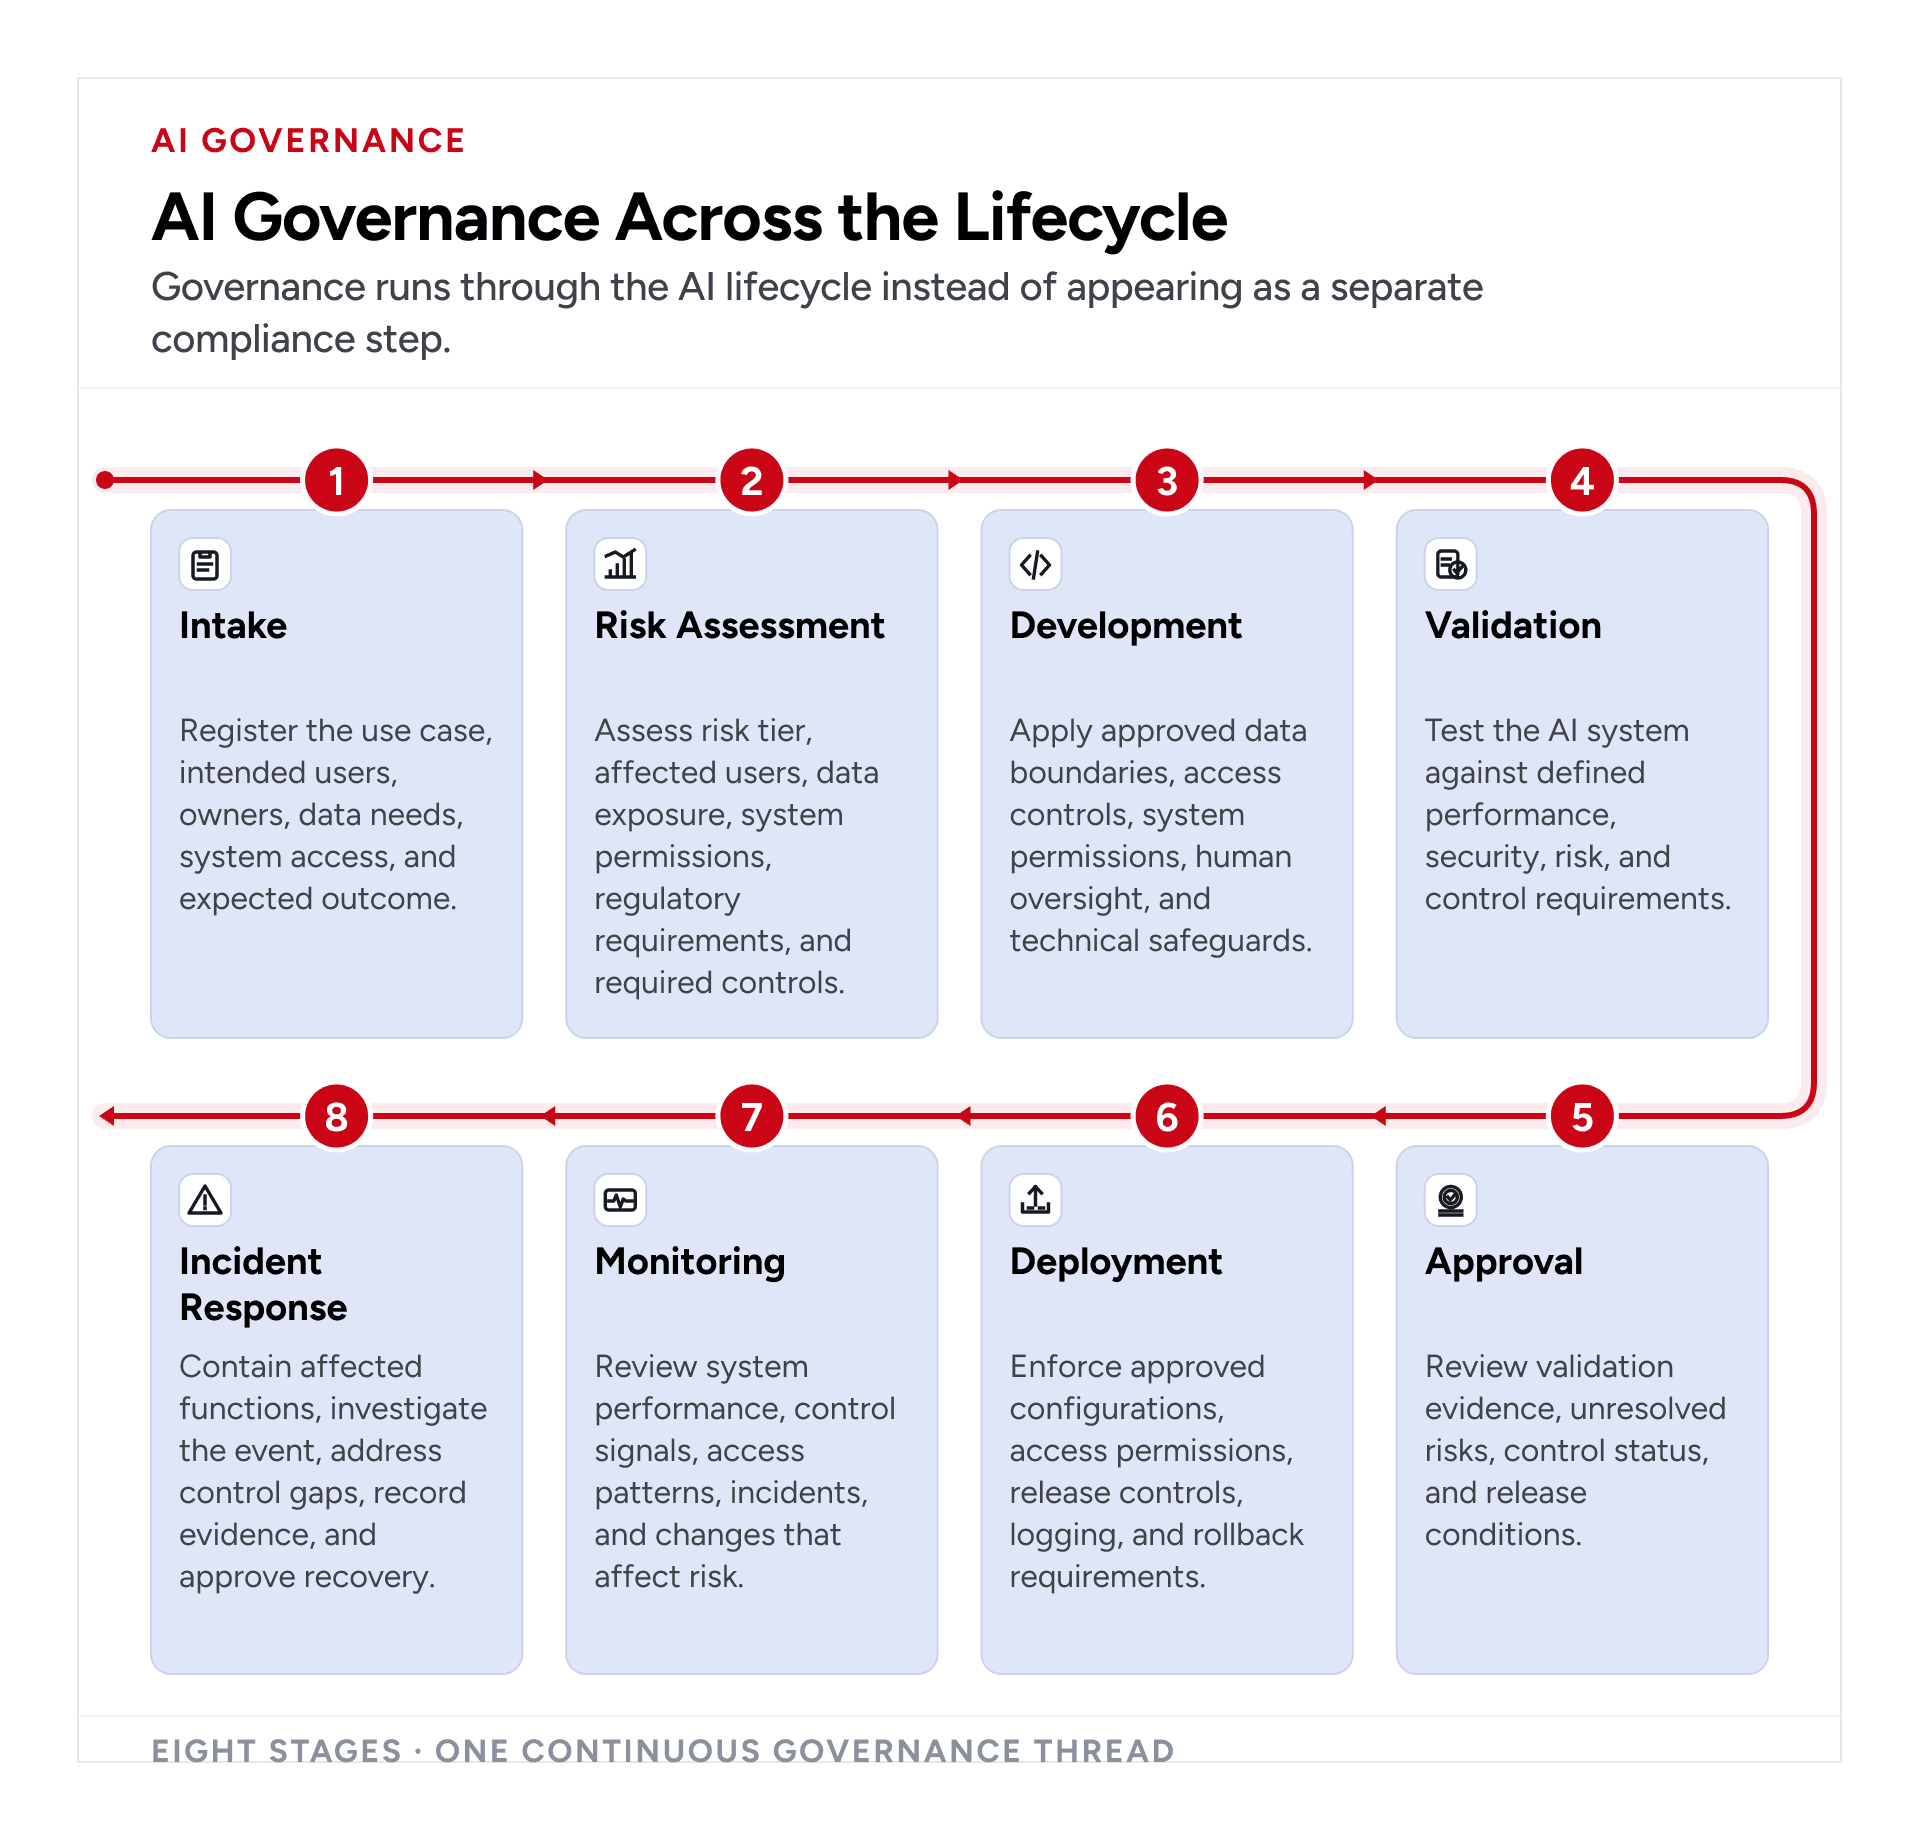
AI governance and compliance should cover intake, risk assessment, development, validation, approval, deployment, monitoring, and incident response. At each stage, product and technology teams need defined ownership, controls, review requirements, and evidence as they build or scale AI-enabled products.
Why Is an AI Governance Policy Alone Not Enough?
A governance policy defines requirements, but those requirements need implementation within the product lifecycle. They should inform architecture, data access, system permissions, human oversight, product design, testing, release controls, production monitoring, incident response, and evidence retention.
This connection helps product and technology teams turn governance requirements into controls they can implement, test, monitor, and document.
How Does AI Governance Work Across the Product Lifecycle?
AI governance applies different controls and review requirements at each stage of the product lifecycle. The checkpoints below show how governance moves with an AI system from initial use-case definition through production monitoring and incident response.
AI Lifecycle Stage | Governance Checkpoint in Product Delivery |
Intake | Define the AI use case, intended users, ownership, data requirements, system access, and expected outcome. |
Risk Assessment | Assess data sensitivity, user impact, system permissions, regulatory exposure, and required oversight. |
Development | Implement data boundaries, access controls, human oversight, security requirements, and product safeguards. |
Validation | Test system behavior, controls, failure scenarios, and human-review requirements before release. |
Approval | Review control results, unresolved risks, exceptions, and release conditions before approving the system. |
Deployment | Apply approved configurations, access controls, logging, rollback procedures, and production safeguards. |
Monitoring | Track system behavior, control performance, access, incidents, and changes that affect risk. |
Incident Response | Contain affected functions, investigate failures, document impact, complete remediation, and approve recovery. |
Who Owns AI Governance Across the Lifecycle?
Product teams define the use case, intended outcome, and user impact. Architecture teams define system boundaries and approved connections. Engineering teams implement product controls, while QA teams validate system behavior and control requirements. DevSecOps and platform engineering teams manage deployment safeguards, access, logging, and production controls. Security teams assess data exposure, permissions, and system risks. Compliance teams connect applicable requirements with controls and evidence. Internal audit teams assess governance and control performance without owning the controls under review.
Governance has value when engineering teams can translate a requirement into a control within the product lifecycle. Data access needs an architectural boundary. Sensitive actions need approval rules. Release decisions need validation evidence. Production systems need monitoring and incident ownership. This connection between governance requirements and engineering controls gives teams a way to manage AI risk through the systems they build and operate.
Varun Kumar SahuChief Digital & Privacy OfficerGrowth-funded startups and mid-market companies need governance embedded within product delivery as they build and scale AI-enabled products. Architecture, engineering, QA, security, and platform teams manage the system boundaries that shape AI risk. Permissions, validation criteria, release gates, logs, monitoring, and incident procedures turn governance requirements into operating controls. Each material requirement should connect to a control, accountable owner, test, and evidence record.
What Documentation Supports AI Compliance in the United States?
Documentation for AI compliance in the United States should give an enterprise a traceable record of each AI system’s purpose, risks, data, controls, testing, approvals, changes, and production history. Documentation should start during system intake and expand as the system changes. Each record should capture evidence from the activity that produced it.
Documentation area | Records to maintain |
Model and system inventory | Current inventory record linking the system to its business purpose, owners, risk tier, deployment status, and approved use |
Risk assessment | Identified risks, affected users, business impact, regulatory considerations, required controls, risk decisions, and accountable owners |
Data documentation | Data sources, data categories, sensitive information, permitted use, access permissions, retention requirements, and data restrictions |
Model documentation | Model or service used, intended use, limitations, approved configurations, system dependencies, and technical decisions |
Testing and validation records | Test scope, acceptance criteria, results, identified failures, remediation records, and release decisions |
Human oversight workflow | Decisions that require human review, assigned reviewers, escalation conditions, intervention authority, and review records |
Change management logs | Changes to models, prompts, data sources, permissions, integrations, configurations, controls, and approved use cases |
Monitoring evidence | Production performance, control results, access records, review findings, identified issues, and remediation status |
Incident evidence | Incident description, affected system, impact, containment actions, investigation findings, corrective actions, and recovery approval |
Vendor documentation | Provider details, contracted service, data-handling terms, security and compliance materials, service changes, and assigned vendor owner |
Documentation should show the relationship between risk, controls, and evidence. An identified risk should have a corresponding control and accountable owner. Validation records should capture the control requirements tested and the results. Monitoring records should capture control performance in production. Material changes to data, models, permissions, integrations, or use cases should produce records of the required review, testing, and approval.
Enterprises can assign documentation ownership to the teams responsible for the underlying work. The documentation process should define the record owner, required evidence, review point, retention requirement, and approval responsibility for each documentation category.
A maintained evidence record gives leadership, compliance teams, internal audit, customers, and external reviewers access to the decisions, controls, tests, changes, and incidents associated with an AI system. Audit preparation can draw from records created as part of product and governance workflows, keeping the evidence connected to the activities it represents.
How Can Organizations Ensure AI Compliance in the United States and Prepare Systems for Audits?
An AI readiness audit for US compliance should assess how well a company connects AI risks, controls, ownership, testing, and evidence. Each material risk should map to a defined control, an accountable owner, a testing requirement, and records that show the control’s performance.
A control-to-evidence map can organize this information for review:
Control record | Evidence to show |
Risk and control mapping | Identified risk, required control, control owner, affected AI system, and applicable requirement |
Operating effectiveness | Test performed, test period, sample or system record reviewed, result, reviewer, and approval |
Audit trail | Approvals, access records, system changes, monitoring records, and decision history |
Exceptions | Control failure, policy exception, affected system, risk impact, owner, and approval |
Remediation | Corrective action, accountable owner, target date, retest result, and closure record |
Operating-effectiveness testing shows whether an AI control performs its intended function in production. Testing can examine required approvals, access restrictions, human review, monitoring records, and corrective actions. The results should show the control tested, the evidence examined, the outcome, and any action required after the test.
Internal audit can provide independent assurance through reviews of control design, operating effectiveness, exceptions, and remediation. Its findings can identify gaps between defined requirements and control performance and give leadership evidence for governance decisions.
Board and procurement reviews have different evidence needs. Board or executive review can focus on material AI risks, accountability, control failures, unresolved exceptions, and remediation status. Procurement review can examine third-party risk assessments, data-handling terms, security requirements, contractual obligations, and vendor evidence.
An audit-ready AI system should provide a traceable path from applicable requirement → identified risk → control → accountable owner → test → result → exception → remediation → closure. That traceability allows reviewers to see what the enterprise required, how the control was tested, what the test found, and how identified gaps were addressed.
Who Should Own AI Compliance in the United States?
AI compliance in the United States requires shared ownership across business and technology functions. Executive leadership sets accountability and risk expectations. Business, product, engineering, platform, security, data, and compliance teams carry defined responsibilities within the operating model. Internal audit provides independent assurance over governance and control performance.
For CIOs and CROs, the ownership model should define decision authority, implementation responsibility, review responsibility, and escalation paths.
Function | Core ownership | Typical RACI role |
Executive leadership | Set risk expectations, establish governance authority, and review material AI risks and unresolved issues. | Accountable |
AI governance committee | Set governance requirements, review high-risk use cases, oversee exceptions, and resolve cross-functional ownership questions. | Accountable / Consulted |
Business teams | Own business objectives, operational impact, and risk decisions tied to the use case. | Accountable / Consulted |
Product | Define intended use, user impact, product requirements, and acceptance criteria. | Responsible |
Engineering | Implement application controls, system permissions, safeguards, logging, and approved technical changes. | Responsible |
Platform engineering | Manage infrastructure controls, deployment requirements, access, observability, and production safeguards. | Responsible |
Security | Define security requirements and assess data exposure, access, system connections, and security risks. | Responsible / Consulted |
Legal and compliance | Identify applicable obligations and connect requirements with policies, controls, reviews, and evidence. | Responsible / Consulted |
Data teams | Define data access, permitted use, quality requirements, lineage, retention, and data controls. | Responsible |
Internal audit | Assess governance design and control performance without owning the controls under review. | Consulted / Informed |
RACI assignments should reflect the decision or control under review. Executive leadership can hold accountability for enterprise risk expectations, while product, engineering, and platform teams hold responsibility for implementation. Security, legal, compliance, and data teams contribute domain review based on the control or decision involved. Internal audit retains an assurance role separate from control ownership.
For CIOs, this ownership model connects product delivery, architecture, engineering, platform operations, security, and governance requirements. For CROs, it establishes accountability for risk decisions, exceptions, remediation, and evidence.
How Can Enterprises Build AI Compliance in the United States in 90 Days?
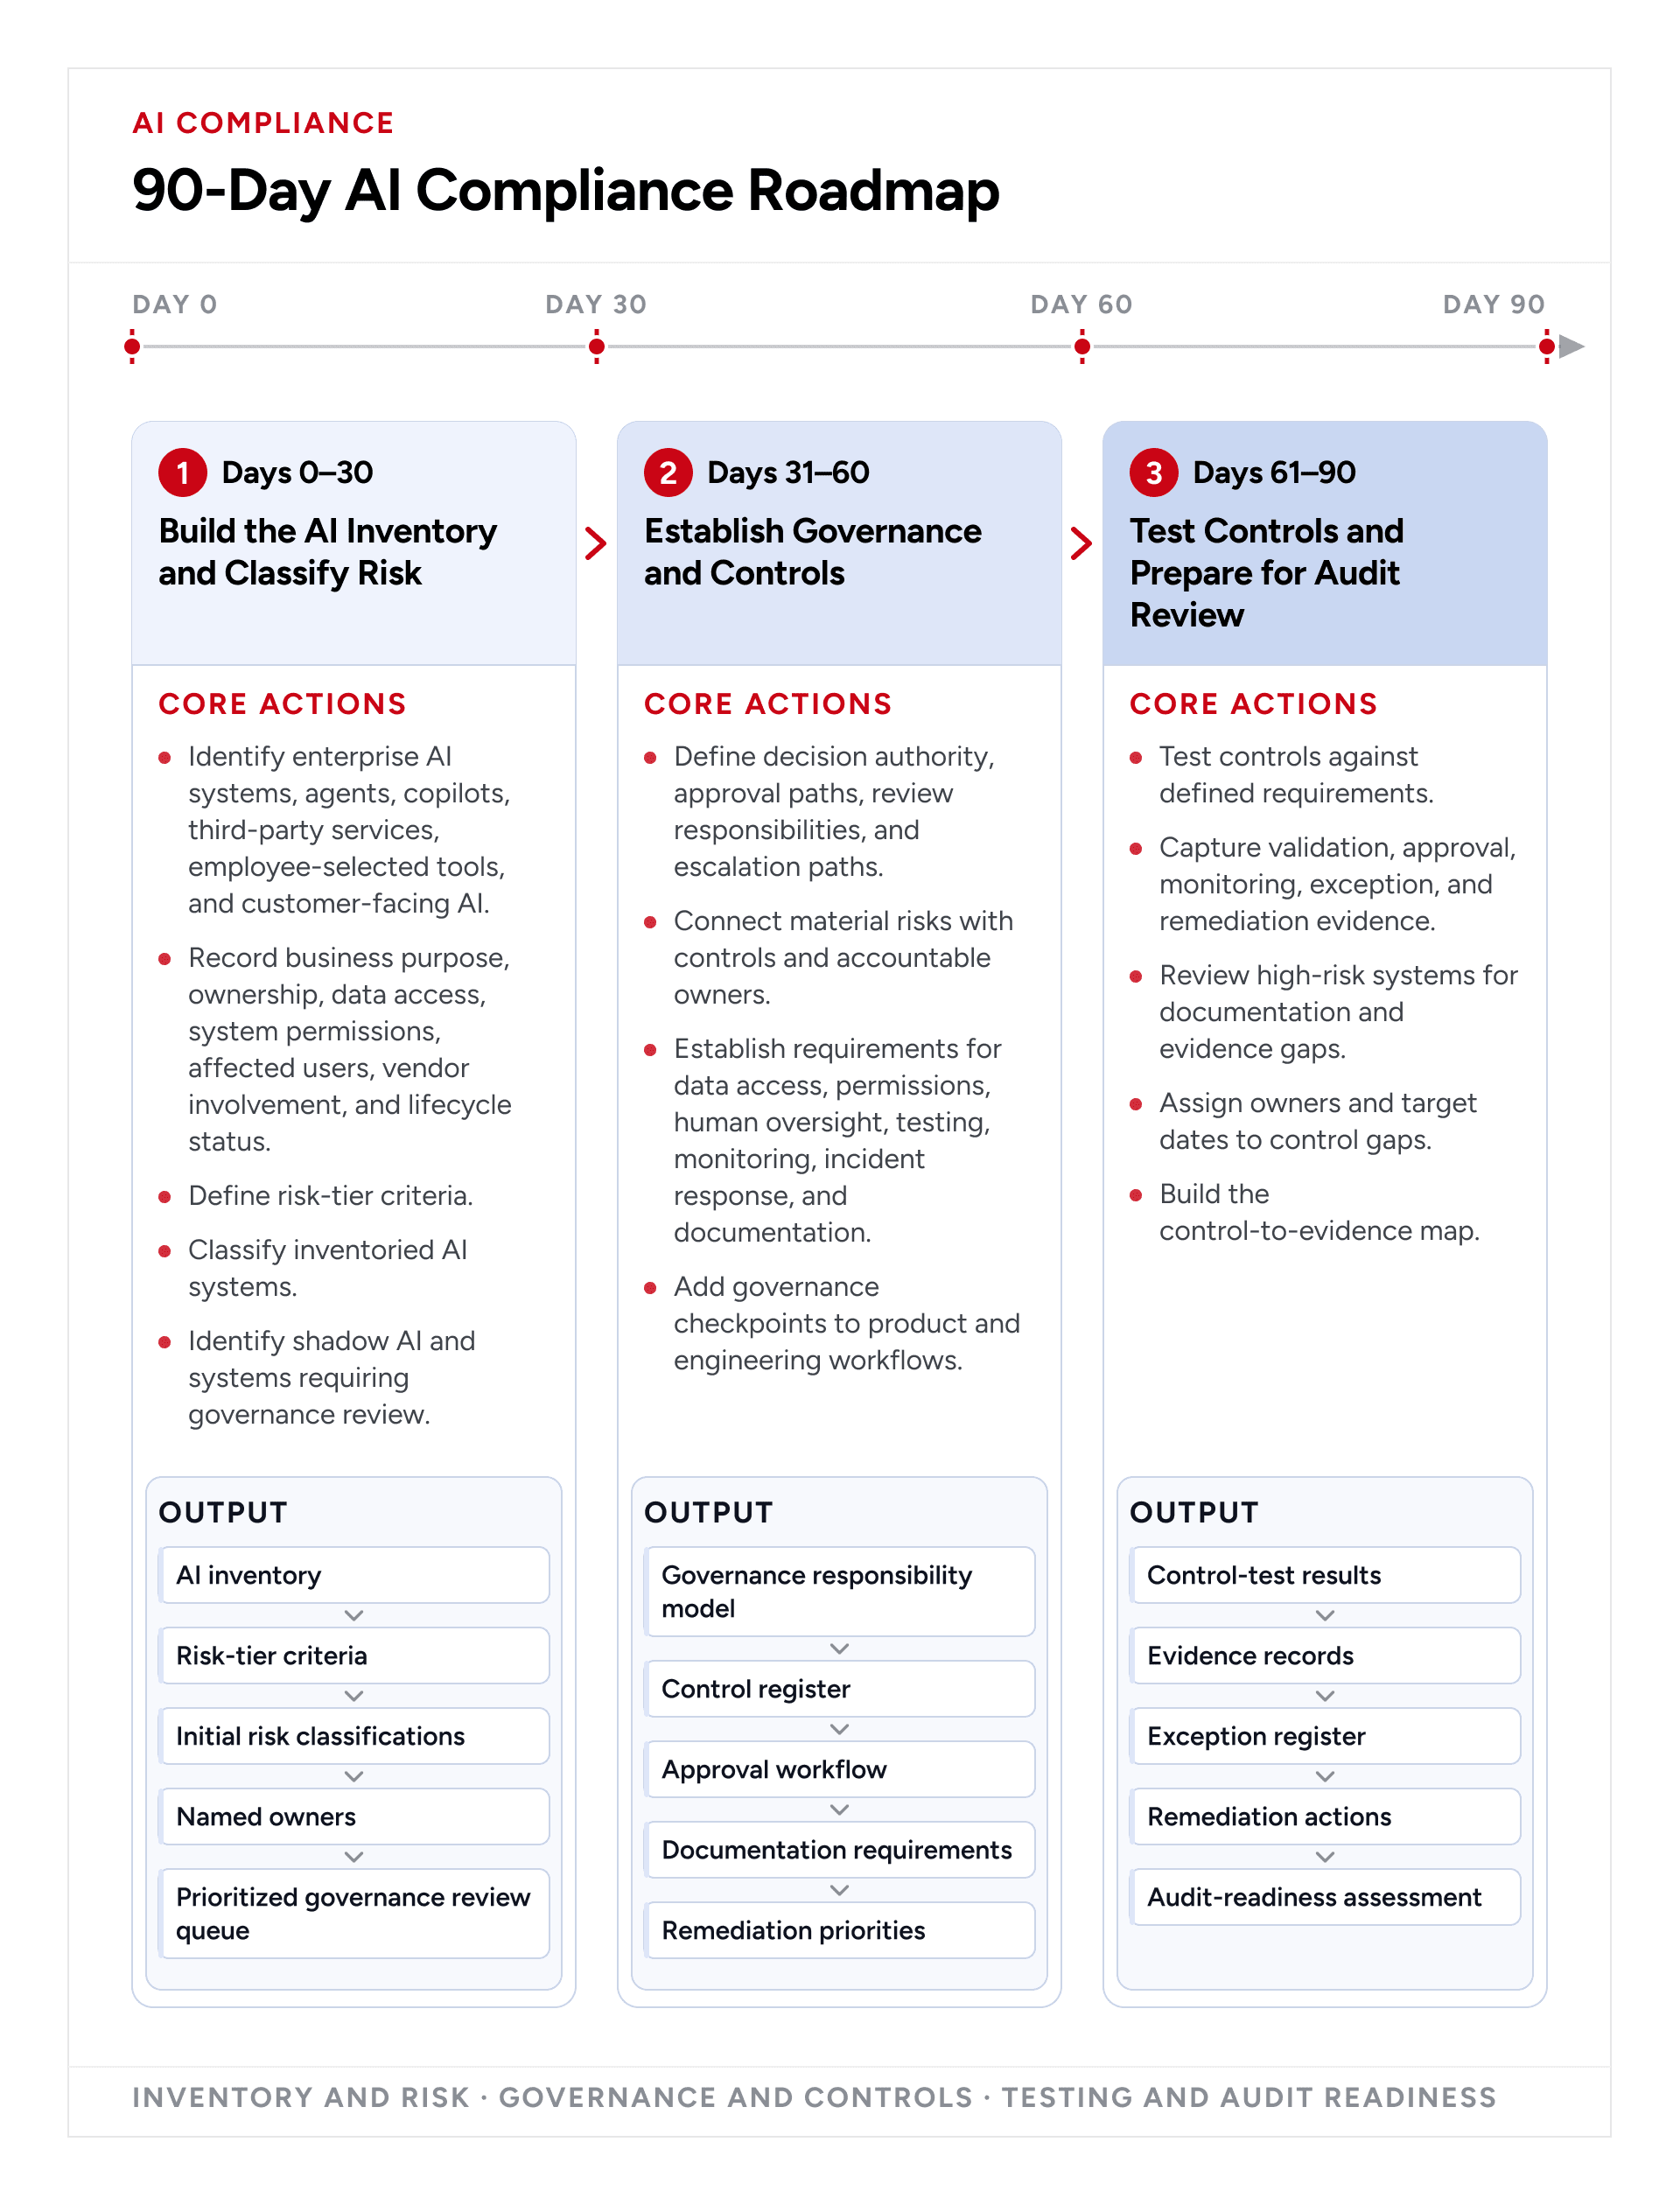
A 90-day roadmap can help growing companies establish an AI compliance framework covering AI inventory, risk classifications, governance controls, ownership, evidence requirements, and review processes. Each phase has defined actions and outputs that prepare the company for the next stage.
Days 0–30: Build the AI Inventory and Classify Risk
The first 30 days establish visibility across enterprise AI use. Teams should identify internal AI systems, third-party services, employee-selected tools, copilots, agents, and customer-facing AI. Each system should have a documented business purpose, business owner, technical owner, data access profile, system permissions, user group, vendor involvement, and lifecycle status.
The organization should define risk-tier criteria based on data sensitivity, system access, decision impact, affected users, and regulatory exposure. Teams should apply these criteria to classify inventoried systems and identify shadow AI or systems that require governance review.
Phase output
AI inventory, approved risk-tier criteria, initial risk classifications, named owners, and a prioritized governance review queue.
Days 31–60: Establish Governance and Controls
The next 30 days connect identified risks with governance requirements and controls. Teams should define decision authority, approval paths, review responsibilities, and escalation paths for each risk tier.
Material risks should connect to controls and accountable owners. Control requirements can cover data access, system permissions, human oversight, testing, monitoring, incident response, and documentation. Product, engineering, security, platform, data, and compliance workflows should contain governance checkpoints that match the organization’s AI risk requirements.
Phase output
Governance responsibility model, control register, approval workflow, documentation requirements, and remediation priorities.
Days 61–90: Test Controls and Prepare for Audit Review
The final 30 days focus on control performance and evidence. Teams should test controls against defined requirements and capture records from validation, approvals, monitoring, exception management, and remediation.
High-risk systems should receive a review for documentation and evidence gaps. Open control gaps should have assigned owners, target dates, and remediation actions. A control-to-evidence map should connect risks, controls, owners, tests, results, exceptions, and remediation records for internal audit, leadership, and procurement review.
Phase output
Control-test results, evidence records, exception register, assigned remediation actions, and an audit-readiness assessment.
By day 90, the enterprise should have an AI inventory, assigned ownership, risk classifications, defined controls, test results, evidence records, documented exceptions, and a remediation plan. New AI use and system changes should enter the established inventory, risk review, control, testing, evidence, and remediation process.
How Can AI Product Teams Assess Compliance Readiness?
AI product teams can assess compliance readiness across ten areas. Each area helps identify gaps in governance, controls, ownership, documentation, testing, and evidence before AI systems move further into production.
1. AI Inventory
Review whether every AI system, agent, copilot, third-party service, and employee-selected tool is recorded with its business purpose, owners, data access, system permissions, vendor involvement, and lifecycle status.
2. Risk Classification
Review whether each AI system has a risk tier based on data sensitivity, system access, decision impact, affected users, and regulatory exposure. Changes to these factors should trigger a new risk review.
3. Ownership
Confirm that each AI system has named business and technical owners, with decision authority, review responsibility, approval authority, and escalation paths defined.
4. Controls
Assess whether each AI system has controls that match its risk tier and cover data access, system permissions, human oversight, security, approvals, and incident response.
5. Documentation
Review whether records capture the system purpose, risk assessment, data use, model or service details, approvals, system changes, incidents, record ownership, and retention requirements.
6. Testing
Confirm that system behavior and required controls have defined test criteria, recorded results, identified gaps, corrective actions, and approval decisions.
7. Monitoring
Assess whether production monitoring covers system performance, control results, access patterns, incidents, and changes that affect the system’s risk classification.
8. Evidence
Review whether each material risk connects to its control, owner, test result, approval, exception record, and remediation evidence.
9. Audit Readiness
Confirm that retained records show control design, test results, approvals, exceptions, corrective actions, and closure status for audit review.
10. Remediation
Review whether each identified control gap has an assigned owner, target date, corrective action, retest requirement, and closure record.
How Can GeekyAnts Support Compliance-Ready AI Product Engineering?
AI governance and compliance requirements need engineering implementation before they can shape a production system. GeekyAnts works as an AI-powered digital product engineering and consulting partner, helping enterprises translate approved requirements into architecture, product controls, testing, security, monitoring, and release processes.
For an enterprise building an AI compliance solution or introducing AI into a regulated product, the engagement can connect risk requirements with product and engineering decisions. This can include defining data and system access, implementing permissions and human review, building test requirements into delivery, establishing production monitoring, and generating technical records from development and release workflows.
GeekyAnts brings 20+ years of product engineering experience, with 1,000+ products shipped across 600+ projects and a team of 350+ product engineers. Its compliance-focused work includes an RBI-led banking domain migration that required validation across 100+ integrations with zero customer disruption. GeekyAnts has delivered a casino platform with KYC, secure payments, and geo-compliance requirements. These engagements provide experience with regulated systems that require engineering controls, validation, security, and continuity.
GeekyAnts can translate approved AI governance and compliance requirements into product architecture, engineering controls, validation workflows, and production systems. Legal, risk, compliance, and audit teams retain responsibility for regulatory interpretation, risk decisions, compliance oversight, and independent assurance.
AI product conversations have shifted toward production questions. Business and technology leaders want clarity on data access, ownership, approval boundaries, security controls, system behavior, and the evidence available for review. Those questions shape architecture and delivery decisions from the start of an engagement. A strong AI use case needs an engineering model that can support the governance expectations attached to its use.
 Kunal KumarChief Revenue Officer
Enterprise buyers are bringing security, privacy, procurement, risk, and engineering stakeholders into AI product discussions. Their requirements can influence architecture, integrations, testing, deployment, monitoring, and documentation. Product teams that account for these requirements during planning can enter stakeholder reviews with defined ownership, mapped controls, and evidence from the delivery process. This gives decision-makers a stronger basis for assessing production readiness.
Conclusion
AI governance risk and compliance in the United States requires a working connection between AI risks, ownership, controls, and evidence. Companies building or scaling AI-enabled products should identify gaps in their current AI environment and assign the controls, owners, and remediation actions needed to address them.
Sources and Citations
- https://www.mckinsey.com/featured-insights/year-in-review/year-in-charts
- https://www.ncsl.org/financial-services/artificial-intelligence-legislation-database
- https://www.nist.gov/itl/ai-risk-management-framework
- https://airc.nist.gov/airmf-resources/airmf/5-sec-core/
- https://www.iso.org/standard/42001